Connect incident.io MCP to your AI agents, securely.
One secured endpoint for every incident.io call your AI agents make, scoped per user, inspected, and logged.Try incident.io MCP now
What your agents can ask once incident.io MCP is connected.
Select the tools your AI agents can call
91 tools from the incident.io MCP schema.
Showing 91 tools
What incident.io MCP exposes
incident.io MCP groups its 91 tools into 13 categories, each with a suggested starting policy.
All 91 tools as JSON, ready to paste.
| Category | Covers | Access | Suggested policy |
|---|---|---|---|
| Extensions | Connectors and their health, plugins loaded from source-control repositories with their skills and sync state, skill feedback and usage, upload URLs, and verifying proposed extension content | Read / Write | extension_plugin_create loads a plugin from a repository, which is instructions the agents then follow. Treat it as a supply-chain control, not a convenience, and verify content before it lands |
| Alerts | Searching and showing alerts, alert sources, counts with workload, tags, attaching and detaching alerts from incidents, resolving firing alerts and declaring an incident from them | Read / Write | alert_resolve silences a live signal and alert_create_incident starts a real incident; alert_tag_apply touches up to 50 alerts in one call |
| Incidents | Creating, searching, showing and updating incidents, aggregate stats across 10 or more dimensions, status update history, posting findings into the incident channel, merging and unmerging, and drafting status page updates | Read / Write | Follow stats then list then show rather than paginating. status_page_update only produces a draft: publishing notifies every subscriber and stays with a person |
| Config & Meta | Organisation config and the resources available to read, custom field values, monitored third-party service status, users, AI data source health, pending AI suggestions, product documentation answers and tool feedback | Read / Write | Read resource_show with resource organisation before filtering or grouping, and custom_field_values before setting a field, since it also says whether a field is settable or derived |
| Maintenance & Pauses | Scheduling windows where matching alerts do not page, counting what a window held back, and pausing a person's notifications so escalations skip them | Read / Write | Both creation tools suppress paging, which is the one failure mode where nothing visibly breaks until an incident is missed. Require approval and bound the duration |
| Actions & Follow-ups | Creating, listing, updating and deleting incident actions, and creating, listing and updating post-incident follow-ups with counts grouped by owner and status | Read / Write | action_delete is the only destructive tool here; follow-ups have no delete |
| On-call & Cover | Listing schedules and their current and upcoming shifts, overriding who is on call for a period or clearing it, and asking for, responding to and managing shift cover requests | Read / Write | schedule_override_create changes who gets paged, including clearing the schedule entirely for a period. Approve it and check the window |
| Escalations | Paging a user or an escalation path, searching and showing escalations with transition history, listing paths and who they would page at each level, acknowledging or declining a page, and paging counts by path, priority and time of day | Read / Write | escalation_create reaches a real person's phone. escalation_path_show is the safe way to see who would be paged before doing it |
| Catalog & Teams | Catalog types such as Service and Team, catalog entries with their attributes, and teams with the escalation paths, alert sources and schedules they own | Read | Read-only. team_show is the quickest way to scope an analysis to one team's surface |
| Investigations | Starting an AI investigation on an incident, steering a running one's hypothesis, downloading a full investigation as an archive, and recording whether it was helpful | Read / Write | Both start and steer are visible to responders: starting posts into the incident channel, and steering appears in the investigation history. investigation_sync pulls the complete evidence set out as an archive |
| AI Agents | Three agent tools: one for on-call queries and schedule management, one for incident investigation and management actions, and one for querying logs, metrics, traces and dashboards | Read / Write | ask and ask_incident are agents that take actions, so a single tool name stands in for an open-ended set of operations. The tool name tells you nothing about what the call does |
| Telemetry & Documents | Discovering the real labels and metric names on a connected datasource, and searching and reading the runbooks, guides, post-mortems and architecture notes synced into Investigations | Read | Read-only, but synced documents come from GitHub, Notion and Confluence, so their content is third-party text; use document_show when the agent has to follow a runbook step by step |
| Analytics | Time to acknowledge and resolve with percentiles, responder hours by person, period or custom field, and starting a structured analysis that downloads playbooks, org config and a report template | Read | time_spent_stats attributes hours to named people, which is employee performance data in most jurisdictions |
Connect incident.io MCP to your AI agent
Four steps, under ten minutes.
- 01
Sign in to NeuralTrust
Open the NeuralTrust platform, sign in and go to Getting started, then Connect your tools.
- 02
Choose your agent
When asked which agent you use, pick Claude Code, Codex, Cursor, Windsurf, Copilot or your own code.
- 03
Connect incident.io
Find incident.io in the tool list and connect it.
- 04
Connect your agent
Follow the steps on screen to add the config to your agent, then send the test prompt.
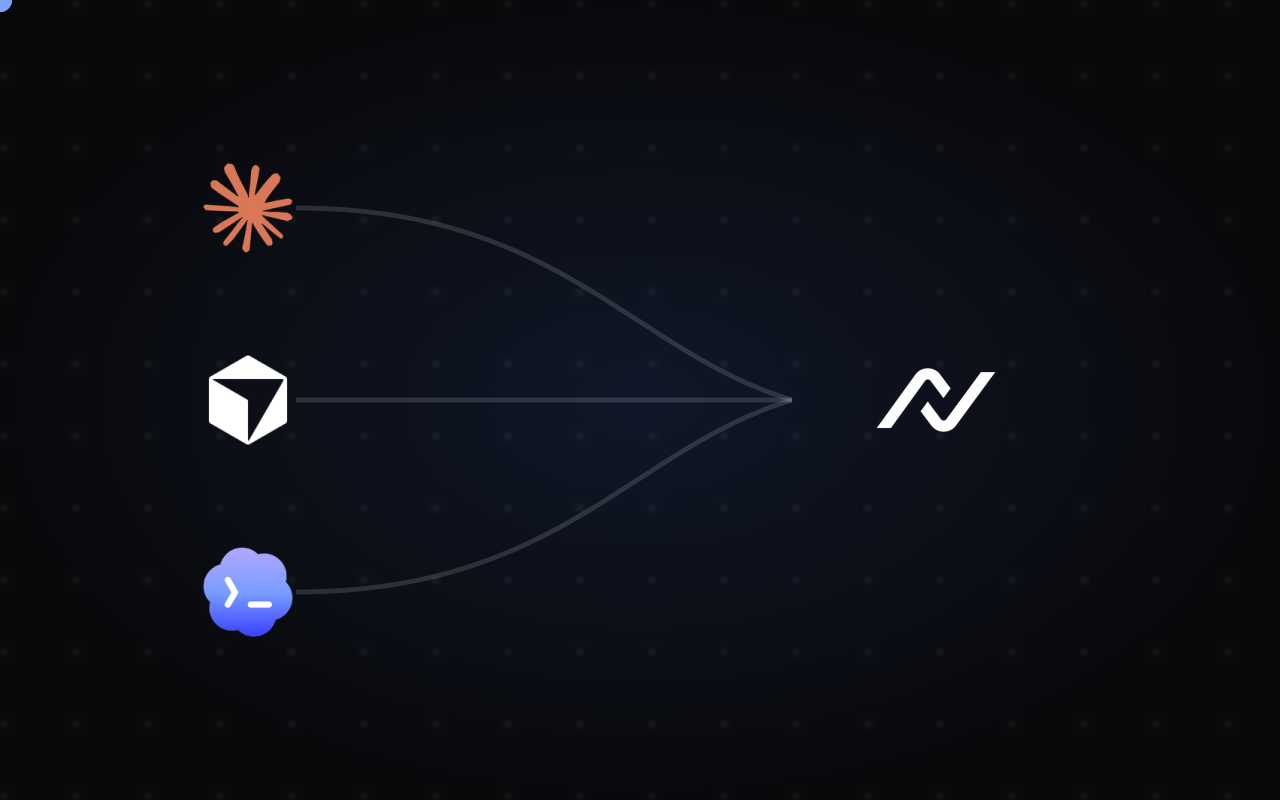
Permissions down to the single tool
You do not allow incident.io MCP or block it. You allow the exact tools each agent can call, one by one.
| incident.io MCP | 91 TOOLS AVAILABLE |
|---|---|
| Code review agent | 4 tools, read only |
| Issue triage bot | 9 tools |
| Platform team assistant | all 91 tools |
- Tool by toolConnecting the server is not the unit of access. Each tool is granted on its own.
- Default denyA tool you have not enabled is never exposed to the agent.
- Approval on writesTools that change or delete things can require a human to confirm.
Is incident.io MCP secure?
One endpoint instead of raw credentials. Every call is checked against policy and logged.
| AI agentsConnect through your MCP client configuration. | NeuralTrustApply controls based on your configuration. | incident.io MCP91 documented tools. Some require the Response, On-call or Investigations product: they still appear in the tool list but return an error explaining what the account is missing. Team, Pro and Enterprise plans only. |
|---|---|---|
| Coding assistants | Connection & credentialsper user | Extensions11 tools |
| Internal copilots | Tool access policiesdeny by default | Alerts10 tools |
| Workflow automations | Request & response inspectioninline | Incidents10 tools |
| Compatible MCP clients | Activity monitoringalerts and logs | All other tools60 tools |
Use incident.io MCP with any AI agent framework
Setup guides for the tools your team already uses.
 Claude CodeAdd incident.io MCP to Claude Code from the terminal
 CursorUse incident.io MCP tools inside Cursor's agent
 CodexConnect incident.io MCP to the OpenAI Codex CLI
 WindsurfGive Windsurf's Cascade access to incident.io MCP
 Gemini CLICall incident.io MCP from Gemini CLI prompts
 Google AntigravityLet Antigravity agents work with incident.io MCP
 GitHub CopilotUse incident.io MCP in Copilot agent mode
 Claude EnterpriseRoll out incident.io MCP across your Claude workspace
 Microsoft Copilot StudioAdd incident.io MCP as a tool for Copilot Studio agents
 Open WebUIBring incident.io MCP tools into Open WebUI chats
 LangChainLoad incident.io MCP tools into LangChain agents
 HaystackPlug incident.io MCP into Haystack agent pipelines
 Strands AgentsGive Strands agents incident.io MCP tools
 Vercel AI SDKCall incident.io MCP from Vercel AI SDK apps
 n8nUse incident.io MCP in n8n AI agent workflows
Common questions about running incident.io MCP through TrustGate.
Other MCP servers
More servers from the catalog.

PagerDuty
Securely connect your AI agents to PagerDuty through TrustGate: incidents, on-calls, schedules, services, escalation policies, teams and status pages, scoped per agent and logged.
18 toolsView
Datadog
Securely connect your AI agents to Datadog through TrustGate: logs, traces, metrics, monitors, hosts, incidents and dashboards, scoped per agent and logged.
25 toolsView
Honeycomb
Securely connect your AI agents to Honeycomb through TrustGate: queries, traces, spans, service maps, Boards, Triggers, SLOs and Canvas investigations, scoped per agent and logged.
34 toolsView
Rootly
Securely connect your AI agents to Rootly through TrustGate: incidents, alerts, on-call schedules, escalation policies, workflows, services, retrospectives, playbooks and status pages, scoped per agent and logged.
261 toolsView
Connect incident.io MCP instantly
Pick the tools, point your agent at TrustGate, and incident.io MCP is live: scoped, inspected, logged.