Connect JumpCloud MCP to your AI agents, securely.
One secured endpoint for every JumpCloud call your AI agents make, scoped per user, inspected, and logged.Try JumpCloud MCP now
What your agents can ask once JumpCloud MCP is connected.
Select the tools your AI agents can call
117 tools from the JumpCloud MCP schema.
Showing 117 tools
What JumpCloud MCP exposes
JumpCloud MCP groups its 117 tools into 17 categories, each with a suggested starting policy.
All 117 tools as JSON, ready to paste.
| Category | Covers | Access | Suggested policy |
|---|---|---|---|
| Users | Listing and reading users, creating and deleting them, suspending and reactivating, unlocking, forcing a password reset, sending reset-password and activation emails, and resetting, adding or removing the MFA requirement on an account | Read / Write | Eleven of these thirteen change someone's ability to sign in. user_reset_mfa, user_add_mfa and user_remove_mfa_requirement touch the control every downstream system relies on, so gate them individually rather than as a group |
| Groups | Listing and reading user and device groups with their memberships, creating and deleting device groups, deleting user groups, and managing membership of both | Read / Write | Group membership is how access is actually granted in JumpCloud, so manage_user_group_membership is an entitlement change wearing an administrative name. Deleting a group removes whatever access it conferred |
| SaaS | Listing and reading SaaS applications, licences and accounts, creating, editing and deleting an application, submitting an application review, and deleting a SaaS account | Read / Write | saas_account_delete removes a person's account in a third-party system rather than in JumpCloud, so its effect lands outside the directory. The licence and account reads are a clear picture of what the organization pays for and who uses it |
| Devices | Listing and reading devices, updating a device, locking, restarting and shutting one down, erasing it, and binding or unbinding a user to a device | Read / Write | device_erase wipes a machine and nothing undoes it. Lock, restart and shutdown take a person off their computer immediately, and binding changes who can sign in to it |
| Commands | Listing and reading commands and their results, running a command, listing the devices and device groups a command targets, and managing those associations | Read / Write | command_run executes a JumpCloud Command on managed devices, which is arbitrary code execution across the fleet from one tool call. command_manage_associations changes which devices a command reaches, so it widens the blast radius before the run |
| Workflows | Listing and reading workflows and their runs, creating, updating, duplicating and deleting a workflow, and triggering a run | Read / Write | In public preview. A workflow is automation that keeps acting after the conversation ends, and workflow_trigger_run fires it immediately, so creating and triggering deserve separate approval |
| Applications | Listing and reading SSO applications, their associations and resources, the application catalog and import schedules | Read | Read-only. application_associations_list shows which users and groups reach which SSO applications, which is an access map of the organization and worth treating as internal |
| Patch Management | Patch coverage and summary figures, critical devices and their summary, the knowledge-base articles involved, and the device groups and devices in scope | Read | Entirely read-only, and one of the safest areas here. The output is a list of unpatched machines, which is a vulnerability inventory, so treat the result as sensitive even though the call is not |
| Admins & Provider Admins | Listing and reading administrators, updating one, resetting an admin's TOTP, reactivating an admin, and listing, inviting or removing provider admins at the MSP level | Read / Write | admin_reset_totp removes an administrator's second factor and provider_admin_invite adds somebody with reach across managed organizations. These are privilege changes and belong behind a named human approval every time |
| Identity Providers | Listing and reading identity providers, LDAP identity providers and the policies attached to them | Read | Read-only. The configuration returned describes how authentication is federated, which is useful context for an agent and useful reconnaissance for anyone else |
| Health Monitoring | Listing and reading health rules, their statistics, and the rule templates available | Read | Read-only, with no ability to change or silence a rule through this server, which removes the usual risk of an agent quietly weakening monitoring |
| Alerts | Listing alerts with their statistics, reading one, and listing its occurrences | Read | Read-only and a reasonable default allow. Alerts cannot be acknowledged or dismissed here, so the agent can read the security picture but not change it |
| Active Directory | Listing Active Directory instances and their translation rules, previewing how a rule would apply, and getting a recommendation for one | Read | Read-only, and the preview and recommendation tools are the right shape: they show the effect of a rule change without committing it |
| Assets | Listing and reading assets, updating one, and deleting one | Read / Write | asset_delete removes the record rather than the hardware, but an asset inventory with gaps is a compliance problem of its own |
| Access Requests & Policies | Listing and reading access requests, and listing and reading the policies applied across the organization | Read | Read-only. Access requests show what people have asked for and policies show what is enforced, so together they describe the gap between intent and configuration |
| Apple MDM | Listing Apple MDM configurations, the devices enrolled through Apple Business Manager, and the OS versions in use | Read | Read-only inventory of the Apple estate. Pair it with the patch tools for a version picture rather than using the device write tools to act on what it returns |
| Search & Insights | Executing a natural-language search across the organization through the search proxy, listing software applications, and retrieving Directory Insights events | Read | di_events_get reaches the audit log itself, including sign-ins and administrative actions, which is the organization's security record. search_api_execute proxies a free-form query, so log the query text and not just the tool name |
Connect JumpCloud MCP to your AI agent
Four steps, under ten minutes.
- 01
Sign in to NeuralTrust
Open the NeuralTrust platform, sign in and go to Getting started, then Connect your tools.
- 02
Choose your agent
When asked which agent you use, pick Claude Code, Codex, Cursor, Windsurf, Copilot or your own code.
- 03
Connect JumpCloud
Find JumpCloud in the tool list and connect it.
- 04
Connect your agent
Follow the steps on screen to add the config to your agent, then send the test prompt.
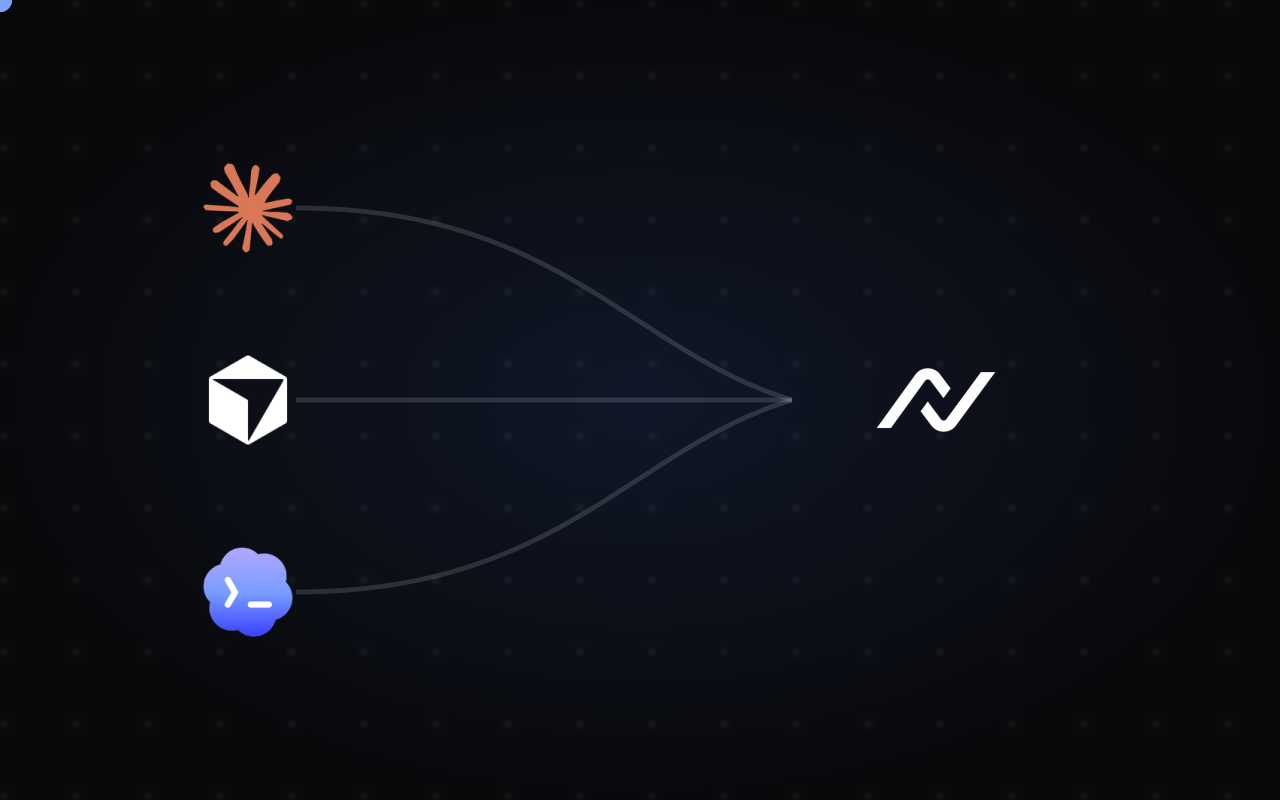
Permissions down to the single tool
You do not allow JumpCloud MCP or block it. You allow the exact tools each agent can call, one by one.
| JumpCloud MCP | 117 TOOLS AVAILABLE |
|---|---|
| Code review agent | 4 tools, read only |
| Issue triage bot | 9 tools |
| Platform team assistant | all 117 tools |
- Tool by toolConnecting the server is not the unit of access. Each tool is granted on its own.
- Default denyA tool you have not enabled is never exposed to the agent.
- Approval on writesTools that change or delete things can require a human to confirm.
Is JumpCloud MCP secure?
One endpoint instead of raw credentials. Every call is checked against policy and logged.
| AI agentsConnect through your MCP client configuration. | NeuralTrustApply controls based on your configuration. | JumpCloud MCP117 documented tools across US, EU and IN endpoints, with an organizationId parameter for MSP child orgs. Tools only, no resources or prompts, and streamable HTTP only; stdio is not supported. An admin must enable the server per organization, API keys mirror the admin's exact permissions, OAuth sessions are individually revocable with a configurable auto-revoke window, and MCP-originated requests appear in Directory Insights. |
|---|---|---|
| Coding assistants | Connection & credentialsper user | Users13 tools |
| Internal copilots | Tool access policiesdeny by default | Groups11 tools |
| Workflow automations | Request & response inspectioninline | SaaS11 tools |
| Compatible MCP clients | Activity monitoringalerts and logs | All other tools82 tools |
Use JumpCloud MCP with any AI agent framework
Setup guides for the tools your team already uses.
 Claude CodeAdd JumpCloud MCP to Claude Code from the terminal
 CursorUse JumpCloud MCP tools inside Cursor's agent
 CodexConnect JumpCloud MCP to the OpenAI Codex CLI
 WindsurfGive Windsurf's Cascade access to JumpCloud MCP
 Gemini CLICall JumpCloud MCP from Gemini CLI prompts
 Google AntigravityLet Antigravity agents work with JumpCloud MCP
 GitHub CopilotUse JumpCloud MCP in Copilot agent mode
 Claude EnterpriseRoll out JumpCloud MCP across your Claude workspace
 Microsoft Copilot StudioAdd JumpCloud MCP as a tool for Copilot Studio agents
 Open WebUIBring JumpCloud MCP tools into Open WebUI chats
 LangChainLoad JumpCloud MCP tools into LangChain agents
 HaystackPlug JumpCloud MCP into Haystack agent pipelines
 Strands AgentsGive Strands agents JumpCloud MCP tools
 Vercel AI SDKCall JumpCloud MCP from Vercel AI SDK apps
 n8nUse JumpCloud MCP in n8n AI agent workflows
Common questions about running JumpCloud MCP through TrustGate.
Other MCP servers
More servers from the catalog.
Vanta
Securely connect your AI agents to Vanta through TrustGate: compliance tests, controls, documents, frameworks, integrations, people, risks and vulnerabilities, scoped per agent and logged.
42 toolsView
Endor Labs
Securely connect your AI agents to Endor Labs through TrustGate: dependency vulnerability and risk checks, Endor's vulnerability database, platform findings, repo scans and AI diff review, scoped per agent and logged.
6 toolsView
Egnyte
Securely connect your AI agents to Egnyte through TrustGate: files and folders, full-text and advanced search, document AI and Agents, uploads, downloads, metadata, comments and share links, scoped per agent and logged.
28 toolsView
Stytch
Securely connect your AI agents to Stytch through TrustGate: projects, redirect URLs, public tokens and secrets, email templates, password policy and Consumer and B2B SDK configuration, scoped per agent and logged.
21 toolsView
Connect JumpCloud MCP instantly
Pick the tools, point your agent at TrustGate, and JumpCloud MCP is live: scoped, inspected, logged.