Last updated: November 18, 2026
What does AI governance require from enterprises in 2027? AI governance in 2027 means a live inventory of every AI system and agent, risk tiers that match the rules you face, and evidence that your controls ran in production. The calendar also moved: the EU pushed stand-alone high-risk obligations to December 2, 2027, so the real work is building proof before an auditor, customer or regulator asks for it.
TL;DR: Key Takeaways
- The EU's Digital Omnibus, Regulation (EU) 2026/1744, moves stand-alone high-risk AI obligations to December 2, 2027 (EU AI Act analysis).
- Gartner puts AI governance platform spending at $492 million in 2026 and above $1 billion by 2030 (Gartner).
- Gartner forecasts the market for securing AI at $4.8 billion in 2027 (Gartner).
- Stanford's AI Index 2026 counts a record 362 reported AI incidents in 2025 (Stanford HAI).
- Colorado replaced its AI Act with SB 26-189, a narrower law effective January 1, 2027 (Finnegan).
- Gartner predicts that by 2027, 40% of enterprises will demote or decommission autonomous AI agents after governance gaps surface in production (Gartner).
AI Governance in 2027 at a Glance
AI governance in 2027 rests on five requirements: a complete inventory, risk tiers, controls mapped to a framework, runtime evidence and named owners. Legal pressure is uneven, with EU dates delayed and US state rules in flux, yet customers and auditors already ask for proof. Waiting for a deadline only delays evidence you will need anyway.
This article covers what changed in 2026 and what to have in place for 2027. For definitions and framework basics, read our AI governance guide and the roundup of AI governance tools.
| Requirement | What it means in 2027 | Evidence a reviewer will ask for |
|---|---|---|
| Inventory | Every AI system, agent, MCP tool and employee-used app is known | A continuously updated register with an owner per entry |
| Risk tiers | Each system is classified against the rules and your own risk appetite | A documented tier, the reasoning and the controls it triggers |
| Framework mapping | Controls are mapped to ISO/IEC 42001, NIST AI RMF or both | A control matrix that links each control to a framework clause |
| Runtime evidence | Logs show what systems and agents actually did | Call logs, policy decisions, blocked actions and incident records |
| Ownership | Named people are accountable for each system and for the program | A RACI, committee minutes and sign-offs |
Source: Our analysis, based on Regulation (EU) 2026/1744, ISO/IEC 42001 and the NIST AI RMF.
How we researched
On November 18, 2026 we checked the EUR-Lex record of Regulation (EU) 2026/1744 and expert analysis of its dates, Gartner's 2026 releases and trade coverage of them, the Stanford HAI AI Index 2026, NIST's Cyber AI Profile page and law firm summaries of Colorado's statute. The operating model, levels and mappings are our analysis, not a legal opinion.
What Changed in 2026
Three shifts defined 2026. The EU agreed to delay its high-risk deadline, Colorado replaced its AI Act with a narrower statute, and analysts began sizing AI governance as its own spending category. Meanwhile incidents kept climbing, so the legal delays eased the pressure on dates but not on the need for evidence.
The EU delay: what moved and what did not
Regulation (EU) 2026/1744, the Digital Omnibus on AI, is dated July 8, 2026 and entered into force on July 27, 2026 (EUR-Lex). It amends the AI Act. According to EU AI Act analysis (2026), stand-alone high-risk systems, such as those used in hiring, credit or education, now face December 2, 2027 instead of August 2, 2026, and high-risk AI built into regulated products follows on August 2, 2028 (EU AI Act analysis).
The delay covers high-risk obligations and the national sandbox deadline. Transparency duties under Article 50 and the general-purpose AI rules kept their original dates, apart from a short grace period for marking generative content. It does not repeal the Act, and it does not change what customers ask in security reviews. Inventory and classification work carries over unchanged, so only the date for conformity evidence moved.
Spending and incidents moved the other way
According to Gartner (2026), global AI regulation is fueling a market for AI governance platforms that reaches $492 million in 2026 and passes $1 billion by 2030 (Gartner). Gartner separately forecasts the market for securing AI at $4.8 billion in 2027 (Gartner). The two figures measure different markets, so do not add them together. Gartner's survey of 360 organizations also found that those with AI governance platforms were 3.4 times more likely to achieve high governance effectiveness.
According to Stanford HAI (2026), reported AI incidents reached a record 362 in 2025 (Stanford HAI). Incident counts rise with adoption, but they show why boards ask for logs and owners rather than another policy PDF.
| 2026 development | What it changes for you | Source |
|---|---|---|
| Gartner sizes AI governance platforms at $492 million (2026) | Governance now has a budget line and a vendor category | Gartner |
| Digital Omnibus on AI becomes Regulation (EU) 2026/1744, in force July 27 | High-risk deadlines move, the rest of the Act stays | EUR-Lex |
| Gartner warns against uniform governance across AI agents (May 26) | Classify controls by agent autonomy instead of one rulebook | Gartner |
| Colorado replaces its AI Act with SB 26-189 | A narrower US state law, effective January 1, 2027 | Finnegan |
| Gartner forecasts securing AI at $4.8 billion for 2027 (August 26) | Security controls sit inside the governance budget | Gartner |
Source: EUR-Lex, Gartner and Finnegan (2026).
The 2027 Regulatory Calendar
Four sets of rules shape 2027 planning: the EU AI Act with its new dates, Colorado's replacement law, the voluntary ISO/IEC 42001 and NIST frameworks, and a growing set of other state rules. Only the first two carry legal deadlines you can name, while the frameworks give you the control vocabulary auditors and customers already use.
| Regime | Status in November 2026 | What to have ready in 2027 |
|---|---|---|
| EU AI Act, stand-alone high-risk systems | Applies from December 2, 2027 after Regulation (EU) 2026/1744 | Inventory, classification, risk management file, human oversight design and logging |
| EU AI Act, high-risk AI in regulated products | Applies from August 2, 2028 | A conformity plan agreed with the product manufacturer |
| Colorado SB 26-189 | Replaced the 2024 AI Act with a narrower law, effective January 1, 2027 | Notices before use and after adverse decisions, human review on request and three years of records |
| ISO/IEC 42001 | Voluntary, certifiable management system standard | Scope, policy, internal audit and Annex A control evidence |
| NIST AI RMF and Cyber AI Profile | Voluntary, with the Cyber AI Profile as an initial preliminary draft (NIST IR 8596) | Govern, Map, Measure and Manage mapping plus AI-specific cybersecurity controls |
Source: EUR-Lex, EU AI Act analysis, Finnegan and NIST (2026). Colorado details come from law firm summaries; confirm with counsel.
EU AI Act: build the file now, not in 2027
December 2, 2027 is closer than it looks for a regulated deployer. A risk management file, human oversight design, data governance records and automatic logging all depend on systems you must first find and classify. Our EU AI Act compliance guide covers the obligation by obligation view.
ISO/IEC 42001: the evidence backbone
ISO/IEC 42001 is a management system standard for AI, in the same family as ISO 27001. It is certifiable, which gives procurement teams a simple question to ask vendors. According to BCG (2026), it was among the first 100 organizations globally certified to the standard in January 2026 (BCG). Early certifications are still rare, so a scoped, honest implementation can set you apart.
Certification does not by itself prove compliance with a law. It proves that a management system exists, is audited and produces records, which is the part most governance programs lack.
NIST AI RMF and the Cyber AI Profile
The NIST AI Risk Management Framework organizes work into Govern, Map, Measure and Manage. NIST has also drafted a Cybersecurity Framework Profile for AI, published as NIST IR 8596 in an initial preliminary draft in December 2025 (NIST). Treat the profile as a preview of how US buyers may phrase AI security questions, and keep your control matrix flexible. Our NIST AI RMF implementation guide shows how to start.
US state laws: plan for a patchwork
Colorado's replacement law, signed on May 14, 2026, reaches developers and deployers of automated decision tools used in consequential decisions such as employment, housing and lending (Finnegan). It keeps notices, human review on request and records, but drops the 2024 act's impact assessments and risk management program. Texas, California and other states have their own rules with different scopes. A single inventory with a field for each system's jurisdictions and decision types lets you answer all of them without rebuilding the register each time.
From Policy Documents to Runtime Evidence
Auditors and customers now ask what your AI systems did, not what your policy says they should do. Runtime evidence means logs of model calls, tool calls, policy decisions and incidents, tied to an owner and a system record. A policy proves intent, while runtime evidence proves operation, and 2027 reviews will test the second.
The shift matters because AI systems change faster than annual reviews. A prompt edit, a new tool or a model upgrade can alter behavior in a day. Evidence therefore has to be collected where the traffic flows, not assembled from interviews before an audit.
| Question a reviewer asks | Policy-only answer | Evidence-based answer |
|---|---|---|
| Which AI systems are in use? | A list from a survey last year | A live inventory covering agents, MCP tools and employee-used apps |
| Who approved this agent and its tools? | An approval email | A registered owner, an approved tool list and permission scopes tied to identity |
| What data reached the model? | "Staff are told not to paste personal data" | Logged calls with data-loss rules applied and violations recorded |
| Was a risky action stopped? | "Guardrails exist" | Timestamped policy decisions in Monitor or Enforce mode |
| How do you know controls work? | An annual review | Scheduled red-team tests with retained results |
Source: Our analysis.
Five kinds of evidence cover most requests: inventory records, approval records, call and decision logs, test results and incident records. Collect each one automatically where you can. Manual evidence ages quickly and rarely survives a staff change.
Evidence needs its own governance. Call logs can contain personal or confidential data, so apply retention limits, access controls and redaction to the evidence store, and agree with legal and privacy teams what you keep and for how long.
Governing AI Agents and Employee AI Use
Agents change governance because they act, not just answer. According to Gartner (2026), one uniform rulebook for every AI agent can lead to enterprise failure, and 40% of enterprises will demote or decommission autonomous agents by 2027 (Gartner). Gartner recommends classifying agents by autonomy level and scope of access, with controls that grow at each level.
Classify agents by autonomy level
Levels turn an abstract policy into a decision a team can make in a meeting. Ask what the agent can read, what it can change and who is affected if it is wrong.
| Level | What the agent does | Minimum controls |
|---|---|---|
| 1: Observe | Reads data, with no ability to change anything | Scoped data access, authentication, logging and testing |
| 2: Advise | Recommends actions while a person carries them out | Level 1 controls plus accuracy and hallucination testing and training on how far to rely on it |
| 3: Act with approval | Acts only after explicit human approval of each action | Level 2 controls plus security testing, approval workflows with audit trails and incident response |
| 4: Act autonomously | Acts without a person in the loop | Level 3 controls plus continuous monitoring, enforced guardrails, rollback, circuit breakers and clear ownership |
Source: Gartner (2026), levels and baseline controls as reported in trade coverage of the release; wording is ours.
Employee AI use is part of the same register
Employees adopt AI tools faster than review cycles run, so the register must include apps no one formally approved. Discovery comes first, followed by a decision for each tool: approve, restrict or block. Publish the approved list where people work, and enforce it with controls rather than reminders. Our guide to shadow AI risks and prevention explains how discovery works in practice.
Training helps but does not replace enforcement. A short acceptable-use policy, an easy path to request a new tool and logging of sanctioned tools give the governance team data to refine the list each quarter.
An AI Governance Operating Model for 2027
A workable AI governance operating model has four moving parts: an accountable owner and a cross-functional committee, a living inventory, risk tiers that trigger controls, and an evidence store. Start with the smallest version of each, then deepen it where your risk tiers or regulators demand more.
Roles that make it work
Governance fails when everyone is responsible and nobody is accountable. Assign each role below a named person, even in a small company where one person holds several.
| Role | Owns | Typical home |
|---|---|---|
| Executive sponsor | Budget, risk appetite and escalations | CEO, COO or CRO |
| AI governance lead | Inventory, tiering process and committee | Risk, compliance or the CISO office |
| Security | Runtime controls, testing and incident response | CISO organization |
| Legal and privacy | Regulatory mapping, notices and contracts | General counsel, DPO |
| Business owner | The use case, its data and its outcomes | Product or business line |
| Internal audit | Independent checks on the program | Audit function |
Source: Our analysis.
Maturity levels and a readiness check
Use the levels below to place your program accurately. Moving up one level in the next two quarters is a realistic goal, and the evidence column shows what you can hand to a reviewer at each stage.
| Level | Inventory | Controls | Evidence |
|---|---|---|---|
| 1: Ad hoc | Spreadsheet from a survey | Policy PDF, no enforcement | Interviews and screenshots |
| 2: Documented | Owned register, updated quarterly | Tiers defined, mapped to a framework | Approval records and review minutes |
| 3: Enforced | Discovery keeps the register current | Policy applied at gateway and runtime | Automatic call logs and policy decisions |
| 4: Evidenced | Register linked to risk and jurisdictions | Controls tested on a schedule | Test results, incident records and audit-ready exports |
Source: Our analysis.
Cadence that keeps it alive
A governance program stays credible when it runs on a calendar. Hold a committee review monthly, re-tier systems when their tools, data or users change, and export an evidence pack each quarter so gaps surface before an audit does. Record every exception with an owner and an expiry date.
A quick readiness check: can you list every AI system and agent today, show who owns each one, and produce last month's blocked actions on request? Three yes answers put you at level 3 or above.
Security and Governance: Turning Policy into Enforced Controls
Governance fails when policy and enforcement live in different places. Prompt injection, sensitive data disclosure and agents misusing tools or permissions are behind most governance incidents. According to OWASP (2026), these map to LLM01 and LLM02 in the Top 10 for LLM Applications 2026 and to ASI01, ASI02 and ASI03 in the Top 10 for Agentic Applications (OWASP).
Prompt injection is LLM01, sensitive information disclosure is LLM02, and the agentic list covers Agent Goal Hijack as ASI01, Tool Misuse and Exploitation as ASI02 and Identity and Privilege Abuse as ASI03. Our OWASP Top 10 for LLM Applications 2026 article walks through the full list.
NeuralTrust, a Barcelona-based AI agent security company, delivers these controls on its Runtime Security Mesh. Each product answers one governance requirement from the table in this article.
| Governance requirement | OWASP reference | NeuralTrust control |
|---|---|---|
| Inventory and posture of agents, tools and permissions | ASI03 Identity and Privilege Abuse | Agent Posture Management (TrustLens) |
| Approved tools and policy at the point of use | ASI02 Tool Misuse and Exploitation | Agent Gateway (TrustGate), with 200+ pre-built MCP servers |
| Block unsafe content and actions at runtime | LLM01 Prompt Injection, LLM02 Sensitive Information Disclosure, ASI01 Agent Goal Hijack | Agent Runtime Security (TrustGuard) |
| Test controls before and after release | LLM01 Prompt Injection, ASI01 Agent Goal Hijack | AI Red Teaming (TrustTest) |
Source: OWASP LLM Top 10 2026 and Top 10 for Agentic Applications 2026. The mapping is our analysis.
TrustGate applies policy on LLM and MCP traffic, so the same layer that blocks a tool also records the call. TrustGuard applies runtime detectors in Monitor or Enforce mode, which produces the policy decisions reviewers ask for. No product makes an organization compliant on its own. These controls produce the evidence your governance program can present.
Which Starting Point Fits Your Organization?
Start where your largest gap or nearest deadline sits. Most enterprises begin with the inventory because every other control depends on it, then add tiers, framework mapping and runtime evidence in the order their regulators, customers and auditors demand. The table below matches common situations to a first move.
| Your situation | Start with |
|---|---|
| You have no reliable list of AI systems | Discovery, owners and a single register |
| You sell into the EU with hiring, credit or education use cases | Classification against high-risk categories and a risk file before December 2, 2027 |
| You make automated decisions about people in the US | Mapping decision tools against Colorado SB 26-189 and other state rules |
| Customers or auditors ask for certification | A scoped ISO/IEC 42001 management system |
| You run agents with tool access | Agent autonomy levels, then enforcement at the gateway and at runtime |
| Security wants proof that controls work | Runtime logging and scheduled red-team tests |
Conclusion
AI governance in 2027 depends on proof. The EU gave you until December 2, 2027 for stand-alone high-risk systems, but inventories, tiers, framework mappings and runtime evidence take time to build. Start with the inventory, tier your agents, align to ISO/IEC 42001 or the NIST AI RMF, and make enforcement produce the logs a reviewer will request. Teams that treat 2027 as a build year, not a deadline year, will answer those requests with exports instead of interviews.
Govern Enterprise AI in Production with NeuralTrust
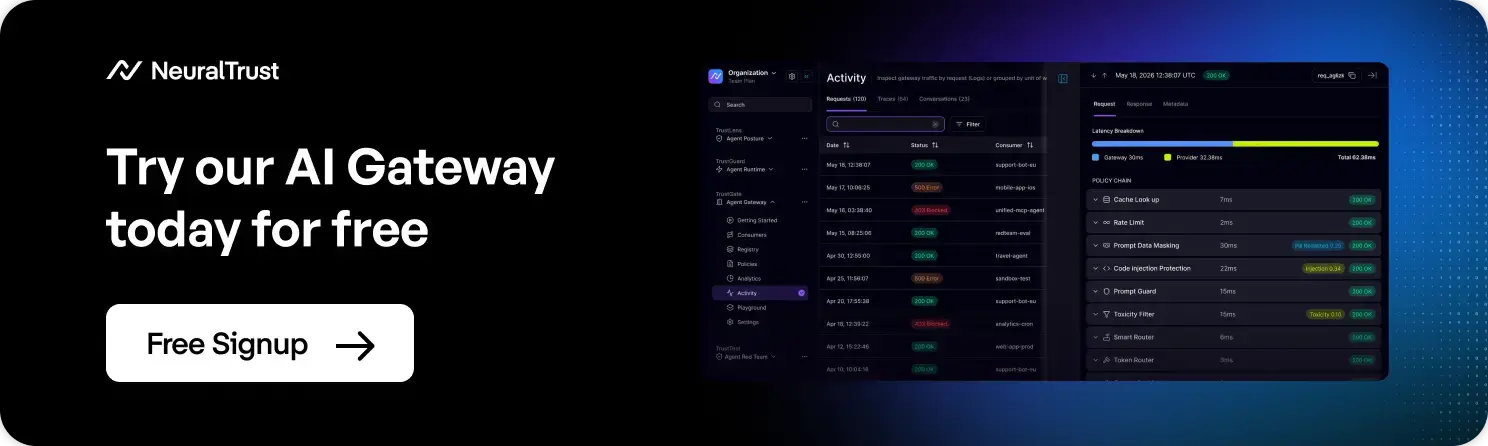
Apply approved tools and policies to LLM and MCP traffic with the Agent Gateway, and see how agent posture management keeps your inventory current.
Related Comparisons
- AI Governance 2026: Frameworks & Tools
- 10 Best AI Governance Tools in 2026
- EU AI Act Enterprise Compliance Guide
- NIST AI RMF Implementation Guide
FAQs about AI Governance
1. What does AI governance require in 2027?
A live inventory of AI systems and agents, risk tiers, controls mapped to a framework such as ISO/IEC 42001 or the NIST AI RMF, named owners and runtime evidence. Legal deadlines differ by region, but customers and auditors already ask for these five items in security and procurement reviews.
2. When do EU AI Act high-risk obligations apply now?
Under Regulation (EU) 2026/1744, stand-alone high-risk systems face December 2, 2027, and high-risk AI built into regulated products follows on August 2, 2028. The delay covers high-risk obligations only, so plan inventory and classification work as if the dates were fixed.
3. Is the EU delay a reason to pause AI governance work?
No. The delay moves a conformity date, not customer expectations. Inventory, classification, ownership and logging take months to build and serve every framework. Teams that pause now will face the same work later, with less time and more AI systems to find.
4. Does ISO/IEC 42001 make you compliant with the EU AI Act?
Not by itself. ISO/IEC 42001 certifies that you run an audited AI management system, which produces useful records. Legal compliance still depends on classifying your systems and meeting each applicable obligation, so use the standard as an evidence backbone, not as a legal shield.
5. Who should own AI governance?
Name an executive sponsor and an AI governance lead, then bring security, legal, privacy and business owners into a committee. The lead often sits in risk, compliance or the CISO office. What matters is a named person accountable for the inventory, tiers and evidence.
6. How is governing AI agents different from governing chatbots?
Agents act on systems, so their risk depends on permissions and tools, not just model answers. According to Gartner (2026), one uniform rulebook for all agents can lead to failure, so classify agents by autonomy level and scope of access and apply stricter controls at the higher levels.
7. How should enterprises handle shadow AI?
Discover which AI tools employees use, decide to approve, restrict or block each one, publish an approved list and enforce it with controls. Add logging for sanctioned tools so the list improves each quarter, and give people a fast way to request a new tool.
8. How big is the AI governance market?
According to Gartner (2026), spending on AI governance platforms reaches $492 million in 2026 and passes $1 billion by 2030. Gartner forecasts securing AI as a separate market at $4.8 billion in 2027, so treat the two figures as different budgets.
About the Author
Roger Howroyd is Head of Global SEO and AI at NeuralTrust, where he leads the company's search strategy across SEO, AEO, GEO, and LLM optimization. He specializes in AI-powered search, content strategy, and SEM. Connect on LinkedIn.
NeuralTrust is the leading platform for securing and scaling AI agents. Named a Pioneer in the Gartner Emerging Market Quadrant for AI Application Security 2026, recognized across six Gartner Hype Cycle reports in 2026, and featured in the Gartner Market Guide for Guardian Agents 2026, the Gartner Market Guide for AI Gateways 2025 and the KuppingerCole Leadership Compass for Generative AI Defense 2025. Headquartered in Barcelona with offices in London and New York. ISO 27001 certified.
Sources
Accessed on November 18, 2026.
- EUR-Lex, "Regulation (EU) 2026/1744 of the European Parliament and of the Council", 2026.
- EU AI Act analysis, "The Digital Omnibus on AI: What Regulation (EU) 2026/1744 Changed", August 4, 2026.
- Gartner, "Global AI Regulations Fuel Billion-Dollar Market for AI Governance Platforms", February 17, 2026.
- Gartner, "Gartner Says Applying Uniform Governance Across AI Agents Will Lead to Enterprise AI Agent Failure", May 26, 2026.
- Gartner, "Gartner Forecasts the Market for Securing AI Will Reach $4.8 Billion in 2027", August 26, 2026.
- Stanford HAI, "The 2026 AI Index Report: Responsible AI", 2026.
- Finnegan, "Colorado Replaces Landmark AI Act: An Overview of the New SB 26-189 Framework", 2026.
- NIST, "Cybersecurity Framework Profile for Artificial Intelligence (Cyber AI Profile), NIST IR 8596, initial preliminary draft", December 16, 2025.
- BCG, "BCG Among First 100 Organizations Globally Certified for ISO/IEC 42001", January 27, 2026.
- OWASP GenAI Security Project, "OWASP Top 10 for Agentic Applications for 2026", December 9, 2025.