What is the difference between on-premises, private cloud, and public cloud for sovereign AI?
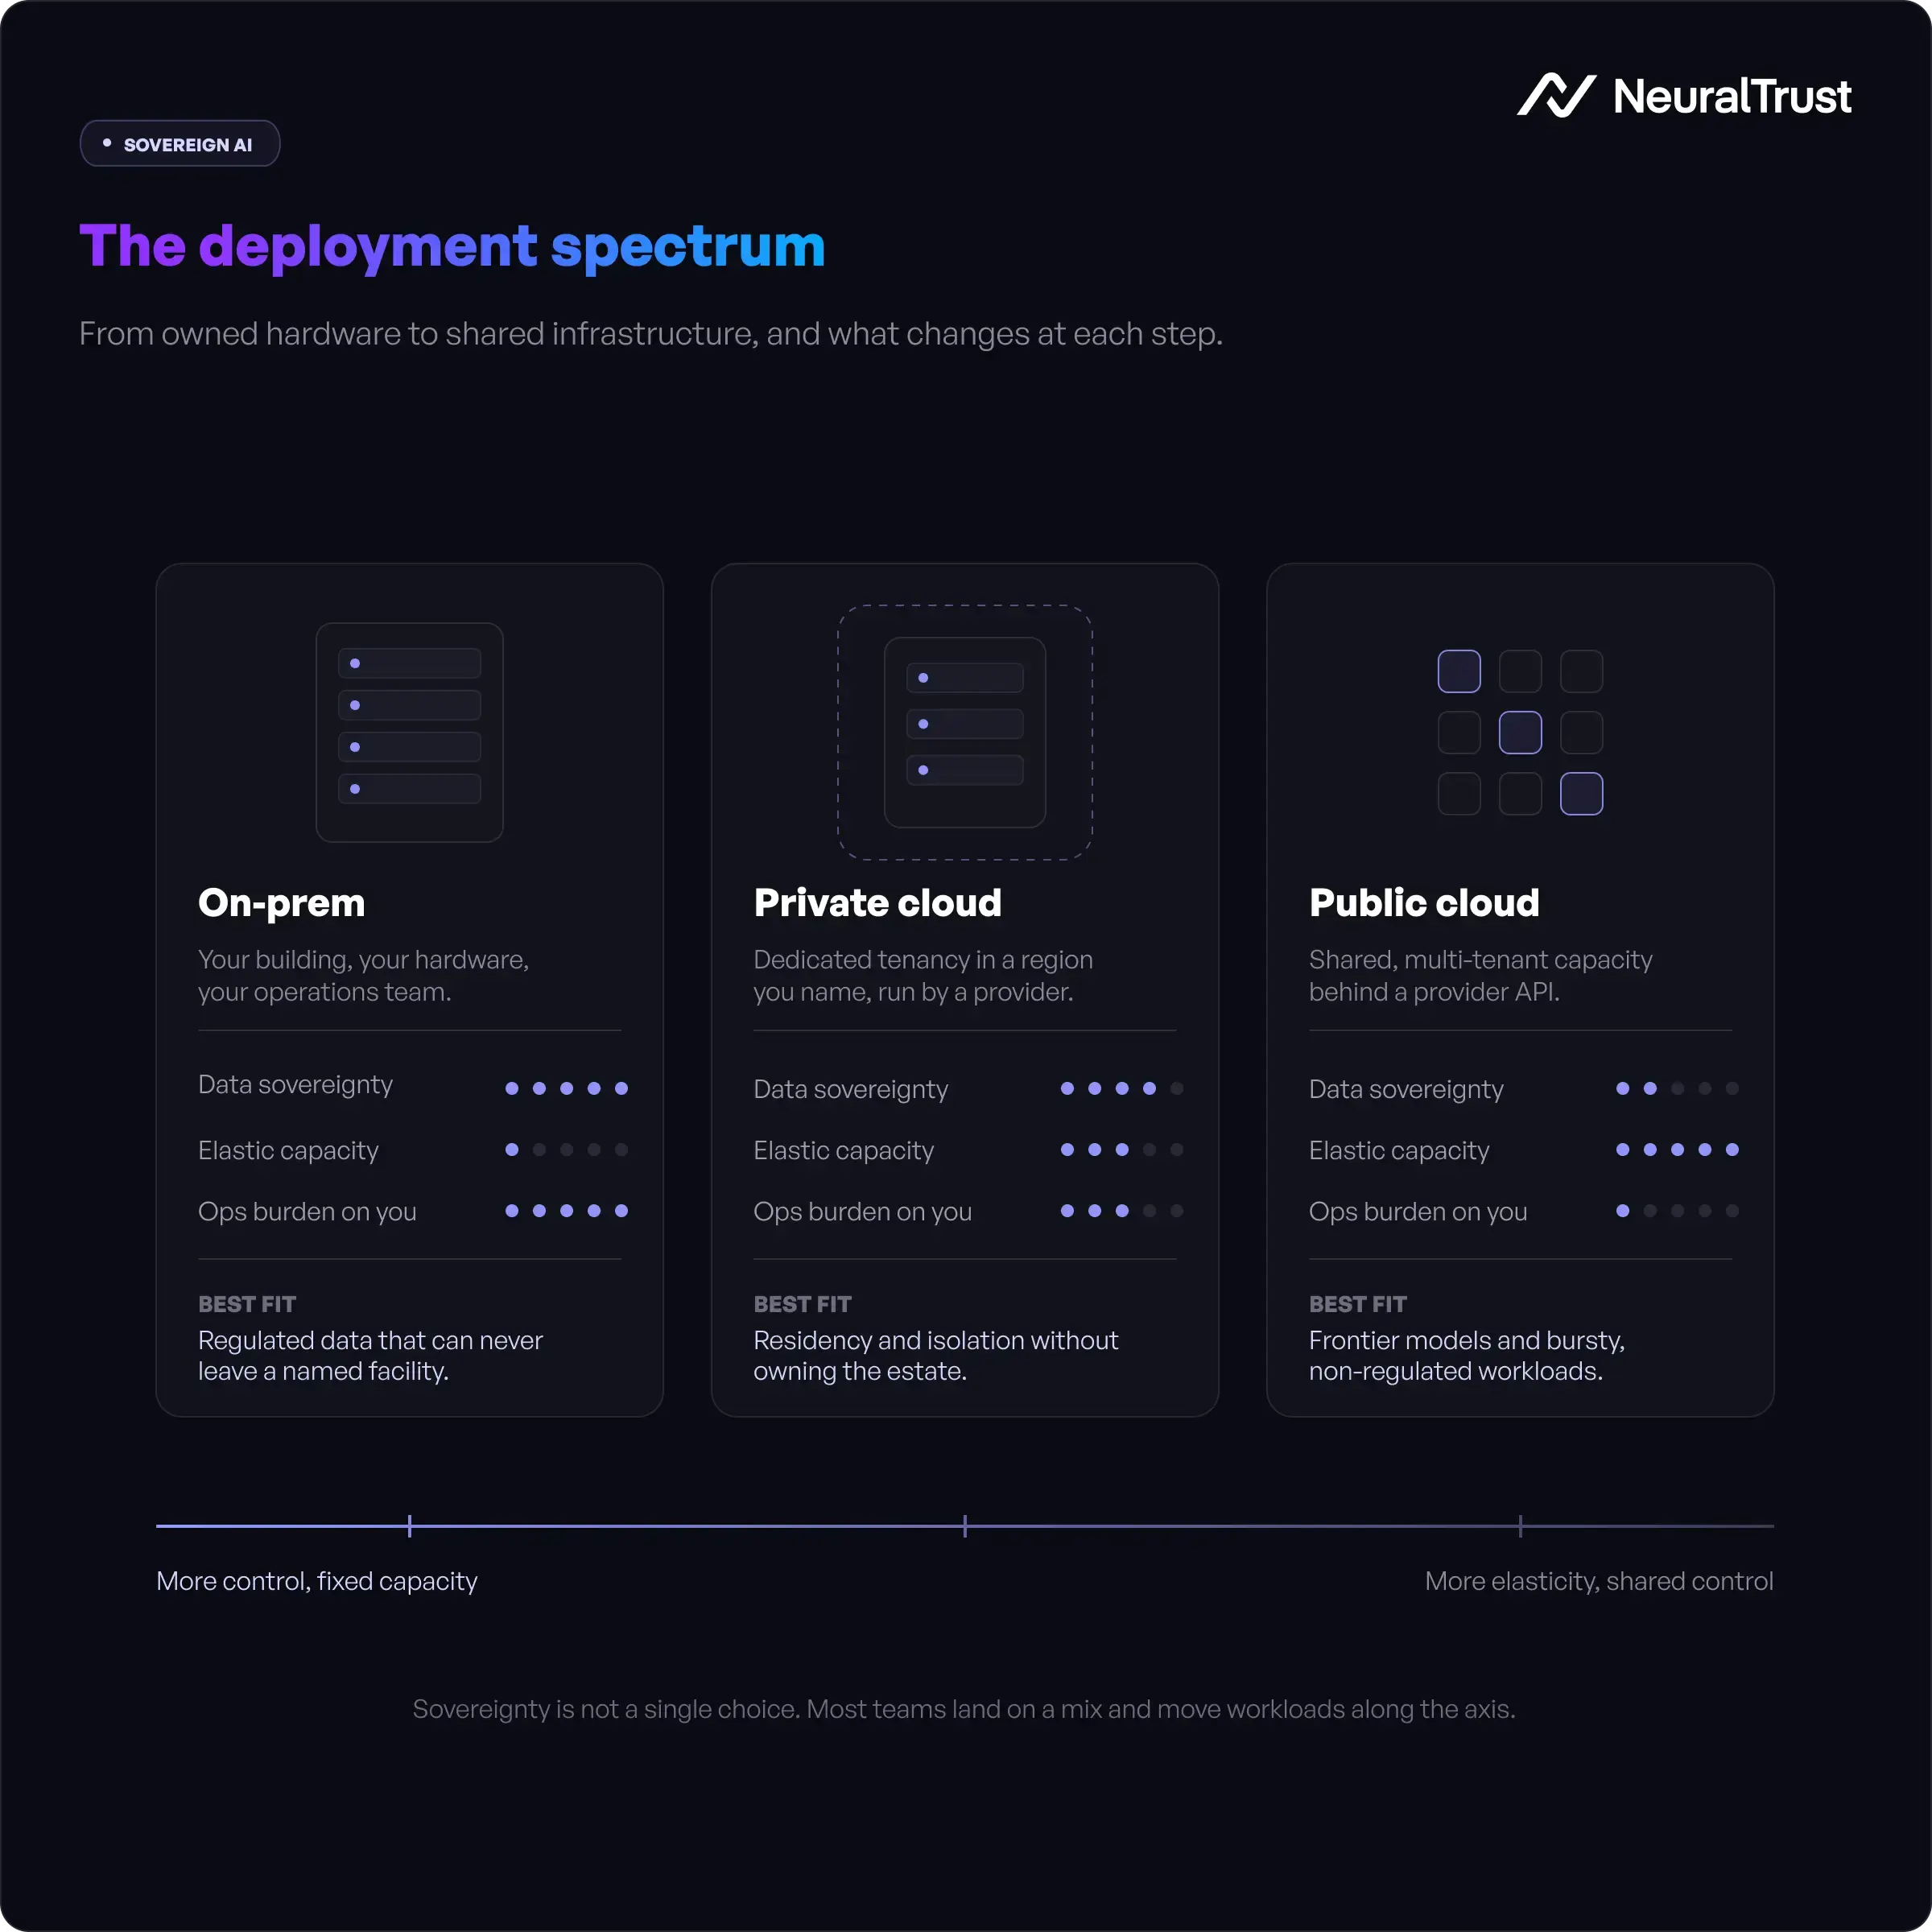
- On-premises AI means running models on hardware your organization owns and operates entirely within your own facilities, giving maximum data sovereignty but the highest operational burden and capital cost.
- Private cloud AI uses dedicated cloud infrastructure (either at a cloud provider like AWS GovCloud or Azure Sovereign Cloud, or in a colocation facility) where your data is isolated from other tenants.
- Public cloud AI uses shared multi-tenant infrastructure from providers like AWS, Azure, or Google Cloud, offering the lowest cost and most model choice but requiring additional controls (such as an AI gateway) to satisfy data sovereignty requirements.
TL;DR - Key Takeaways
- There is no single right answer: On-premises, private cloud, and public cloud each offer a different combination of data control, compliance confidence, operational overhead, performance, and cost. The right model depends on your risk tolerance, regulatory obligations, and AI workload mix.
- On-premises gives you the strongest sovereignty guarantee but the highest cost and operational burden. It is the right choice for defense, intelligence, and the most tightly regulated industries.
- Private cloud, including AWS GovCloud, Azure Sovereign Cloud, and Google Assured Workloads, provides dedicated tenancy and strong compliance controls without the full operational overhead of owning hardware.
- Public cloud can satisfy sovereign AI requirements when combined with an AI gateway that enforces PII masking, policy-based routing, and audit logging before data reaches external model endpoints.
- Most regulated enterprises end up with a hybrid model: on-premises or private cloud for sensitive workloads, public cloud with gateway controls for lower-sensitivity AI use cases.
You have three infrastructure choices for sovereign AI. On-premises is the most control, the most cost, and the most operational work. Private cloud is the middle path. Public cloud is the cheapest and most capable, but needs additional governance controls to be sovereign.
This article breaks down all three across the dimensions that actually matter for your decision.

Everybody Wants Sovereign AI. Not Everybody Wants to Buy a GPU Cluster.
I have heard the sovereign AI conversation play out the same way dozens of times.
A CISO walks in and says: "We need full data sovereignty. Nothing leaves our perimeter."
The infrastructure team comes back a week later: "That will be four million dollars in hardware, eighteen months to deploy, and a dedicated ML ops team."
Silence.
Then someone says: "Can we just use Azure?"
And that is where the real conversation starts. Because the honest answer is: yes, sometimes you can. And sometimes you cannot. And the difference between those two scenarios is exactly what this article is about.
Sovereign AI is not one architecture. It is a spectrum of choices, each with a different trade-off between control, cost, and operational complexity. Your job is to find where your risk tolerance and your regulatory obligations intersect on that spectrum.
The Three Models, Defined
Before comparing them, let me be precise about what each one means.
1. On-premises AI
On-premises AI means the models run on hardware your organization owns, in facilities your organization controls. The compute never leaves your building. No cloud provider, no shared infrastructure. You own the GPUs, you manage the software stack, you handle the security. Everything in your hands.
3. Private cloud AI
Private cloud AI is a dedicated cloud infrastructure that runs your workloads exclusively. No multi-tenancy. The infrastructure may be physically located at a hyperscaler's data center, but it is logically and contractually isolated from other customers. AWS GovCloud, Azure Sovereign Cloud, Azure Government, and Google Assured Workloads are all private cloud options with different sovereignty and compliance profiles.
4. Public cloud AI
Public cloud AI is shared infrastructure. You call an API, the request runs on shared GPU infrastructure alongside requests from other organizations, and the response comes back. The major LLM APIs, AWS Bedrock, Azure OpenAI, Google Vertex AI, and the direct APIs from model providers all fall into this category.
For the full architecture context around these three models, see How to Build a Sovereign AI Architecture.
Decision Matrix: Six Dimensions That Matter
| Dimension | On-Premises | Private Cloud | Public Cloud |
|---|---|---|---|
| Data sovereignty guarantee | Maximum: data never leaves your premises | Strong: dedicated tenancy, no shared infrastructure | Moderate: shared infrastructure, gateway controls required |
| GDPR / EU AI Act compliance | Easiest to prove: full physical control | Strong: contractual and technical controls | Requires additional controls such as AI gateway and SCC |
| Operational complexity | Highest: your team manages all hardware and ops | Moderate: provider manages infrastructure layer | Lowest: fully provider-managed |
| AI inference performance | High, but constrained by hardware budget | High: access to provider GPU infrastructure | Highest: access to latest GPU generations at scale |
| Total cost of ownership | Highest upfront CAPEX: servers, facilities, staff | Mid to high OPEX: premium over standard cloud pricing | Lowest: pay-per-use, no upfront hardware |
| Best-fit industries | Defense, intelligence, critical infrastructure, top-tier healthcare | Financial services, healthcare, government, EU enterprises | SaaS, startups, enterprises with AI gateway governance |
On-Premises: Maximum Control, Maximum Commitment
Nobody chooses on-premises because it is convenient. They choose it because their threat model leaves no other option.
If you are processing intelligence data, classified defense workloads, or the most sensitive patient health information under regulations that explicitly prohibit cloud processing, on-premises is not a preference. It is a requirement.
What you get: complete physical control. Every prompt, every model weight, every output stays within your facilities. There is no contractual question about whether your cloud provider can access your data, because there is no cloud provider. The answer is simply no.
What you give up: flexibility and speed. The GPU infrastructure required to run capable LLMs is expensive and power-intensive. NVIDIA H100 clusters, the standard for production LLM inference, carry six-figure price tags per unit. You also take on the full operational burden: hardware maintenance, model updates, infrastructure security, and ML ops staffing.
For most enterprises, pure on-premises AI is reserved for the most sensitive workloads. A closed-domain model that never touches external APIs. An air-gapped system for classified processing. Everything else goes elsewhere.
Private Cloud: The Middle Path
Private cloud gives you dedicated infrastructure without the full capital and operational commitment of owning hardware.
The three major sovereign cloud options each work somewhat differently.
AWS GovCloud is a US-only region designed for US federal agencies and contractors handling controlled unclassified information. It provides physical separation from standard AWS regions, US-only staff access, and compliance support for FedRAMP, ITAR, and other US regulatory frameworks. Non-US enterprises cannot use it.
Azure Sovereign Cloud and Azure Government provide dedicated infrastructure for government and regulated enterprises in various regions, with commitments around data residency, access controls, and sovereignty assurances. Microsoft has invested heavily in European sovereign cloud options specifically for EU enterprises with GDPR and EU AI Act compliance requirements.
Google Assured Workloads provides controls for data residency, staff access restrictions, and compliance support for enterprises with specific regulatory requirements. It does not provide full physical isolation but does provide strong logical controls.
What all three offer: dedicated tenancy (your workloads do not share physical compute with other customers), contractual data sovereignty commitments, and compliance documentation that supports your own audit processes.
What they still require: trusting the provider's contractual terms. You do not have physical control. A valid court order in the provider's jurisdiction could theoretically compel disclosure. For EU enterprises, this is the heart of the Schrems II problem: even contractually sovereign cloud infrastructure run by a US company may be subject to US surveillance laws.
Private cloud is the right answer for most regulated enterprises that need strong sovereignty guarantees without the capital and operational overhead of on-premises. Financial services, healthcare, and public sector organizations typically land here.
Public Cloud: Sovereign Enough, With the Right Controls
Here is the thing nobody says out loud: for most enterprise AI use cases, public cloud is sovereign enough.
Not for everything. Not without controls. But for the vast majority of internal productivity tools, customer-facing AI assistants, and analytical workloads that do not touch highly regulated personal data, the sovereignty question is answered by an AI gateway, not by your infrastructure choice.
The EU AI Act data governance obligations apply to high-risk AI systems. Most enterprise AI applications are not high-risk under Annex III. For those that are not, GDPR Standard Contractual Clauses (SCCs) plus technical controls at the gateway layer is a defensible compliance posture.
What an AI gateway does for public cloud sovereignty:
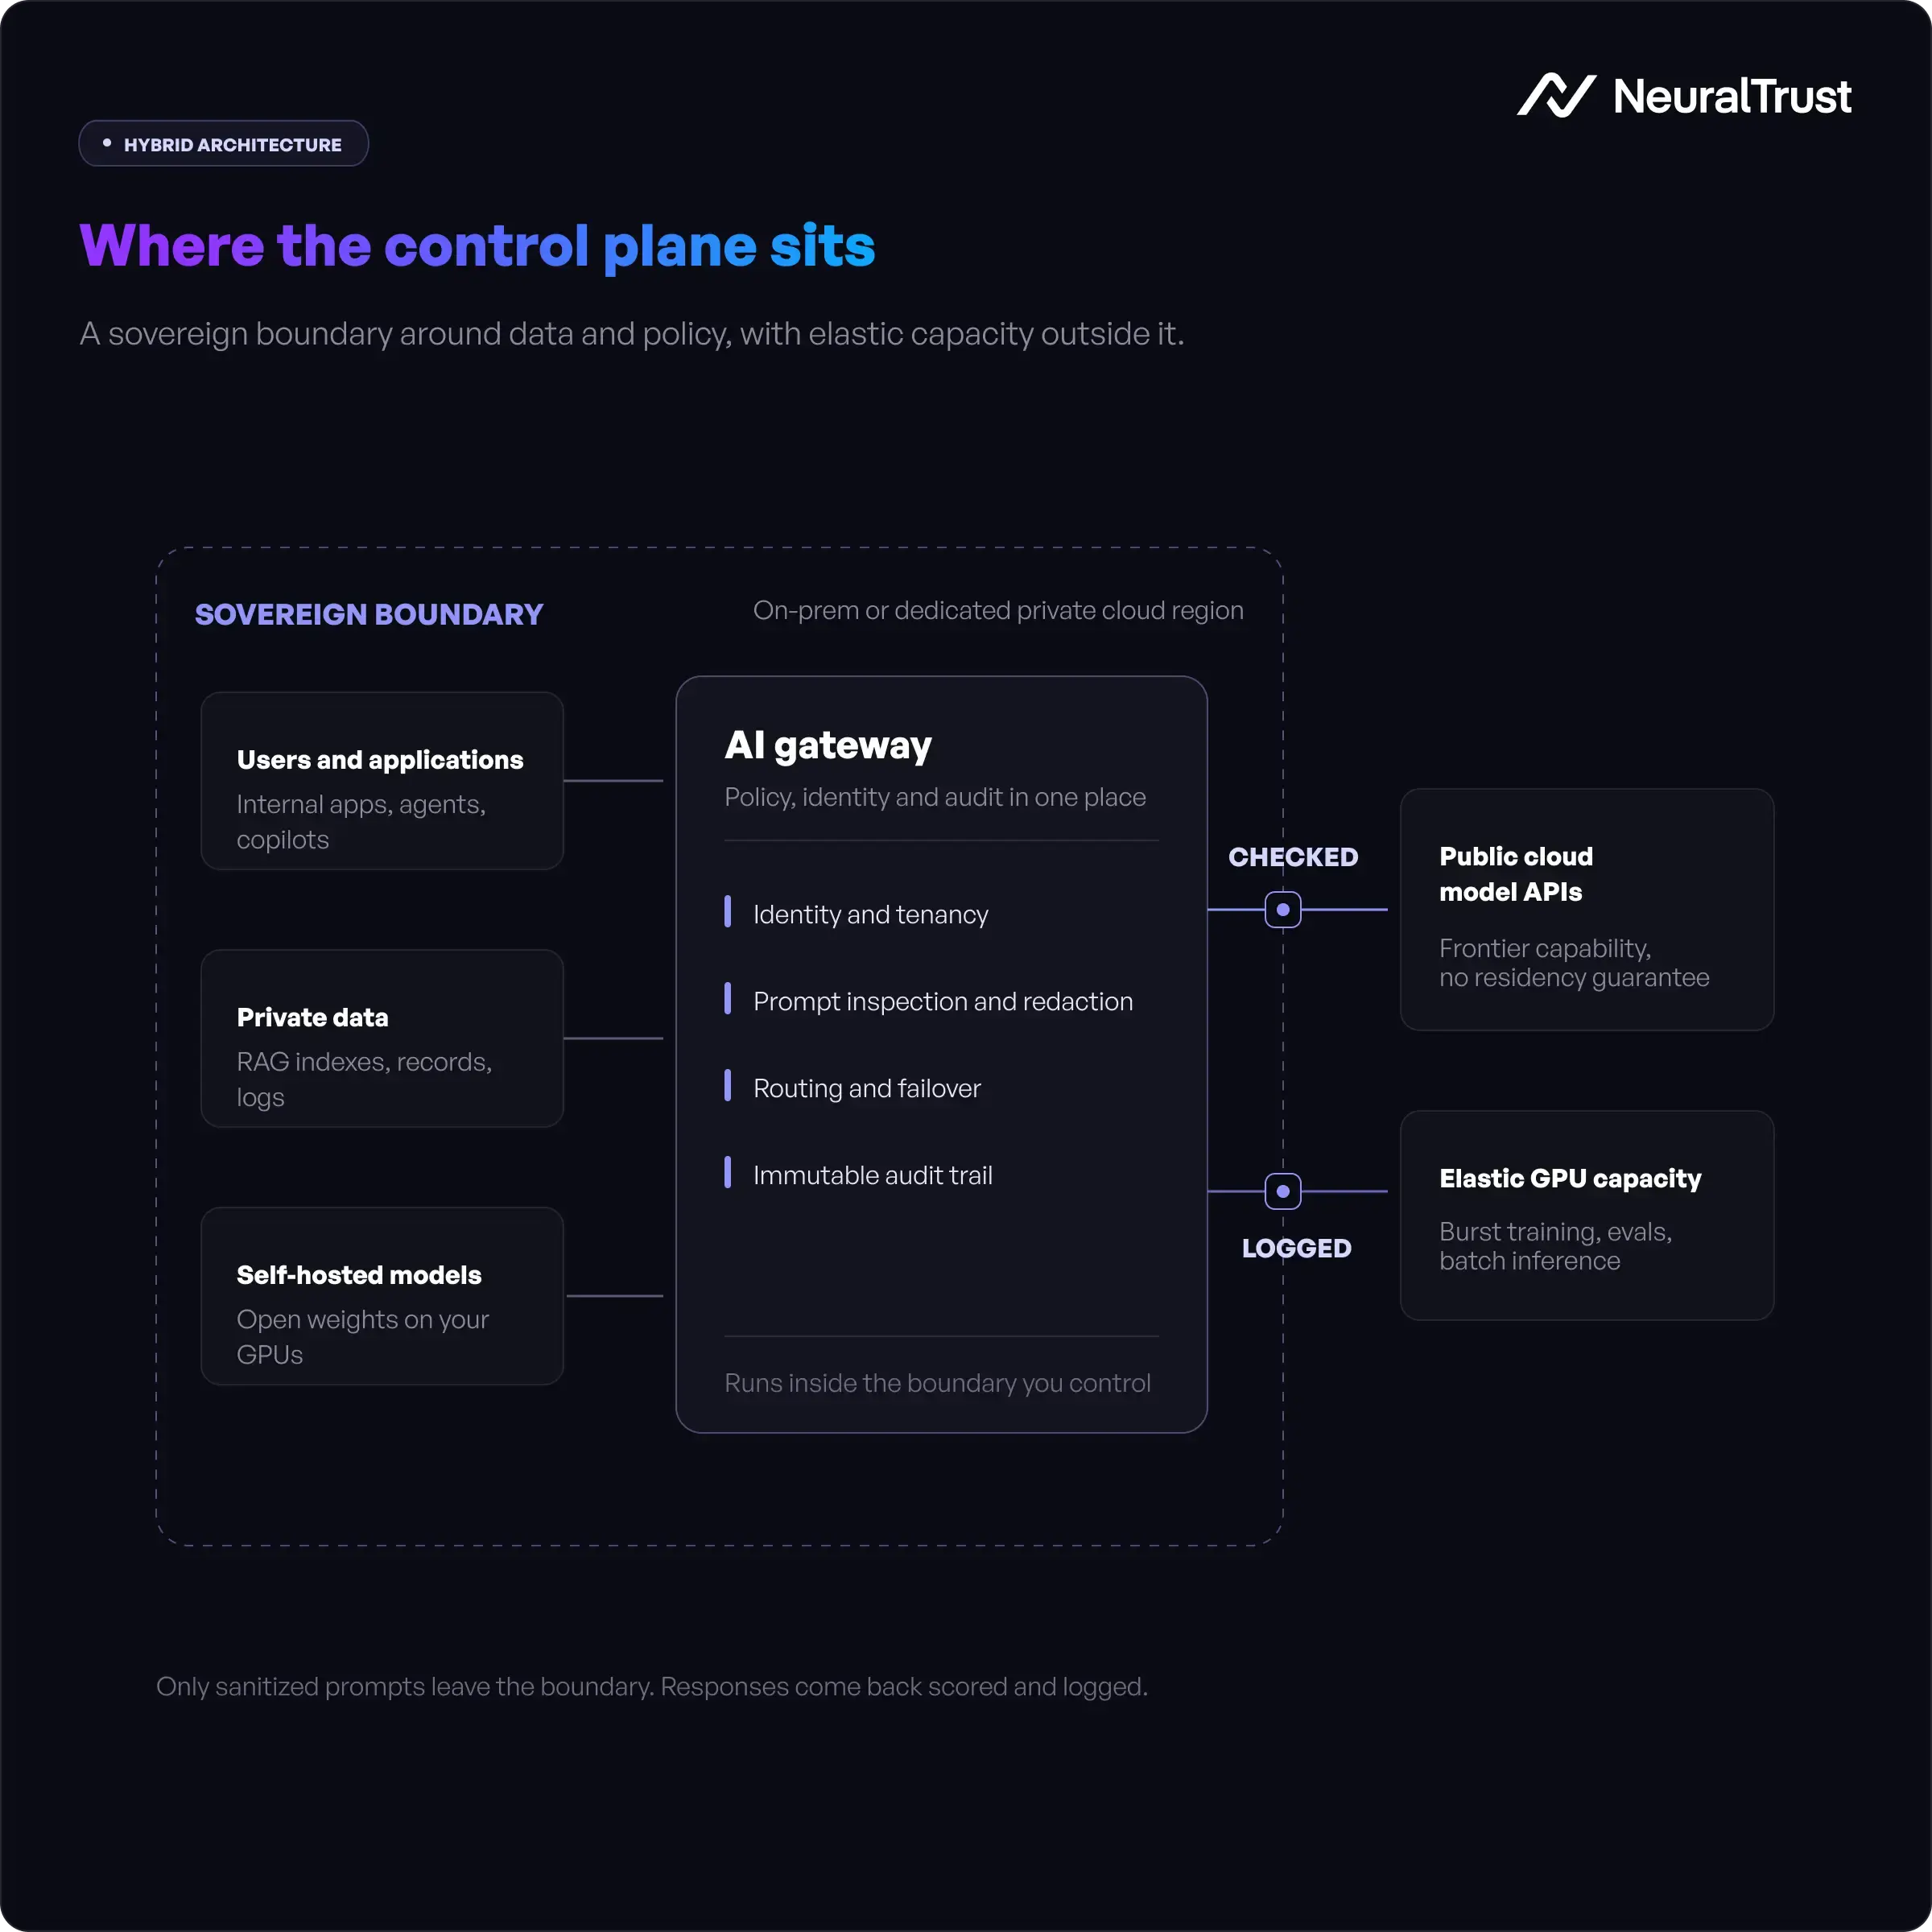
Intercepts every prompt before it reaches the external API and strips or masks any PII or sensitive data. Routes any prompt that exceeds your data classification threshold to a private cloud or on-premises endpoint instead. Logs every interaction with full attribution in a tamper-evident format. Inspects model responses for unauthorized data disclosure before returning them to the user.
Done right, this means your sensitive data never actually reaches the public cloud LLM. The gateway enforces your sovereignty policy at runtime. Public cloud becomes the compute layer; your gateway is the sovereignty layer.
For the technical detail on how this works, see How AI Gateways Help Maintain Data Sovereignty.
Hybrid Is the Real Answer
Almost no enterprise at scale lives entirely in one model.
The pattern I see most often: on-premises or private cloud for regulated, high-risk workloads; public cloud with AI gateway controls for the rest.
A hospital system might run clinical AI models on on-premises infrastructure in their EU data centers, while using a public cloud LLM for their internal HR assistant, with an AI gateway ensuring no patient data ever crosses over.
A financial services firm might use Azure Sovereign Cloud for customer-facing AI that touches transaction data, and a public cloud provider for back-office productivity tools, with the gateway acting as the policy enforcement layer across all of them.
This hybrid approach requires one thing above everything else: a governance layer that applies consistent sovereignty policies regardless of where the workload actually runs. That is the role NeuralTrust TrustGate plays: an infrastructure-agnostic control plane that enforces your data sovereignty policies whether the model lives on your premises, in a private cloud, or behind a public API.
For the complete multi-pillar architecture, see The Complete Guide to Data Sovereignty for Enterprise AI.
Industry Suitability Guide
| Industry | Recommended model | Reasoning |
|---|---|---|
| Defense and intelligence | On-premises | Classified data cannot be in any cloud environment |
| Critical infrastructure | On-premises or private cloud | OT/ICS data often restricted from cloud processing |
| Regulated healthcare (EU) | Private cloud or on-premises | EU AI Act high-risk + GDPR special category data |
| Financial services (EU) | Private cloud | DORA, GDPR, EU AI Act overlap on cloud outsourcing |
| Government (EU) | Private cloud (Azure Sovereign, Assured Workloads) | Data residency requirements + NIS2 compliance |
| SaaS and tech companies | Public cloud with AI gateway | Flexibility and cost efficiency with governance controls |
| Non-regulated enterprises | Public cloud with AI gateway | Lowest cost, most capable models |
Frequently Asked Questions
1. What is the difference between private cloud and sovereign cloud?
Private cloud refers to dedicated cloud infrastructure used exclusively by one organization, with no multi-tenancy. Sovereign cloud is a more specific term: it refers to cloud infrastructure with contractual and technical commitments around data residency, staff access restrictions, and jurisdictional controls designed to satisfy government or regulated industry sovereignty requirements. All sovereign clouds are private clouds, but not all private clouds have the specific sovereignty commitments (data residency, access controls, legal jurisdiction guarantees) that the term "sovereign cloud" implies.
2. Can public cloud be used for sovereign AI?
Yes, in many cases. For AI workloads that do not involve high-risk personal data or classified information, public cloud combined with an AI gateway that enforces PII masking, policy-based routing, and tamper-evident logging provides a defensible sovereignty posture. GDPR Standard Contractual Clauses cover the transfer mechanism, and the gateway layer ensures sensitive data never actually reaches the external model. For high-risk AI systems under EU AI Act Annex III, private cloud or on-premises is more appropriate.
3. What are the data sovereignty commitments of AWS GovCloud, Azure Sovereign Cloud, and Google Assured Workloads?
AWS GovCloud is a US-only region for US federal and defense workloads, with FedRAMP High authorization and ITAR controls. It is not available to non-US enterprises. Azure Sovereign Cloud and Azure Government provide dedicated infrastructure with data residency commitments, EU-staff-only access options for European sovereign cloud offerings, and contractual sovereignty guarantees. Google Assured Workloads provides data residency controls, access transparency, and compliance documentation but does not provide full physical isolation. Each provider publishes detailed sovereignty and compliance documentation for their respective offerings.
4. What is the total cost difference between on-premises and private cloud AI?
On-premises AI requires capital expenditure on GPU infrastructure: NVIDIA H100 or H200 clusters for production LLM inference, facility costs (power, cooling, physical security), and dedicated ML ops staffing. Private cloud shifts most of this to OPEX, typically at a premium over standard cloud pricing in exchange for dedicated infrastructure and sovereignty guarantees. Public cloud is the lowest cost option, with no upfront hardware and pay-per-use inference pricing. The right cost model depends on your workload volume: high, consistent inference volumes favor on-premises or private cloud; variable or lower-volume workloads favor public cloud.
5. How does the EU AI Act affect the choice between on-premises, private cloud, and public cloud?
The EU AI Act (Regulation (EU) 2024/1689) imposes data governance obligations under Article 10 on providers of high-risk AI systems. These obligations apply regardless of where the infrastructure runs: on-premises, private cloud, or public cloud. However, the compliance posture differs significantly by infrastructure model. On-premises and private cloud deployments where you control the data and the inference environment are much easier to document for a conformity assessment. Public cloud deployments require additional evidence of data governance controls (gateway logging, PII masking, routing policies) to satisfy Article 10 and Article 12 obligations. For a detailed breakdown, see Data Sovereignty Requirements under the EU AI Act.
Related Articles
- The Complete Guide to Data Sovereignty for Enterprise AI (2026)
- Data Sovereignty vs Data Residency vs Data Localization
- AI Data Sovereignty: Why Enterprises Need It Before Deploying LLMs
- How to Build a Sovereign AI Architecture
- Data Sovereignty Requirements under the EU AI Act
- How AI Gateways Help Maintain Data Sovereignty
- Data Sovereignty Best Practices for RAG Applications
- AI Data Privacy vs Data Sovereignty: Key Differences Explained
- Sovereign AI for Regulated Industries: Finance, Healthcare & Government
- Data Sovereignty Checklist for Enterprise CISOs (2026)
About the Author
Roger Howroyd is Head of Global SEO and AI at NeuralTrust, where he leads the company's search strategy across SEO, AEO, GEO, and LLM optimization. He specializes in AI-powered search, content strategy, backlink development, and SEM. Connect on LinkedIn.
NeuralTrust is an AI agent security platform, recognized in the Gartner Hype Cycle for Application Security 2026, the Gartner Hype Cycle for Infrastructure Security 2026, the Gartner 2025 Market Guide for AI Gateways and Guardian Agents, and the KuppingerCole 2025 Leadership Compass for Generative AI Defense. ISO 27001 certified. Headquartered in Barcelona.