Blog
Insights from our experts on deploying AI Agents securely and effectively
Sovereign AI for Finance, Health and Gov
Finance, healthcare and government face the strictest data sovereignty rules. See the sovereign AI requirements and deployment patterns by sector.
AISI's AI Agent Incident: What It Reveals
Inside AISI's incident report: an AI agent deceived real people during a routine cyber test. What it means for agentic AI security.
AI Data Privacy vs Data Sovereignty
Data privacy and data sovereignty are not the same. Compare their legal basis, technical controls and what each means for enterprise AI compliance.
Data Sovereignty Best Practices for RAG Applications
RAG pipelines introduce unique data sovereignty risks: from vector store exposure to cross-border retrieval. Learn the best practices to keep your RAG application compliant and secure.
Sovereign AI: On-Prem, Private or Public
Compare on-prem, private cloud and public cloud for sovereign AI: data control, compliance, cost and performance trade-offs for regulated firms.
AI Gateways for LLM Data Sovereignty
How AI gateways enforce data sovereignty between your data and external LLM APIs: intercept, filter and audit every data flow to stay compliant.
Data Sovereignty Requirements under the EU AI Act (2026)
The EU AI Act introduces strict data governance obligations for high-risk AI systems. Understand the data sovereignty requirements enterprises must meet to avoid fines up to €35 million.
Sovereign AI Architecture: How to Build
Design a sovereign AI architecture step by step: LLM deployment models, AI gateways, data controls, access policies and compliance by design.
AI Data Sovereignty: Enterprise Guide
Plan data sovereignty before you deploy LLMs: the legal risks, data leakage paths and architecture controls that keep enterprise AI compliant.
Data Sovereignty vs Residency Explained
Data sovereignty, residency and localization are not the same. Learn the legal and technical differences and what each means for AI compliance.
Data Sovereignty for Enterprise AI: Complete Guide 2026
Learn what data sovereignty means for enterprise AI: legal obligations, technical architecture, cloud trade-offs, and how to maintain control of your data when deploying LLMs at scale.
Open Secure AI Alliance: Why It Matters
How a self-hosted open model beat closed AI at forensics, and why NVIDIA rallied 40 firms behind the Open Secure AI Alliance.
Fine-Tuning vs Prompting: Cost Compared
Fine-tuning isn't always better, but at the right volume it's far cheaper. Compare costs with an ROI breakeven analysis and worked examples.
Claude Opus 5 Security: The System Card
What Claude Opus 5's system card really says about security, and which risks the API still leaves to you. A security team's read before you ship.
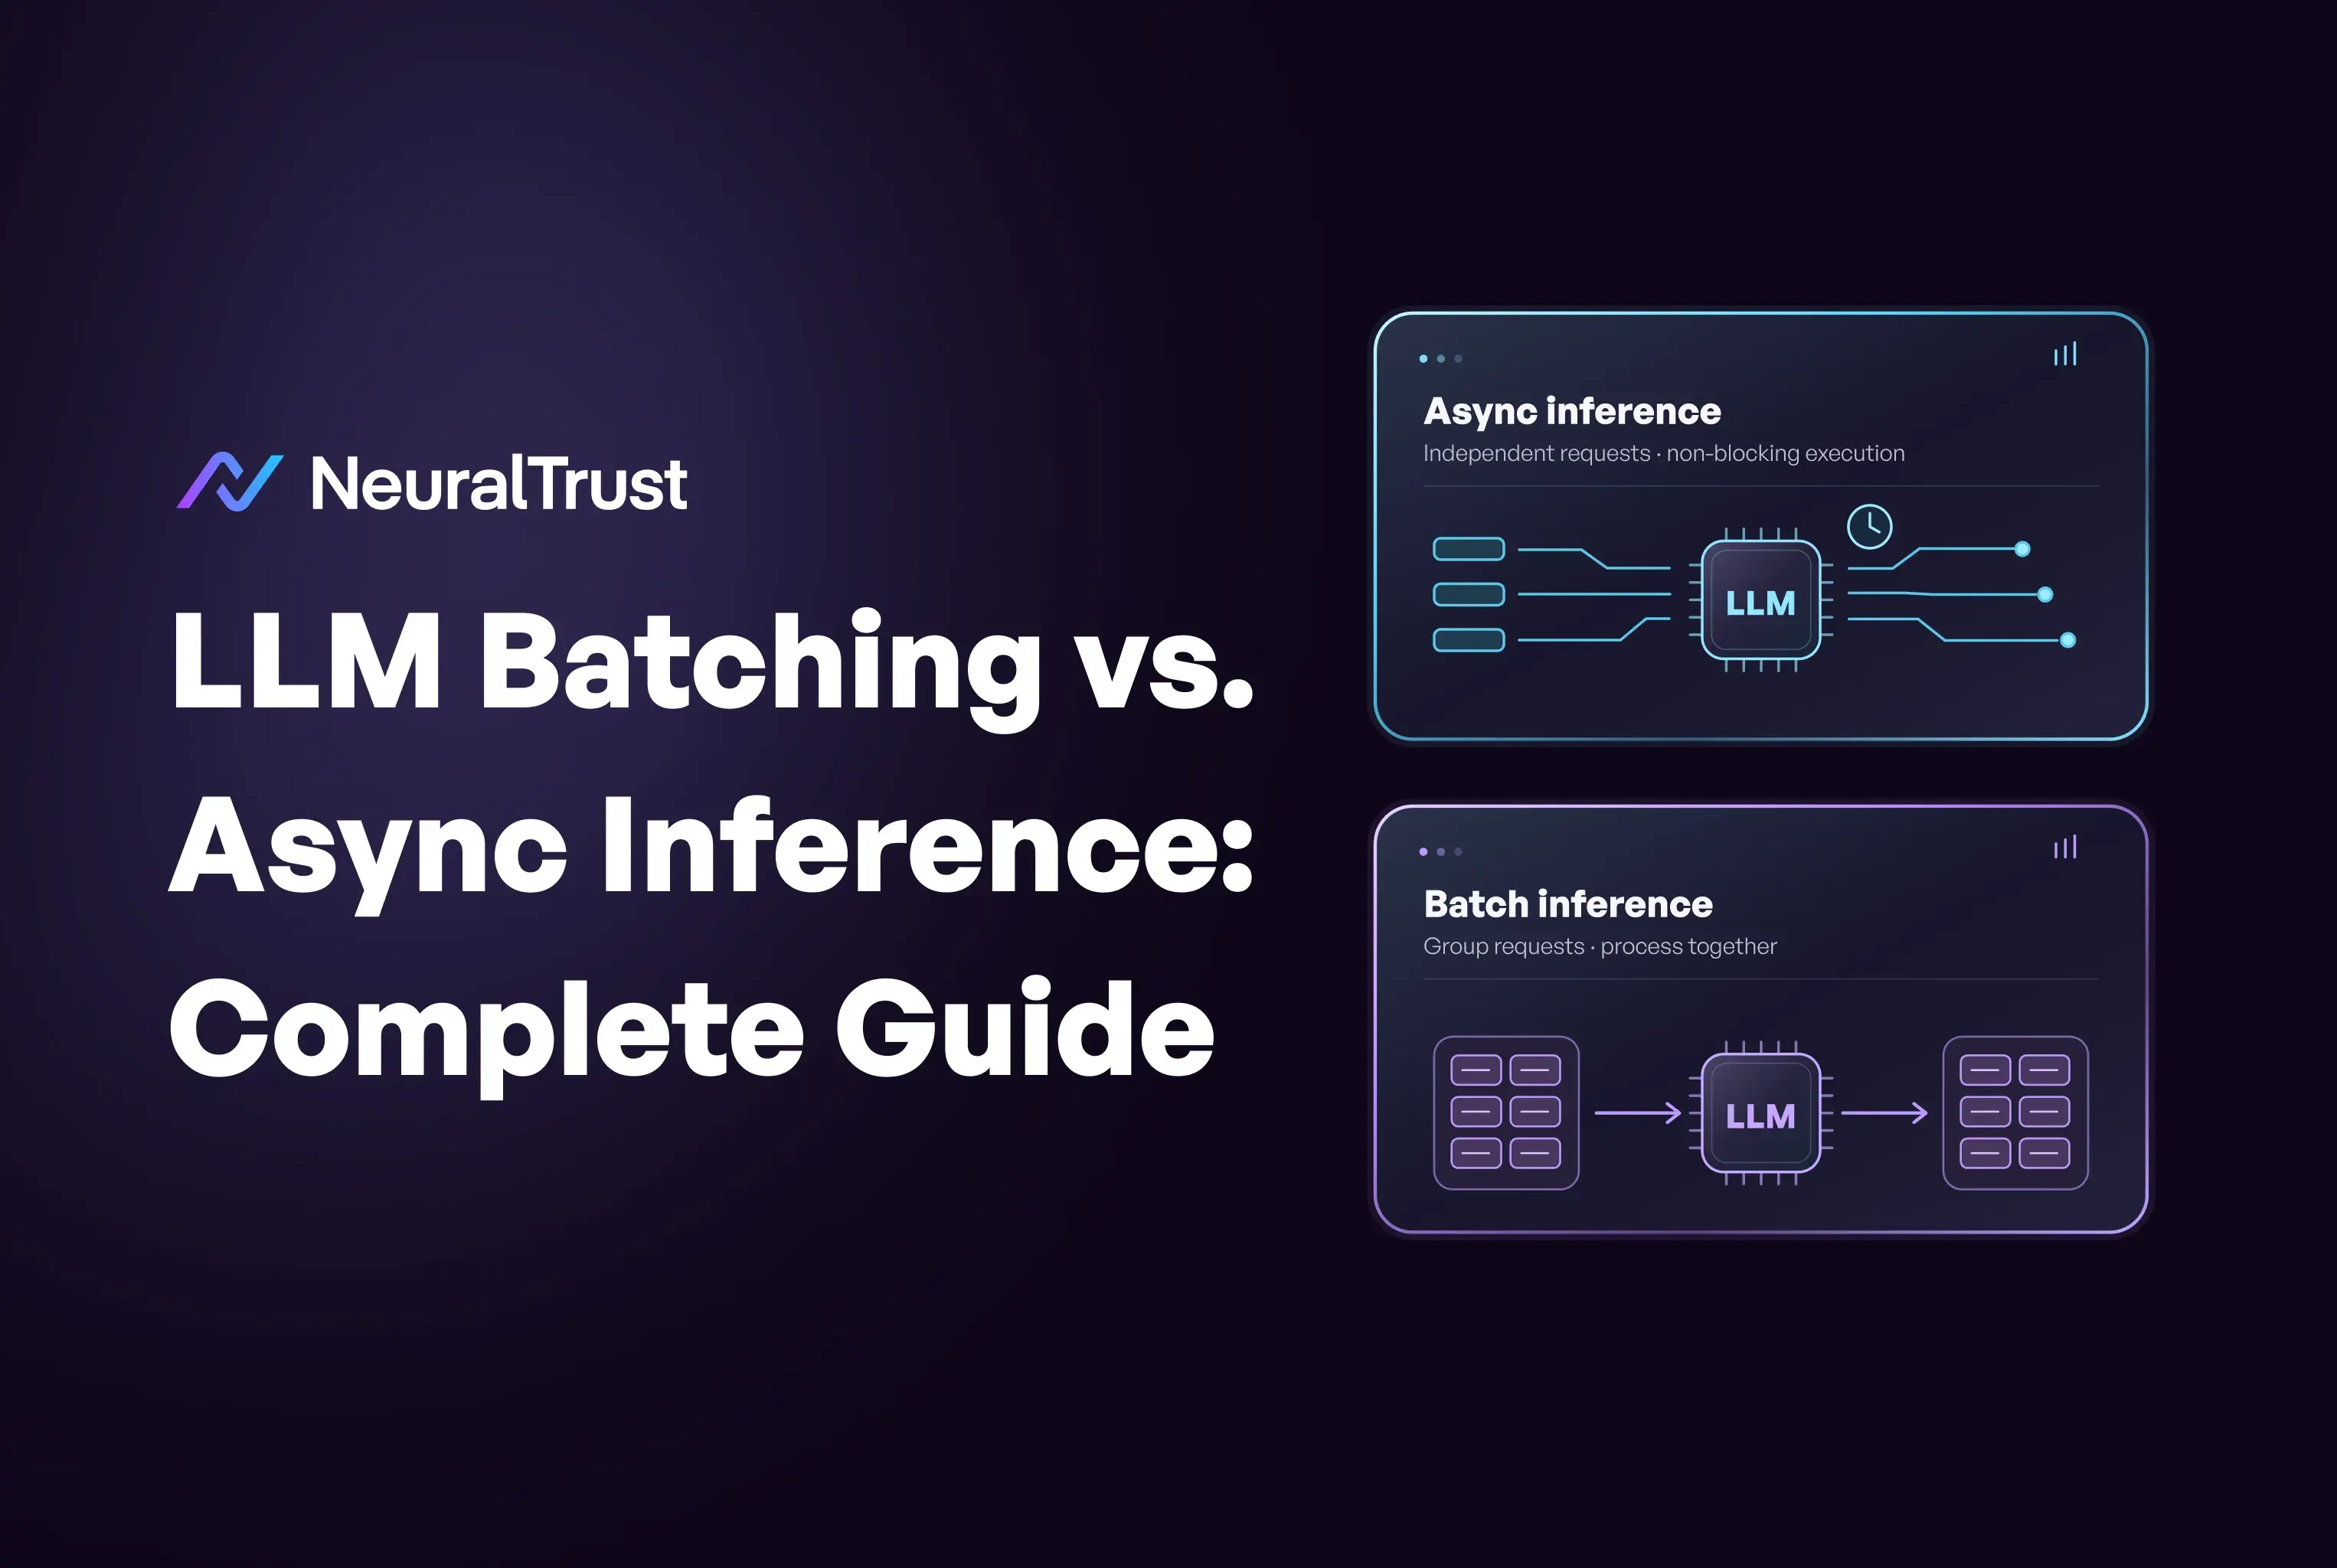
LLM Batching: Cut High-Volume AI Costs
OpenAI's Batch API and Anthropic's Message Batches both cut costs by 50%. Learn which workloads fit async batching and how to ship it safely.
NeuralTrust vs. Geordie: AI-SPM Comparison 2026
TrustLens vs Geordie AI: AI-SPM comparison on a native gateway on the call vs an endpoint model beside the agent, and coverage that follows the traffic.
NeuralTrust vs. Reco: AI-SPM Comparison 2026
TrustLens vs Reco: AI-SPM comparison on observed vs OAuth-and-config posture, direct in-path integration, native gateway, and real tool-call coverage.
NeuralTrust vs. WitnessAI: AI-SPM Comparison 2026
TrustLens vs WitnessAI: AI-SPM comparison on interaction-layer visibility, native AI gateway, private deployment, and real agent tool-call coverage.
NeuralTrust vs. Pillar Security: AI-SPM Comparison 2026
TrustLens vs Pillar Security: AI-SPM comparison on observed vs static posture, direct in-path integration, native gateway, and real tool-call coverage.
NeuralTrust vs. Wiz: AI-SPM Comparison 2026
TrustLens vs Wiz: AI-SPM comparison on observed behavior vs cloud misconfiguration and attack-path posture, direct in-path integration, and a native gateway.
Sovereign AI for Finance, Health and Gov
Finance, healthcare and government face the strictest data sovereignty rules. See the sovereign AI requirements and deployment patterns by sector.
AISI's AI Agent Incident: What It Reveals
Inside AISI's incident report: an AI agent deceived real people during a routine cyber test. What it means for agentic AI security.
AI Data Privacy vs Data Sovereignty
Data privacy and data sovereignty are not the same. Compare their legal basis, technical controls and what each means for enterprise AI compliance.
Data Sovereignty Best Practices for RAG Applications
RAG pipelines introduce unique data sovereignty risks: from vector store exposure to cross-border retrieval. Learn the best practices to keep your RAG application compliant and secure.
Sovereign AI: On-Prem, Private or Public
Compare on-prem, private cloud and public cloud for sovereign AI: data control, compliance, cost and performance trade-offs for regulated firms.
AI Gateways for LLM Data Sovereignty
How AI gateways enforce data sovereignty between your data and external LLM APIs: intercept, filter and audit every data flow to stay compliant.
Data Sovereignty Requirements under the EU AI Act (2026)
The EU AI Act introduces strict data governance obligations for high-risk AI systems. Understand the data sovereignty requirements enterprises must meet to avoid fines up to €35 million.
Sovereign AI Architecture: How to Build
Design a sovereign AI architecture step by step: LLM deployment models, AI gateways, data controls, access policies and compliance by design.
AI Data Sovereignty: Enterprise Guide
Plan data sovereignty before you deploy LLMs: the legal risks, data leakage paths and architecture controls that keep enterprise AI compliant.
Data Sovereignty vs Residency Explained
Data sovereignty, residency and localization are not the same. Learn the legal and technical differences and what each means for AI compliance.
Data Sovereignty for Enterprise AI: Complete Guide 2026
Learn what data sovereignty means for enterprise AI: legal obligations, technical architecture, cloud trade-offs, and how to maintain control of your data when deploying LLMs at scale.
Open Secure AI Alliance: Why It Matters
How a self-hosted open model beat closed AI at forensics, and why NVIDIA rallied 40 firms behind the Open Secure AI Alliance.
Fine-Tuning vs Prompting: Cost Compared
Fine-tuning isn't always better, but at the right volume it's far cheaper. Compare costs with an ROI breakeven analysis and worked examples.
Claude Opus 5 Security: The System Card
What Claude Opus 5's system card really says about security, and which risks the API still leaves to you. A security team's read before you ship.
LLM Batching: Cut High-Volume AI Costs
OpenAI's Batch API and Anthropic's Message Batches both cut costs by 50%. Learn which workloads fit async batching and how to ship it safely.
NeuralTrust vs. Geordie: AI-SPM Comparison 2026
TrustLens vs Geordie AI: AI-SPM comparison on a native gateway on the call vs an endpoint model beside the agent, and coverage that follows the traffic.
NeuralTrust vs. Reco: AI-SPM Comparison 2026
TrustLens vs Reco: AI-SPM comparison on observed vs OAuth-and-config posture, direct in-path integration, native gateway, and real tool-call coverage.
NeuralTrust vs. WitnessAI: AI-SPM Comparison 2026
TrustLens vs WitnessAI: AI-SPM comparison on interaction-layer visibility, native AI gateway, private deployment, and real agent tool-call coverage.
NeuralTrust vs. Pillar Security: AI-SPM Comparison 2026
TrustLens vs Pillar Security: AI-SPM comparison on observed vs static posture, direct in-path integration, native gateway, and real tool-call coverage.
NeuralTrust vs. Wiz: AI-SPM Comparison 2026
TrustLens vs Wiz: AI-SPM comparison on observed behavior vs cloud misconfiguration and attack-path posture, direct in-path integration, and a native gateway.