Last updated: September 2026
What does enterprise AI governance actually require in a production deployment?
An AI gateway is the control layer that makes enterprise AI governance operational. It enforces policy on every model interaction, generates the audit trails regulators ask for, applies identity-aware access controls that existing Identity and Access Management (IAM) tools cannot reach, and feeds LLM observability data into the compliance reporting stack. Without a gateway, enterprise AI governance is just a policy document.
TL;DR - Key Takeaways
- AI governance without enforcement is just documentation: Policies, frameworks, and risk assessments only translate into protection when a technical control layer sits between your applications and your models.
- An AI gateway is that control layer: It intercepts every prompt and completion, applies policy in real time, and generates the structured audit data governance and compliance teams need.
- LLM observability is the foundation of AI governance: You cannot govern what you cannot see: an AI gateway surfaces token usage, model routing decisions, content policy violations, and anomalous behaviour across every AI application in the stack.
- Enterprise AI gateway deployments map directly to regulatory requirements: The EU AI Act, GDPR, and NCSC AI guidelines each impose obligations that a properly configured AI gateway can address at the infrastructure layer.
- According to Gartner, by 2028, loss of control over AI agents will be the top concern for 40% of Fortune 1000 organisations. The window for establishing governance controls is now, before AI deployments scale beyond manual oversight.
- TrustGate, NeuralTrust's AI gateway, implements policy enforcement, LLM observability, access control, and compliance logging from a single infrastructure deployment with no application-level changes required.
The AI Governance Gap Every Enterprise Needs to Close
Most enterprises now have an AI policy. Very few have AI governance that actually works in production.
The gap between the two is structural. An AI policy is a document that defines acceptable use, sets risk appetite, and lists the conditions under which AI can be deployed. AI governance is the set of controls that enforces that policy on every model call, every agent action, and every piece of output that flows through your AI infrastructure. The first is produced by a committee. The second requires an AI gateway.
Enterprise AI deployments are scaling faster than governance infrastructure. Teams ship features powered by large language models, deploy AI agents into customer-facing workflows, and connect internal tools to model providers using API keys that exist outside the visibility of any central security or compliance function.
The result is a fragmented landscape: dozens of AI applications generating millions of model interactions with no consistent policy layer, no unified audit trail, and no way to demonstrate to a regulator, board, or CISO that controls are in place.
This is the governance gap, and the reason it exists is that the tools available until recently were not designed to govern AI traffic at the infrastructure layer.
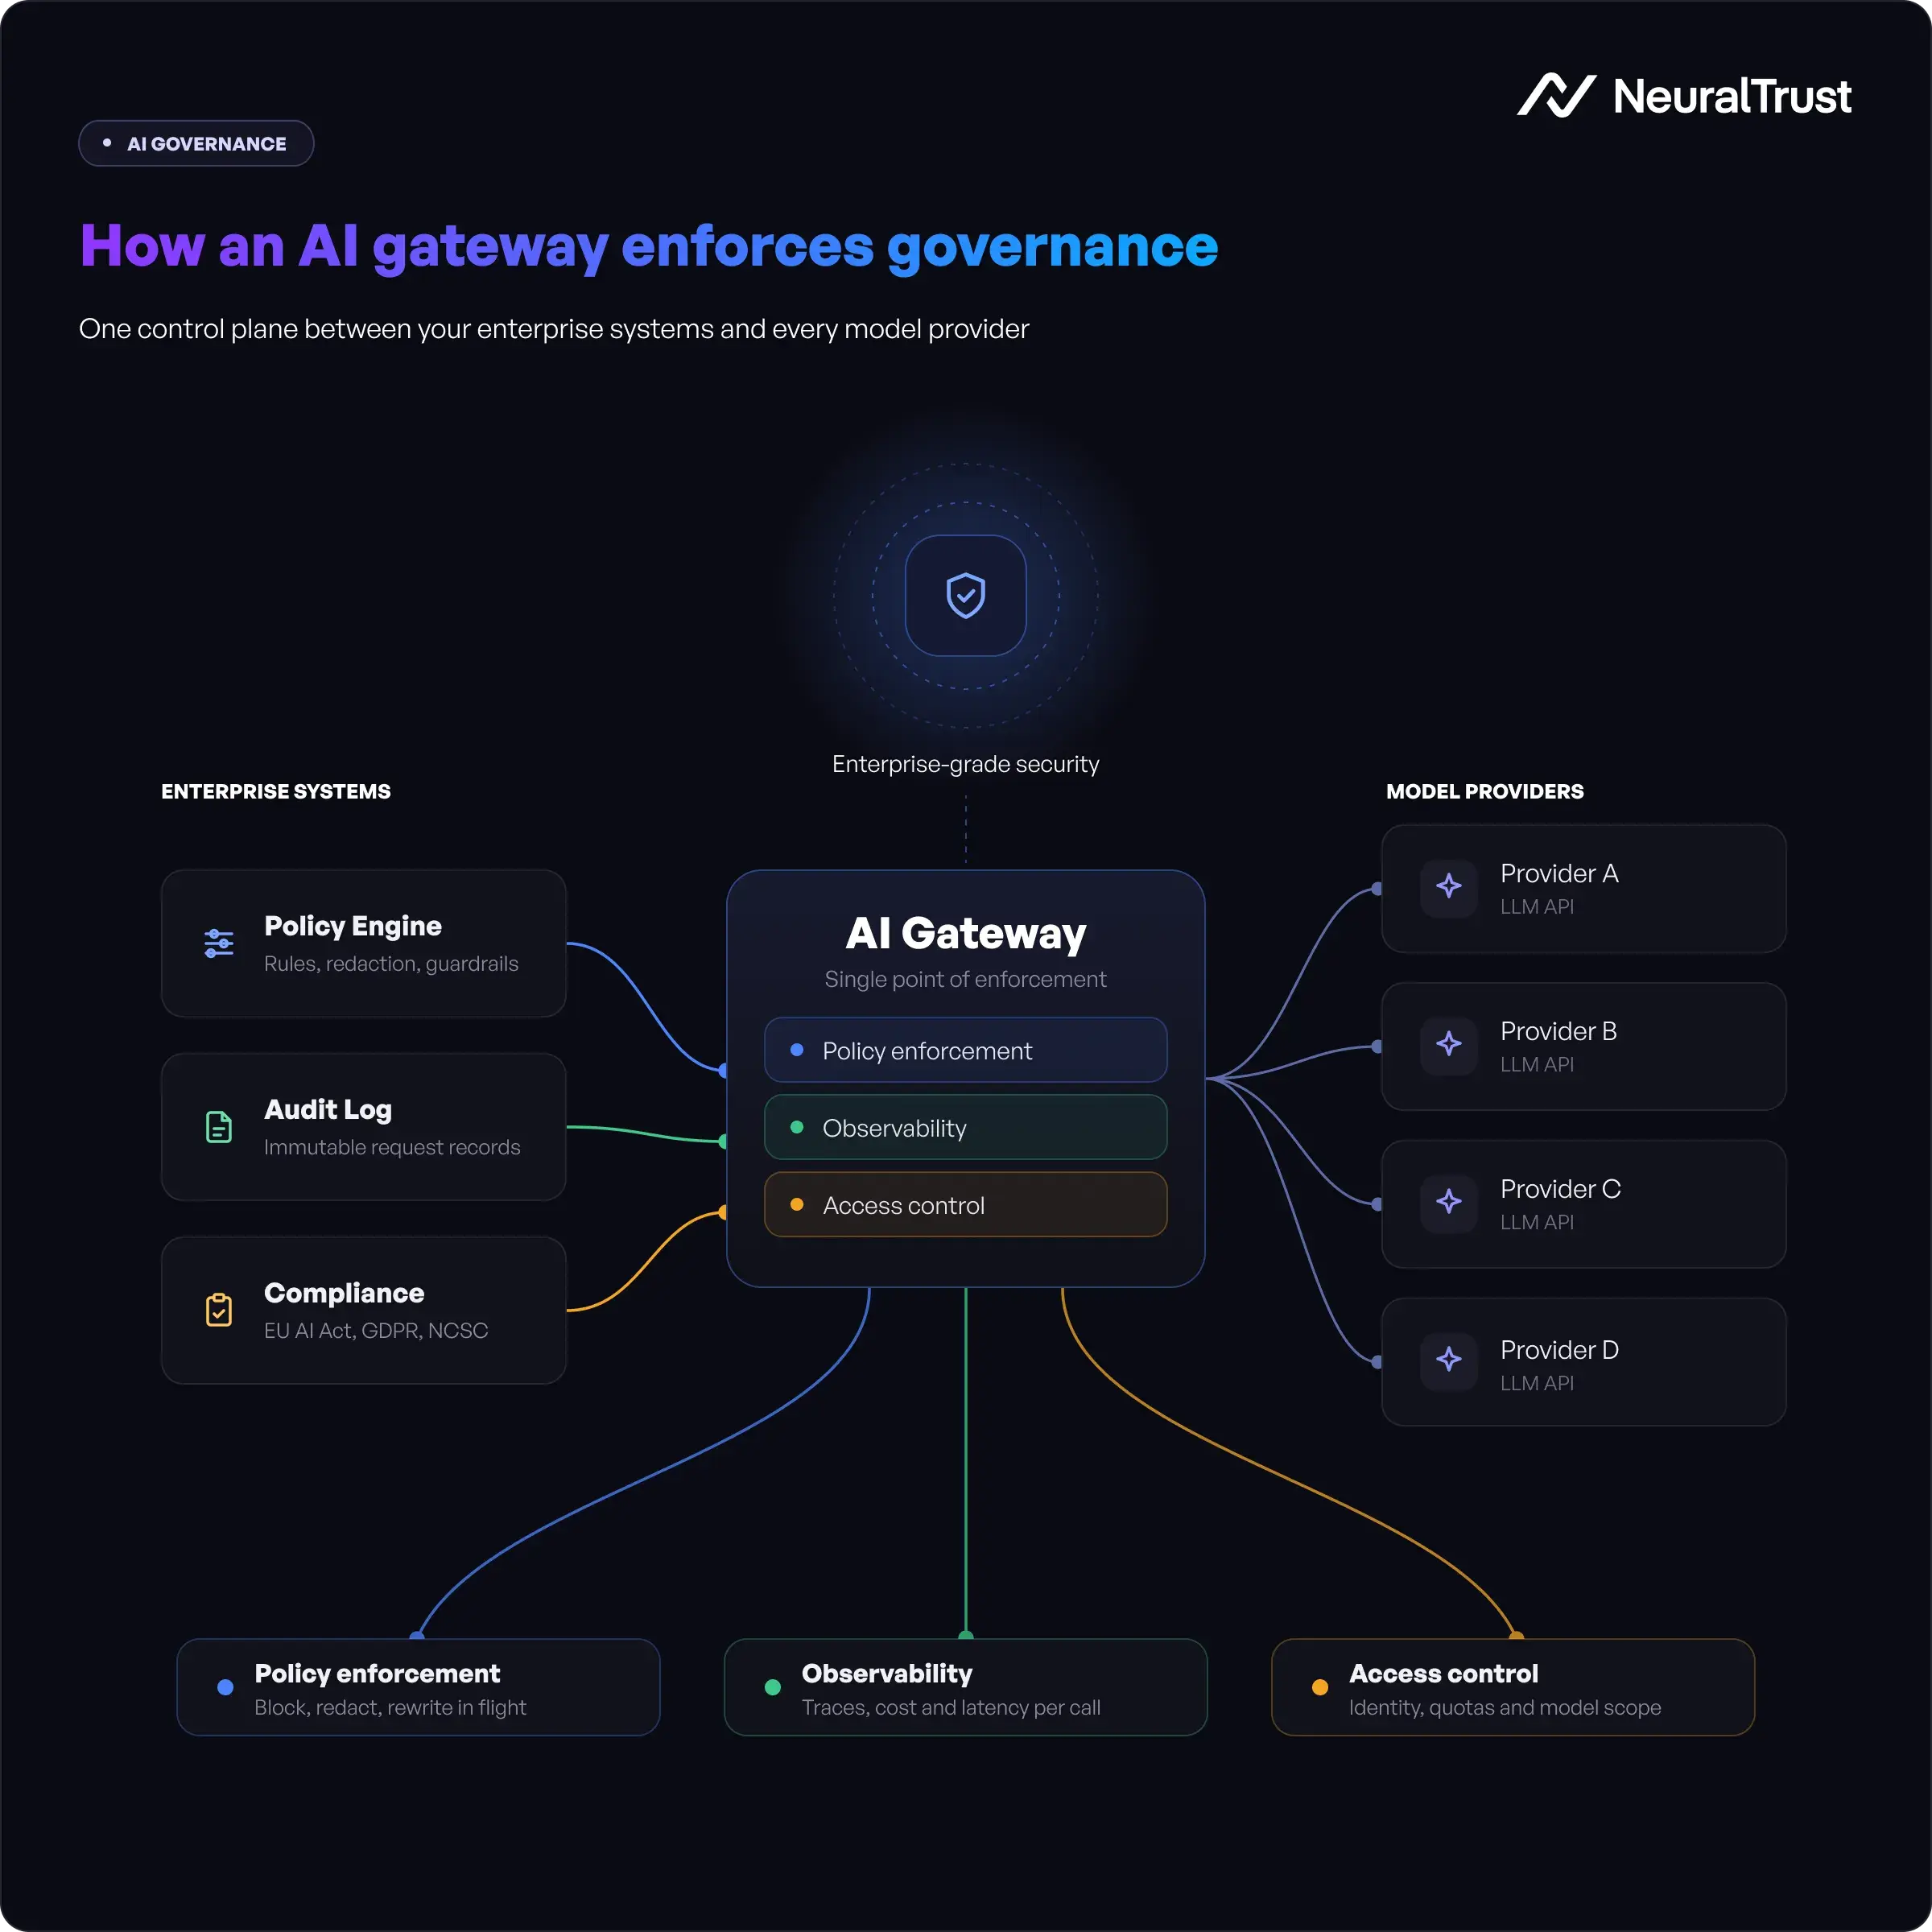
An AI gateway closes that gap. It sits between your enterprise applications and your model providers, and it is the only layer in the stack that sees every single model interaction regardless of which application, which team, or which model triggered it. That position is what makes it the right place to enforce AI governance at scale.
What Enterprise AI Governance Actually Requires
AI governance is not one problem. It is four distinct problems that a mature governance framework needs to solve simultaneously.
1. Policy Enforcement
Every enterprise AI deployment carries an implicit policy: what the model is allowed to say, what data it is allowed to see, who is allowed to query it, and what outputs it is allowed to return. Governance requires that policy to be enforced in real time on every interaction, not reviewed after the fact. This means technical controls, not review processes.
2. Audit Trails and Observability
Regulators, auditors, and boards need to know what happened. That requires structured, immutable records of model interactions: what was sent, what was returned, what policy was applied, and what was blocked. LLM observability (the ability to monitor and analyse AI application behaviour at the interaction level) is not optional for enterprise governance. It is the audit trail.
3. Access Control and Identity Management
Not every employee, system, or application should have access to every model or every data source. Enterprise AI governance requires identity-aware access control that extends into the AI layer, to see which users can query which models, which applications can access which context sources, and which agents can call which tools.
4. Compliance and Regulatory Reporting
The EU AI Act, GDPR, NCSC AI Framework, and a growing number of industry regulations, impose specific obligations on organisations deploying AI systems. Compliance requires not only that controls exist, but that their operation can be demonstrated through logs, reports, and audit outputs. Governance infrastructure must generate compliance evidence, not just enforce policy.
The table below maps these four governance requirements to the technical controls an enterprise AI gateway provides:
| Governance requirement | What it means in practice | How an AI gateway addresses it |
|---|---|---|
| Policy enforcement | Block disallowed content, enforce prompt constraints, apply model routing rules | Real-time inspection of every prompt and completion with configurable policy engine |
| Audit trails | Immutable record of all model interactions, policy decisions, and blocked requests | Structured logging of every request with metadata, policy outcome, and model response |
| Access control | Restrict model and data access by user, role, team, and application | API key management, role-based routing, per-application token quotas |
| Compliance reporting | Demonstrable evidence of controls for regulators and auditors | Compliance dashboards, exportable logs, and integration with SIEM and ticketing systems |
How an AI Gateway Delivers Enterprise AI Governance
An AI gateway is purpose-built for the specific characteristics of LLM-based systems: high-volume, variable-length, semantically complex interactions that carry both security and compliance risk at every step.
Policy Enforcement at the Prompt Layer
The most important governance control in an AI deployment is the one that runs before the model does. An AI gateway intercepts every incoming prompt, evaluates it against configured policy, and decides in real time whether to pass it through, modify it, or block it.
Policy enforcement at the prompt layer covers:
- Content policy: blocking requests that ask the model to generate harmful, illegal, or policy-violating outputs
- Data governance: detecting and redacting sensitive data (personally identifiable information, payment card data, internal credentials) before it reaches an external model provider
- Prompt injection defence: identifying adversarial inputs designed to manipulate model behaviour or extract system context
- Scope enforcement: ensuring that model interactions remain within the defined purpose of the application: a customer support bot cannot be turned into a general research tool through user manipulation
According to OWASP's LLM Top 10, prompt injection is the leading vulnerability in LLM-powered applications. Gateway-level prompt inspection is the primary defence against it, and unlike application-layer controls, it applies consistently across every AI application regardless of how each one is built.
The same policy engine that enforces content rules also governs model selection. Enterprise AI governance often requires that certain data types route to on-premises or private models rather than external providers. A gateway enforces this routing policy automatically: regulated data stays within approved boundaries without requiring developers to implement routing logic in every application.
LLM Observability as a Governance Instrument
LLM observability is the practice of monitoring AI application behaviour at the interaction level: what prompts were sent, what completions were returned, how long they took, what they cost, and whether they triggered any policy rules. For enterprise governance, observability is the audit infrastructure.
Without gateway-level observability, an enterprise cannot answer the questions that governance requires:
- Which applications are sending data to which model providers?
- Which users generated the most sensitive queries last month?
- How many prompt injection attempts were blocked across the estate?
- Which AI applications are operating outside their defined scope?
- What evidence do we have that our content policy was enforced on a specific date?
An AI gateway centralises observability across the entire AI estate. Because it sits upstream of every model provider, it generates a unified record of model interactions regardless of which application, SDK, or team generated them. That unified record is what makes AI governance demonstrable rather than aspirational.
Observability data from the gateway feeds into:
- Real-time alerting for policy violations and anomalous behaviour
- Compliance dashboards that aggregate policy enforcement metrics
- SIEM integration for security operations teams
- Audit exports for regulatory review
- Trend analysis that identifies governance gaps before they become incidents
Identity-Aware Access Control for AI
Standard API key management is not sufficient for enterprise AI governance. A single API key shared across a team or application gives everyone the same level of model access regardless of role, clearance, or data handling obligations. Gateway-level access control solves this by making model access identity-aware.
An enterprise AI gateway applies access controls at multiple levels:
- Per-user controls: individual users have different token quotas, model access permissions, and content policy thresholds based on role
- Per-application controls: different AI applications route to different model tiers with different policy configurations
- Per-agent controls: autonomous AI agents have hard limits on tool calls, context retrieval, and token consumption per session
- Per-data-type controls: requests carrying regulated data route to approved models only, with additional logging and stricter output filters applied
This granularity is what enterprise governance actually requires. A CISO cannot tell a board that AI access is controlled if that control amounts to a shared API key managed by an individual developer. Gateway-level access control replaces informal key management with a policy-governed infrastructure layer that security and compliance teams can audit and report on.
Compliance Reporting from the Infrastructure Layer
An AI gateway generates structured audit data as a byproduct of normal operation. Every request carries metadata: timestamp, source application, user or service identity, model routing decision, token counts, policy outcomes, and whether any content was flagged or blocked. That metadata is the raw material for compliance reporting.
At the infrastructure level, compliance reporting from a gateway covers:
- Data residency evidence: proof that regulated data never transited an unapproved provider
- Content policy enforcement logs: timestamped records of every blocked or modified request
- Access logs: a complete record of which users and applications queried which models
- Incident records: structured data on anomalies, policy violations, and blocked prompt injection attempts
- Cost attribution: per-team and per-application spend data that supports AI procurement governance
For organisations subject to periodic audits, this infrastructure-level evidence is significantly stronger than application-level logs because it is independent of individual development teams and consistent across the entire AI estate.
Enterprise AI Governance Under the EU AI Act, GDPR, and NCSC
The three regulatory frameworks most relevant to European enterprise AI deployments each impose governance obligations that an AI gateway directly addresses.
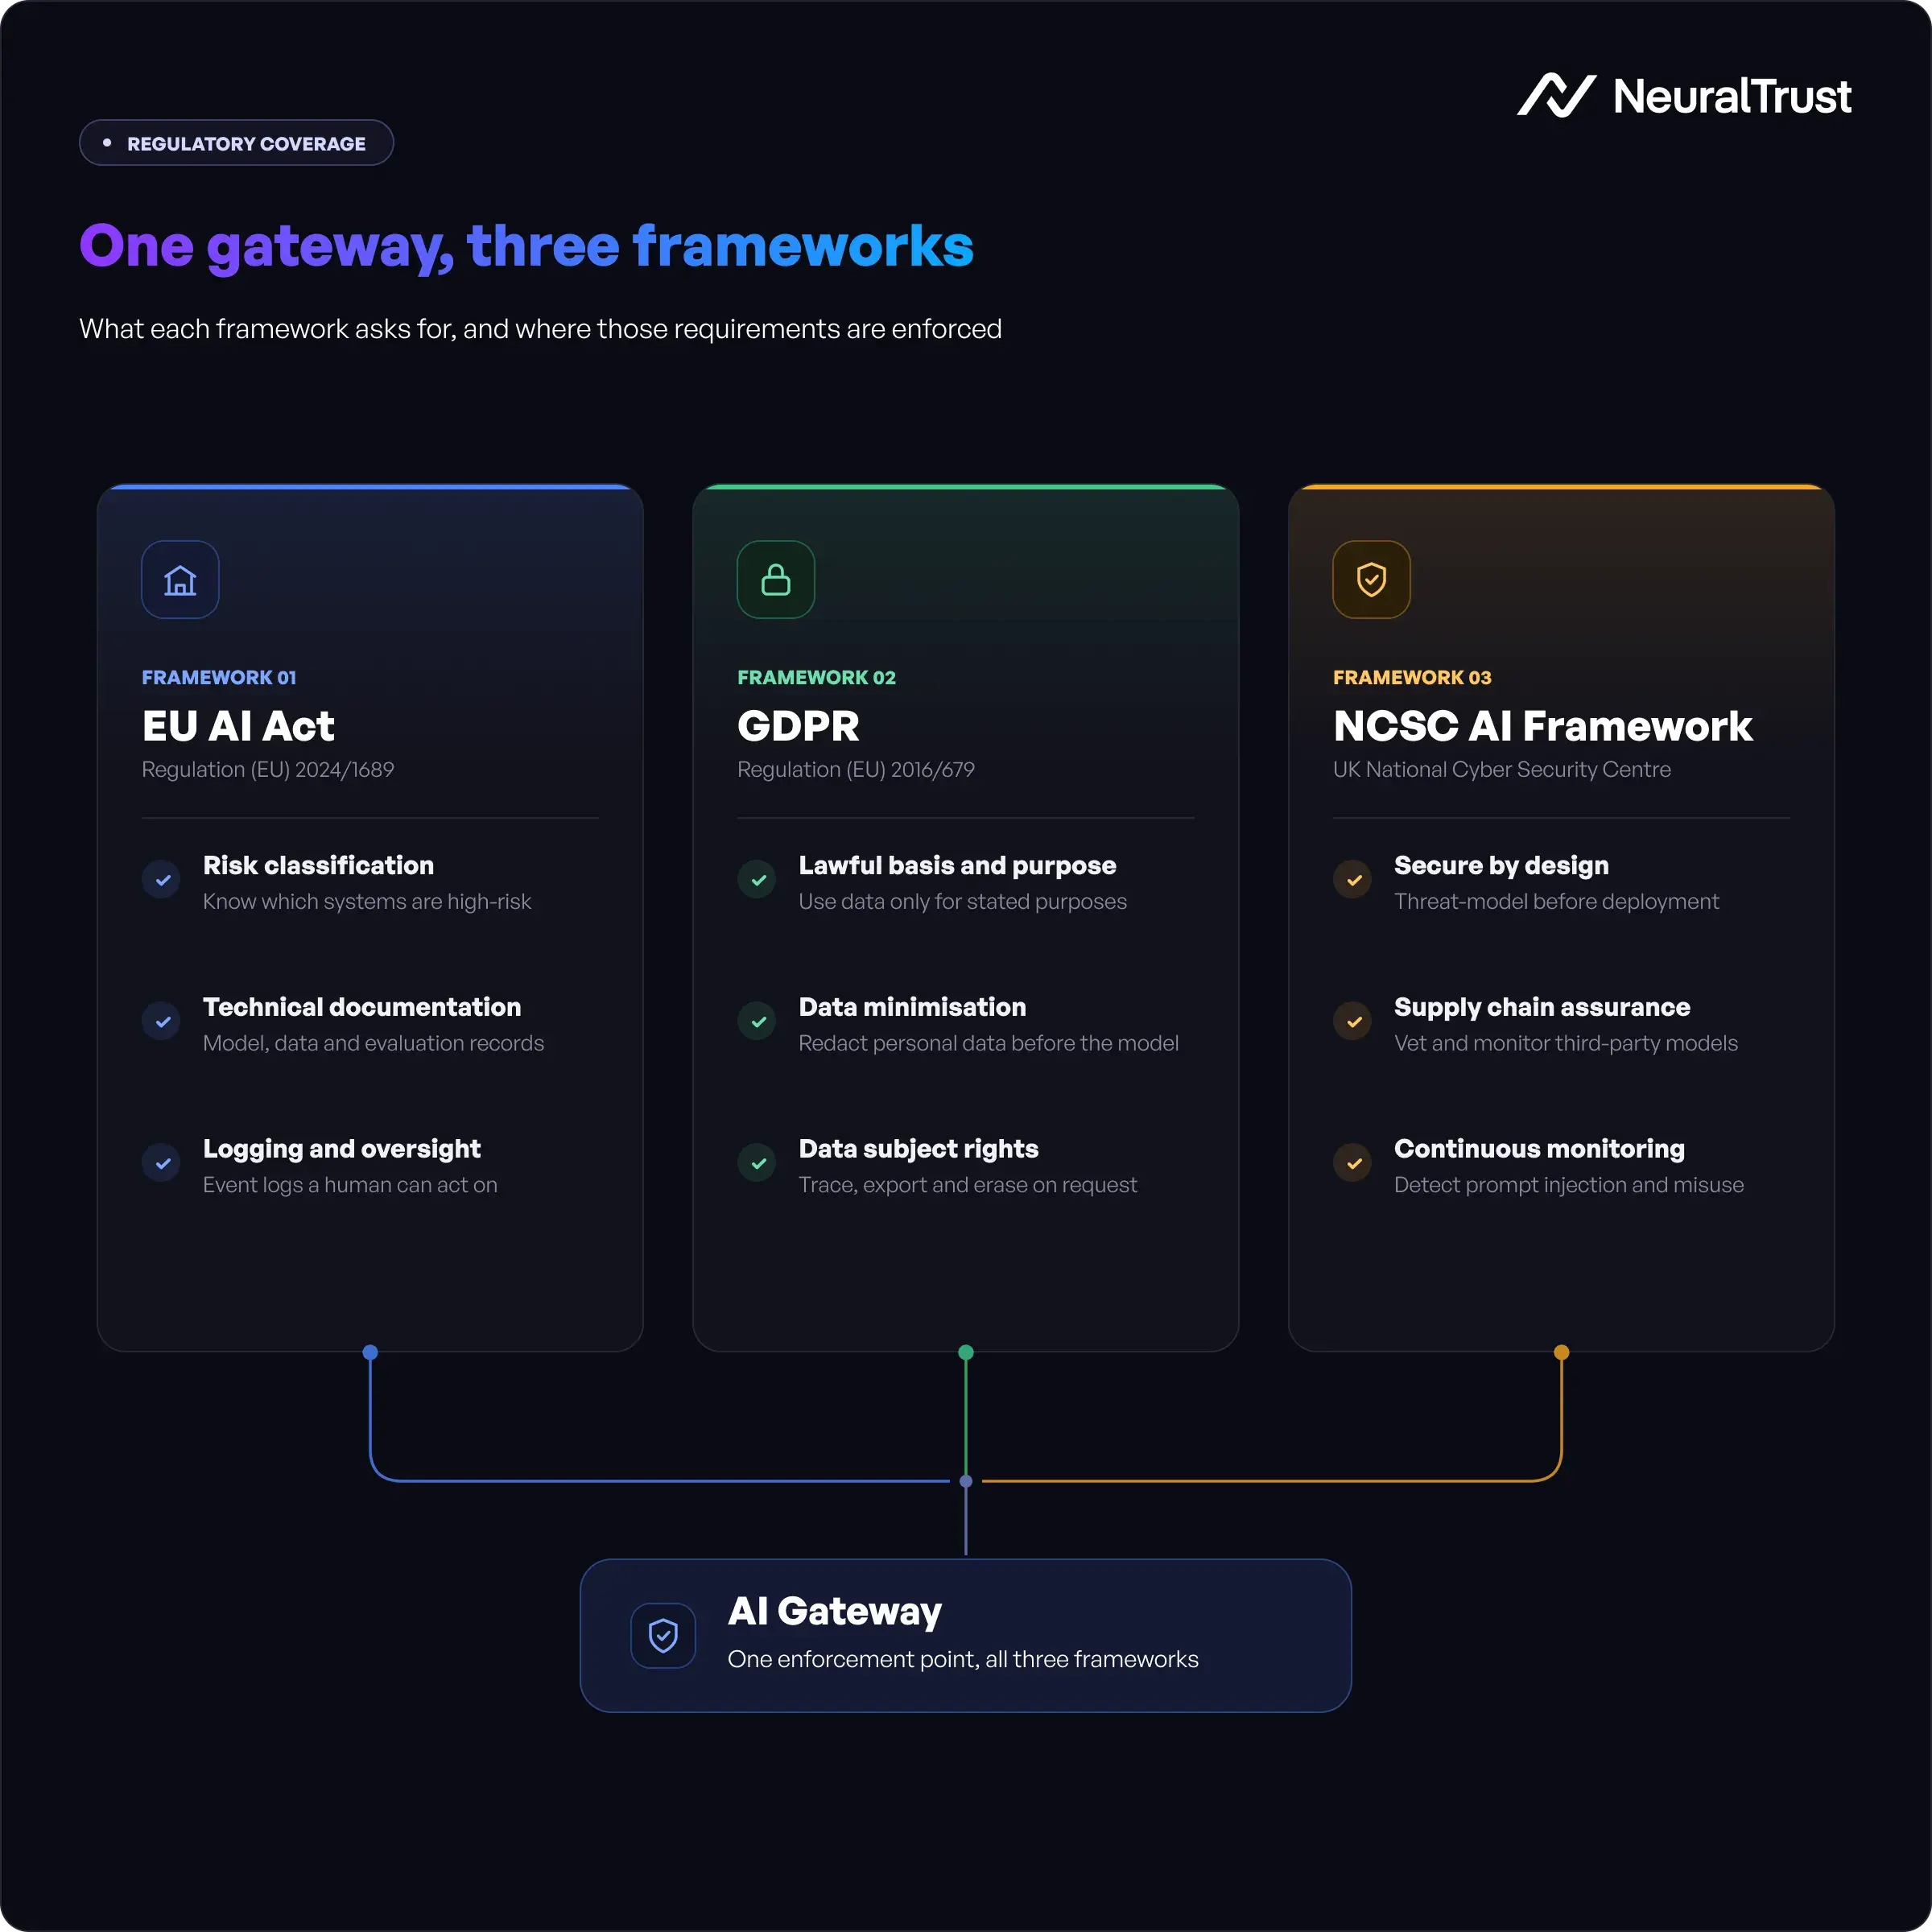
| Regulatory framework | Key AI governance obligation | How an AI gateway addresses it |
|---|---|---|
| EU AI Act (High-Risk AI) | Risk management system, technical documentation, logging, human oversight | Gateway-level policy enforcement, immutable interaction logs, human-reviewable audit outputs |
| EU AI Act (General Purpose AI) | Transparency requirements, adversarial robustness testing | Content policy enforcement, prompt injection detection, model behaviour logging |
| GDPR | Data minimisation, purpose limitation, cross-border transfer controls | PII detection and redaction before model calls, jurisdictional routing, provider-level data governance |
| NCSC AI Framework | Secure AI deployment, monitoring for misuse, supply chain risk | Runtime monitoring, anomaly detection, model provenance tracking |
EU AI Act Obligations
The EU AI Act classifies AI systems by risk level and imposes proportionate obligations on each tier. High-risk AI systems (including those used in recruitment, credit scoring, education, law enforcement, and critical infrastructure) must implement risk management systems, maintain technical documentation, provide audit logs, and ensure human oversight mechanisms are in place.
An enterprise AI gateway addresses these obligations at the infrastructure layer. The risk management system is the policy engine: it enforces the controls that the Act requires. The audit logs are the gateway interaction logs: structured, complete, and exportable. Human oversight is enabled through the observability layer: policy violations surface in real time for human review before they escalate.
GDPR Obligations
GDPR's data minimisation and purpose limitation principles apply directly to AI deployments. Sending personal data to an external LLM provider to answer a customer query is a data processing activity that requires a lawful basis and a data processing agreement. If that personal data is more than necessary for the stated purpose, the processing may breach data minimisation requirements.
A gateway enforces data minimisation at the point of processing: PII detection rules identify personal data in prompts before the request reaches an external provider, and redaction policies strip or substitute it. Jurisdictional routing ensures that data from EU data subjects routes only to EU-approved providers, supporting GDPR's transfer restrictions without requiring application-level implementation.
NCSC AI Framework
The UK National Cyber Security Centre's guidelines for AI security include requirements for secure deployment, monitoring for misuse, and supply chain risk management. An AI gateway directly supports each of these: it provides the monitoring layer, the policy enforcement infrastructure, and the model routing controls that prevent unauthorised model provider substitution.
Building an Enterprise AI Governance Framework on an AI Gateway
Deploying an AI gateway is the foundation. The governance framework is what you build on top of it. The following sequence gives enterprise security and compliance teams a practical path from deployment to full governance coverage.
-
Deploy the gateway as a central proxy for all model traffic: Route every AI application through a single gateway endpoint. This is the prerequisite for every subsequent governance control, you cannot enforce policy on traffic you cannot see.
-
Inventory your AI applications and define their governance profiles: For each application, document: which model it uses, what data it processes, who has access, and what policy constraints apply. This inventory becomes the source of truth for gateway policy configuration.
-
Configure content policy rules for each application: Define what each application is and is not allowed to send and receive. Apply stricter policies to applications that handle regulated data and default policies to lower-risk internal tools.
-
Enable PII detection and routing controls for data-sensitive applications: Configure detection rules for the data types your applications handle (health data, financial data, personal identifiers) and define routing policies that keep regulated data within approved provider boundaries.
-
Set token budgets and rate limits by user, application, and agent: This simultaneously controls cost and enforces scope, an application that regularly exceeds its token budget may be handling prompts outside its intended purpose.
-
Activate LLM observability dashboards and connect to your SIEM: Governance requires visibility. Connect the gateway's observability output to your existing security monitoring infrastructure so AI traffic appears alongside network and endpoint telemetry.
-
Run a baseline audit of the first 30 days of gateway logs: Use the structured interaction logs to identify governance gaps: applications routing outside policy, users generating anomalous query volumes, or content policy rules triggering at unexpected rates.
-
Schedule quarterly governance reviews using gateway-generated compliance reports: Treat gateway audit exports as the primary evidence package for regulatory reviews, board reporting, and internal compliance cycles.
For a deeper technical view of how the gateway architecture supports each of these steps, see AI Gateway Architecture: How It Works Under the Hood and AI Gateway Security: Protecting LLM Traffic.
TrustGate: Enterprise AI Governance at the Infrastructure Layer
TrustGate is NeuralTrust's AI gateway. It implements the full enterprise governance stack described in this article from a single infrastructure deployment, applying consistently to every AI application and every model in your stack.
Policy enforcement is configured declaratively using a policy engine that applies to every prompt and completion. Content policy rules, PII detection, prompt injection filters, and scope constraints are defined once and enforced on all traffic. No application-level SDK changes or per-feature instrumentation required.
LLM observability is built into the data plane. Every request generates a structured log entry containing the full interaction metadata: timestamp, source identity, routing decision, token counts, policy outcome, latency, and cost. These logs feed into the observability dashboard and can be exported to SIEM platforms and compliance reporting tools.
Access control is managed through API key policies, role-based routing rules, and per-application token quotas. Token budgets set hard limits on per-user, per-application, and per-agent consumption. Rate limits protect against runaway spend and scope violation simultaneously. For more on cost governance through the gateway, see How an AI Gateway Reduces LLM Costs.
Jurisdictional routing keeps regulated data within approved geographic boundaries. Routing rules evaluate request metadata and data classification tags to determine which provider receives each request, enforcing data residency policy without developer-level implementation in each application.
Audit exports produce structured compliance packages from the interaction log. Audit exports include policy violation summaries, content blocking records, access logs, and cost attribution reports, covering the evidence requirements of EU AI Act technical documentation, GDPR processing records, and NCSC security audit requirements.
TrustGate runs in your own infrastructure (Kubernetes, VPC, or on-premises) so model traffic never leaves your environment. The control plane manages policy centrally without touching application data.
The AI gateway cluster covers related governance and architecture topics in depth:
- What Is an AI Gateway?
- AI Gateway vs MCP Gateway
- AI Gateway Security
- AI Gateway Architecture
- LLM Observability with an AI Gateway
- How an AI Gateway Reduces LLM Costs
Try TrustGate Free Today
Enterprise AI governance starts with visibility. Deploy TrustGate in your own environment and get a complete picture of every model interaction across your AI estate (with policy enforcement, LLM observability, and access control active) in minutes. No sales process. No credit card.
FAQs about AI Gateway Enterprise Governance
1. What is an AI gateway in the context of enterprise AI governance?
An AI gateway is an infrastructure layer that sits between enterprise applications and LLM providers, intercepting every model interaction and applying policy controls in real time.
In the context of AI governance, it is the enforcement layer that translates governance policies into technical controls. It blocks policy-violating requests, generates audit trails, manages access permissions, and produces compliance reporting data. Without a gateway, enterprise AI governance exists only as documentation, the policies are defined but not enforced at the point of model interaction.
2. How does an AI gateway help with EU AI Act compliance?
The EU AI Act requires organisations deploying high-risk AI systems to implement risk management systems, maintain technical documentation, log AI system operations, and enable human oversight. An AI gateway addresses each of these obligations at the infrastructure layer. The policy engine is the technical risk management control. The interaction logs are the technical documentation. The observability dashboard enables human oversight by surfacing policy violations and anomalous behaviour in real time.
For general-purpose AI systems, the gateway's prompt injection defence and content policy enforcement support the adversarial robustness obligations the Act imposes on model providers and deployers alike.
3. What is LLM observability and why does it matter for AI governance?
LLM observability is the practice of monitoring and analysing AI application behaviour at the interaction level, capturing what was sent to a model, what it returned, how it behaved, and whether it complied with policy.
For enterprise AI governance, LLM observability is the audit infrastructure. It generates the structured interaction records that regulators, auditors, and compliance teams need to verify that governance controls are working. An AI gateway provides LLM observability centrally across the entire AI estate, independently of how individual applications are built.
4. Can an AI gateway enforce GDPR data minimisation for LLM applications?
Yes, through PII detection and redaction at the prompt layer. A configured AI gateway inspects every outgoing request for personal data (names, email addresses, national identifiers, financial data) and applies redaction or substitution rules before the request reaches an external model provider.
This enforces GDPR's data minimisation principle at the point of processing, without requiring developers to implement data handling logic in each application individually. Jurisdictional routing rules complement this by ensuring that requests involving EU personal data route only to EU-approved providers, supporting GDPR transfer restrictions.
5. How does gateway-level access control differ from standard API key management?
Standard API key management assigns a single credential to an application or team, giving all users of that application identical model access regardless of role or data handling obligations. Gateway-level access control is identity-aware: it enforces per-user token quotas, role-based routing policies, per-application model restrictions, and per-agent tool call limits.
This granularity is what enterprise AI governance requires: a shared API key is not a governance control, it is a single point of failure. The gateway replaces it with a structured access policy that can be audited, reported on, and adjusted without application changes.
6. What is the difference between an AI gateway and a traditional API gateway for AI governance purposes?
A traditional API gateway manages HTTP traffic: routing, authentication, rate limiting, and load balancing across web services. It operates at the request level and has no understanding of the semantic content of the payloads it handles.
An AI gateway operates at the content level: it understands the structure of LLM prompts and completions, can inspect their meaning, apply natural language policy rules, detect adversarial inputs, and enforce governance controls that depend on what is being said rather than just how much traffic is flowing.
For AI governance, this content-level understanding is what distinguishes an AI gateway from a general-purpose API proxy. See AI Gateway Architecture: How It Works Under the Hood for a technical comparison.
About the Author
Roger Howroyd is Head of Global SEO and AI at NeuralTrust, where he leads the company's search strategy across SEO, AEO, GEO, and LLM optimization. He specializes in AI-powered search, content strategy, and SEM. Connect on LinkedIn.
NeuralTrust is an AI agent security platform recognised in the Gartner Emerging Market Quadrant for AI Application Security 2026 (Pioneer), the Gartner Hype Cycle for Application Security 2026, the Gartner Hype Cycle for AI Governance Technologies 2026, and the KuppingerCole Leadership Compass for Generative AI Defense. ISO 27001 certified. Headquartered in Barcelona.
Sources
- OWASP Top 10 for Large Language Model Applications: OWASP
- Gartner Hype Cycle for AI Governance Technologies, 2026: Gartner (Strategic Planning Assumption: by 2028, loss of control over AI agents will be the top concern for 40% of Fortune 1000 organisations)
- EU Artificial Intelligence Act: European Parliament and Council
- NCSC Guidance on AI: UK National Cyber Security Centre
- NIST AI Risk Management Framework: National Institute of Standards and Technology