What's the difference between an AI gateway and an MCP gateway?
An AI gateway is a reverse proxy that sits in front of large language model calls, handling routing across providers, rate limits, cost tracking, and prompt- or response-level security. An MCP gateway is a control layer purpose-built for MCP (Model Context Protocol) traffic, it governs which tools and data sources an AI agent is allowed to reach once the model decides to act, enforcing authentication, per-tool authorization, and audit logging on that agent-to-tool traffic.
The two sit at different points on the same request path. An AI gateway watches the "thinking" traffic going into and out of the model. An MCP gateway watches the "acting" traffic that happens after the model decides to call a tool, query a database, or trigger a workflow.
They overlap in some functions, both provide authentication, observability, and policy enforcement, but they inspect fundamentally different payloads, and most production agent architectures that use MCP end up needing both.
TL;DR - Key Takeaways
- An AI gateway sits in front of LLM API calls (OpenAI, Anthropic, Bedrock, Gemini, etc.), managing routing, provider fallback, token-based rate limits, cost visibility, and prompt/response security policies.
- An MCP gateway sits in front of Model Context Protocol traffic, governing which tools and data an agent can invoke, enforcing per-tool role-based access control, and logging every call for audit.
- They are complementary, not competing: the AI gateway secures the model call, the MCP gateway secures the tool call that follows it.
- If your agents only call a model, an AI gateway alone may be enough. If your agents call MCP servers to use tools or fetch data, you need MCP-layer inspection too.
- Most production enterprise agent deployments end up running both layers together, often on the same control plane, since a threat that slips past one layer can still be caught by the other.
- MCP itself is an open standard, originally introduced by Anthropic in November 2024 and since donated to the Agentic AI Foundation, a directed fund under the Linux Foundation, to keep its governance vendor-neutral.
What is an MCP gateway?
An MCP gateway is a specialized gateway that sits between AI agents and the MCP servers that expose tools, resources, and prompts to them. The Model Context Protocol (MCP) itself is an open standard, introduced by Anthropic and now stewarded by the Agentic AI Foundation under the Linux Foundation, that lets an AI application discover and invoke external tools and data sources through a consistent client-server interface, instead of every team writing bespoke integration code for every combination of model and system.
MCP solves what's often called the "M×N integration problem": without a shared protocol, every AI application (M) needs a custom connector for every tool or data source (N). MCP collapses that into an "M+N" problem, build one MCP client in your agent and one MCP server per system, and any compliant agent can use any compliant server.
"Nearly 50% of software companies are already using MCP in production, with 19% having deployed at broad scale."
Source: Stacklok, State of Model Context Protocol in Software 2026 (survey of 100 senior technical leaders)
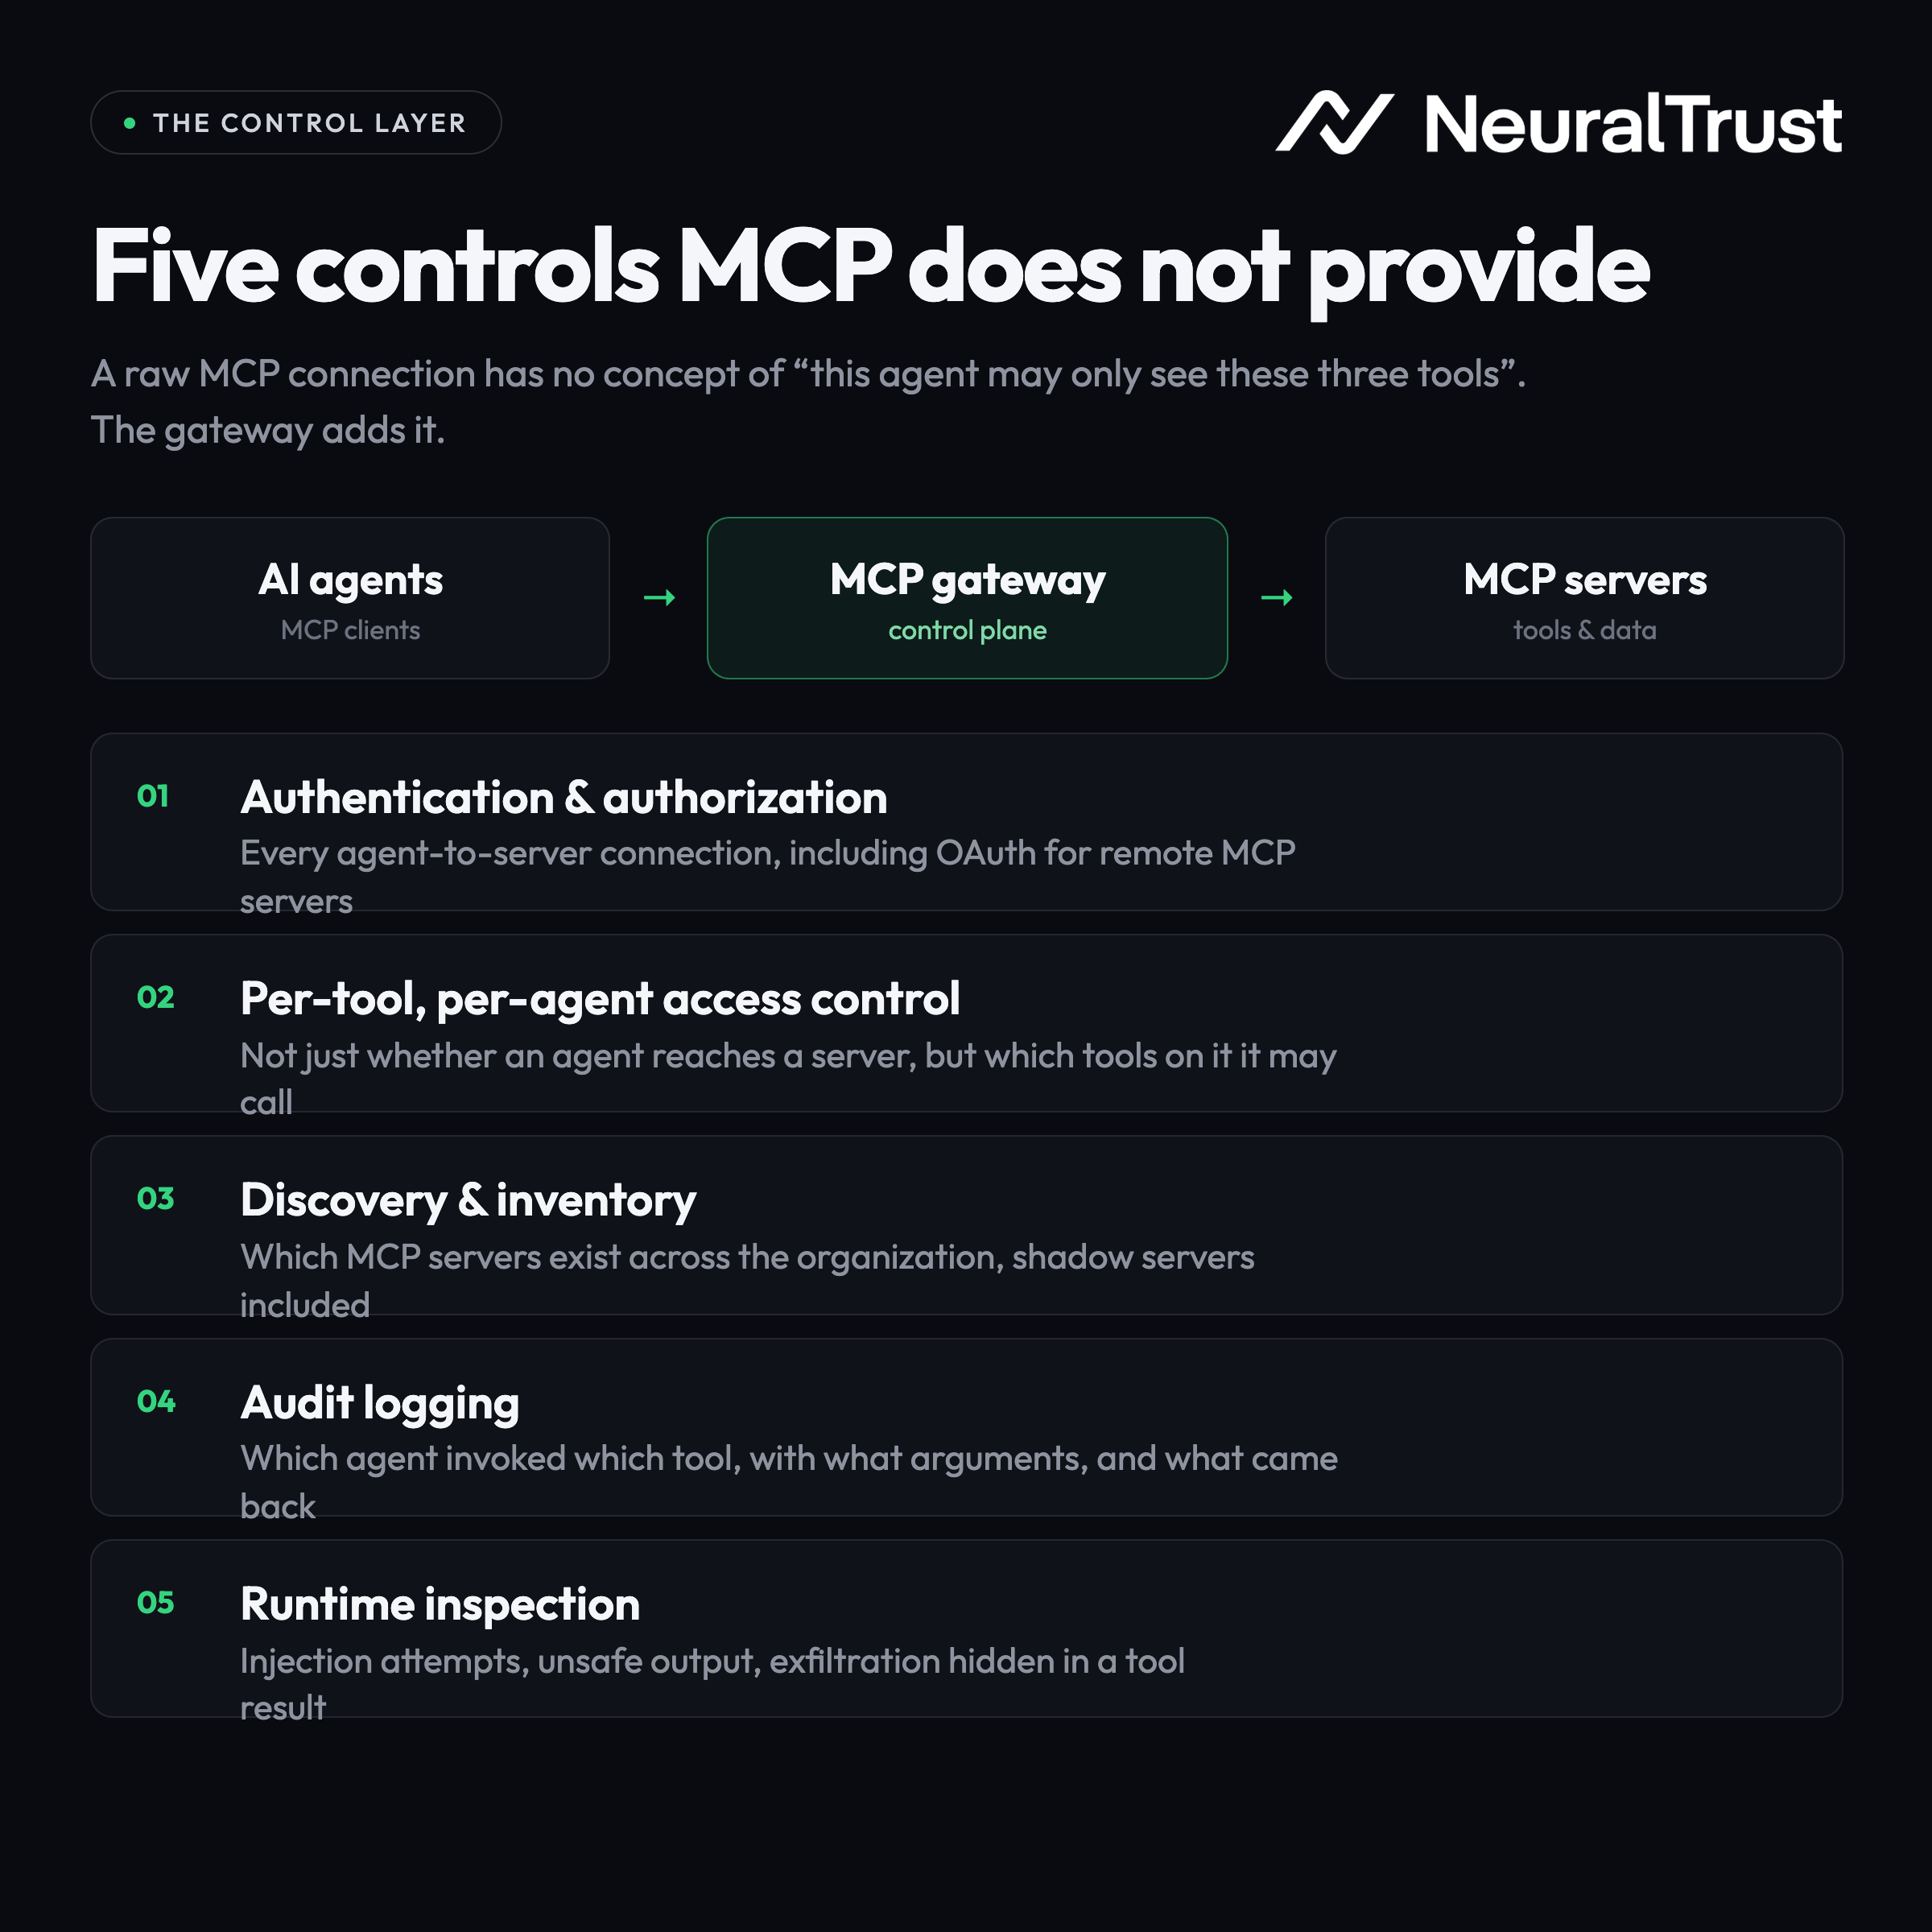
That flexibility creates a new governance gap. A raw MCP connection has no built-in concept of "this agent should only see these three tools" or "log every call this agent makes to the finance database."
An MCP gateway closes that gap by adding a production control layer on top of MCP traffic:
- Authentication and authorization for every agent-to-server connection, including OAuth flows for remote MCP servers.
- Per-tool, per-agent access control, deciding not just whether an agent can reach a server, but which specific tools on that server it can call.
- Discovery and inventory of which MCP servers exist across the organization, including unsanctioned or "shadow" servers.
- Audit logging that records who (or which agent, acting on whose behalf) invoked which tool, with what arguments, and what came back.
- Runtime inspection of tool calls and tool results for injection attempts, unsafe outputs, or data exfiltration hidden in a tool response.
What is an AI gateway?
An AI gateway is a reverse proxy purpose-built for traffic to and from large language models. Instead of every application team wiring its own API keys and error handling into each model provider's SDK, requests are routed through a single control point that normalizes multiple providers behind one interface, typically an OpenAI-compatible surface that can transparently point at OpenAI, Anthropic, Azure OpenAI, Bedrock, Gemini, or self-hosted models.
Because it operates on model traffic specifically, an AI gateway handles concerns that a general-purpose API gateway was never designed for: token-based rate limits and quotas instead of request counts, streaming response handling, model fallback and load balancing across providers, semantic caching, cost attribution per team or per application, and policy checks on the prompts going in and the completions coming out, things like jailbreak detection, PII masking, and toxicity filtering.
An AI gateway does not, on its own, see what happens after the model decides to call a tool. If the model's response includes a tool call, that call typically leaves the AI gateway's field of view and goes to wherever the agent's tool-execution logic lives, which is exactly the traffic an MCP gateway is built to govern.
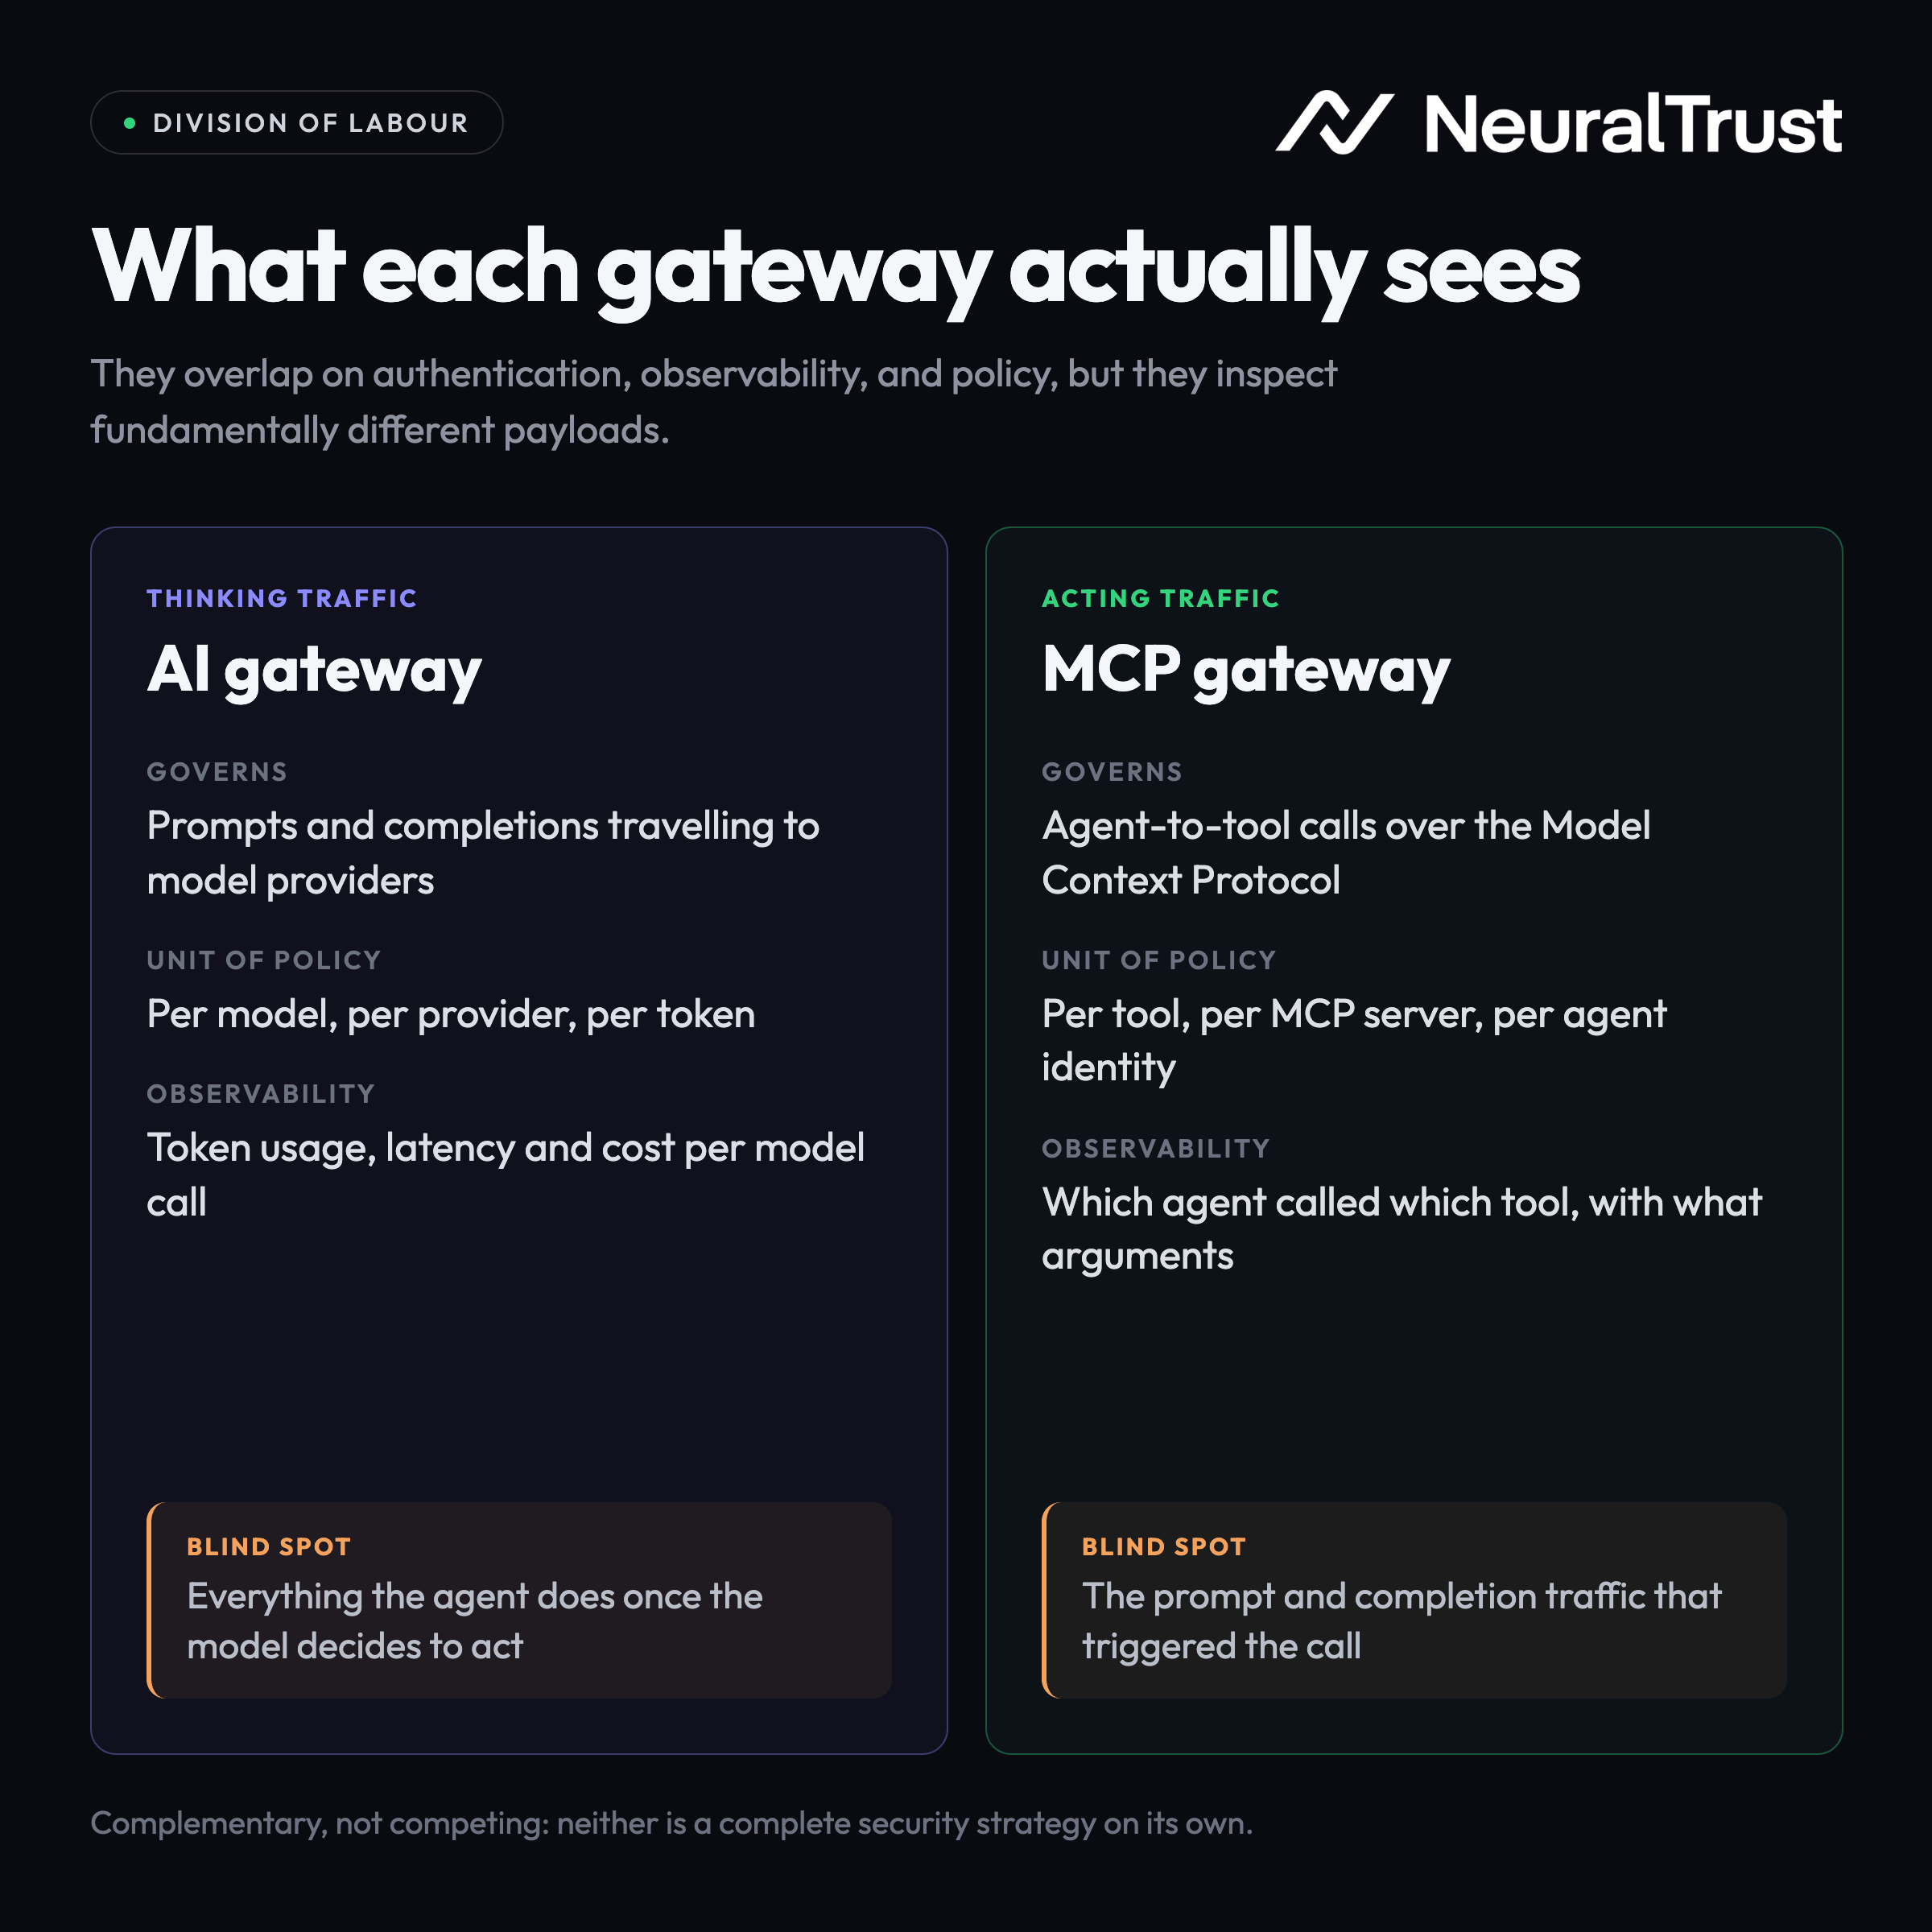
AI gateway vs MCP gateway: the key differences
| Feature | AI Gateway | MCP Gateway |
|---|---|---|
| Traffic it governs | Model/LLM API calls (prompts, completions) | Agent-to-tool calls over the Model Context Protocol |
| Position in the request path | In front of the model call | In front of tool execution, after the model decides to act |
| Core controls | Routing, provider fallback, rate limits, cost tracking, caching | Authentication, per-tool authorization, tool/server inventory, audit logs |
| Security focus | Prompt injection in inputs, unsafe or leaking outputs | Malicious or over-scoped tool use, unauthorized data access, tool-result injection |
| Typical unit of policy | Per model, per provider, per token | Per tool, per MCP server, per agent identity |
| Observability output | Token usage, latency, cost per model call | Which agent called which tool, with what arguments, and the result |
| Failure mode if missing | Runaway spend, provider outages with no fallback, unfiltered prompts/outputs | Agents reaching tools or data they shouldn't, no record of what an agent actually did |
Where each one sits in the architecture
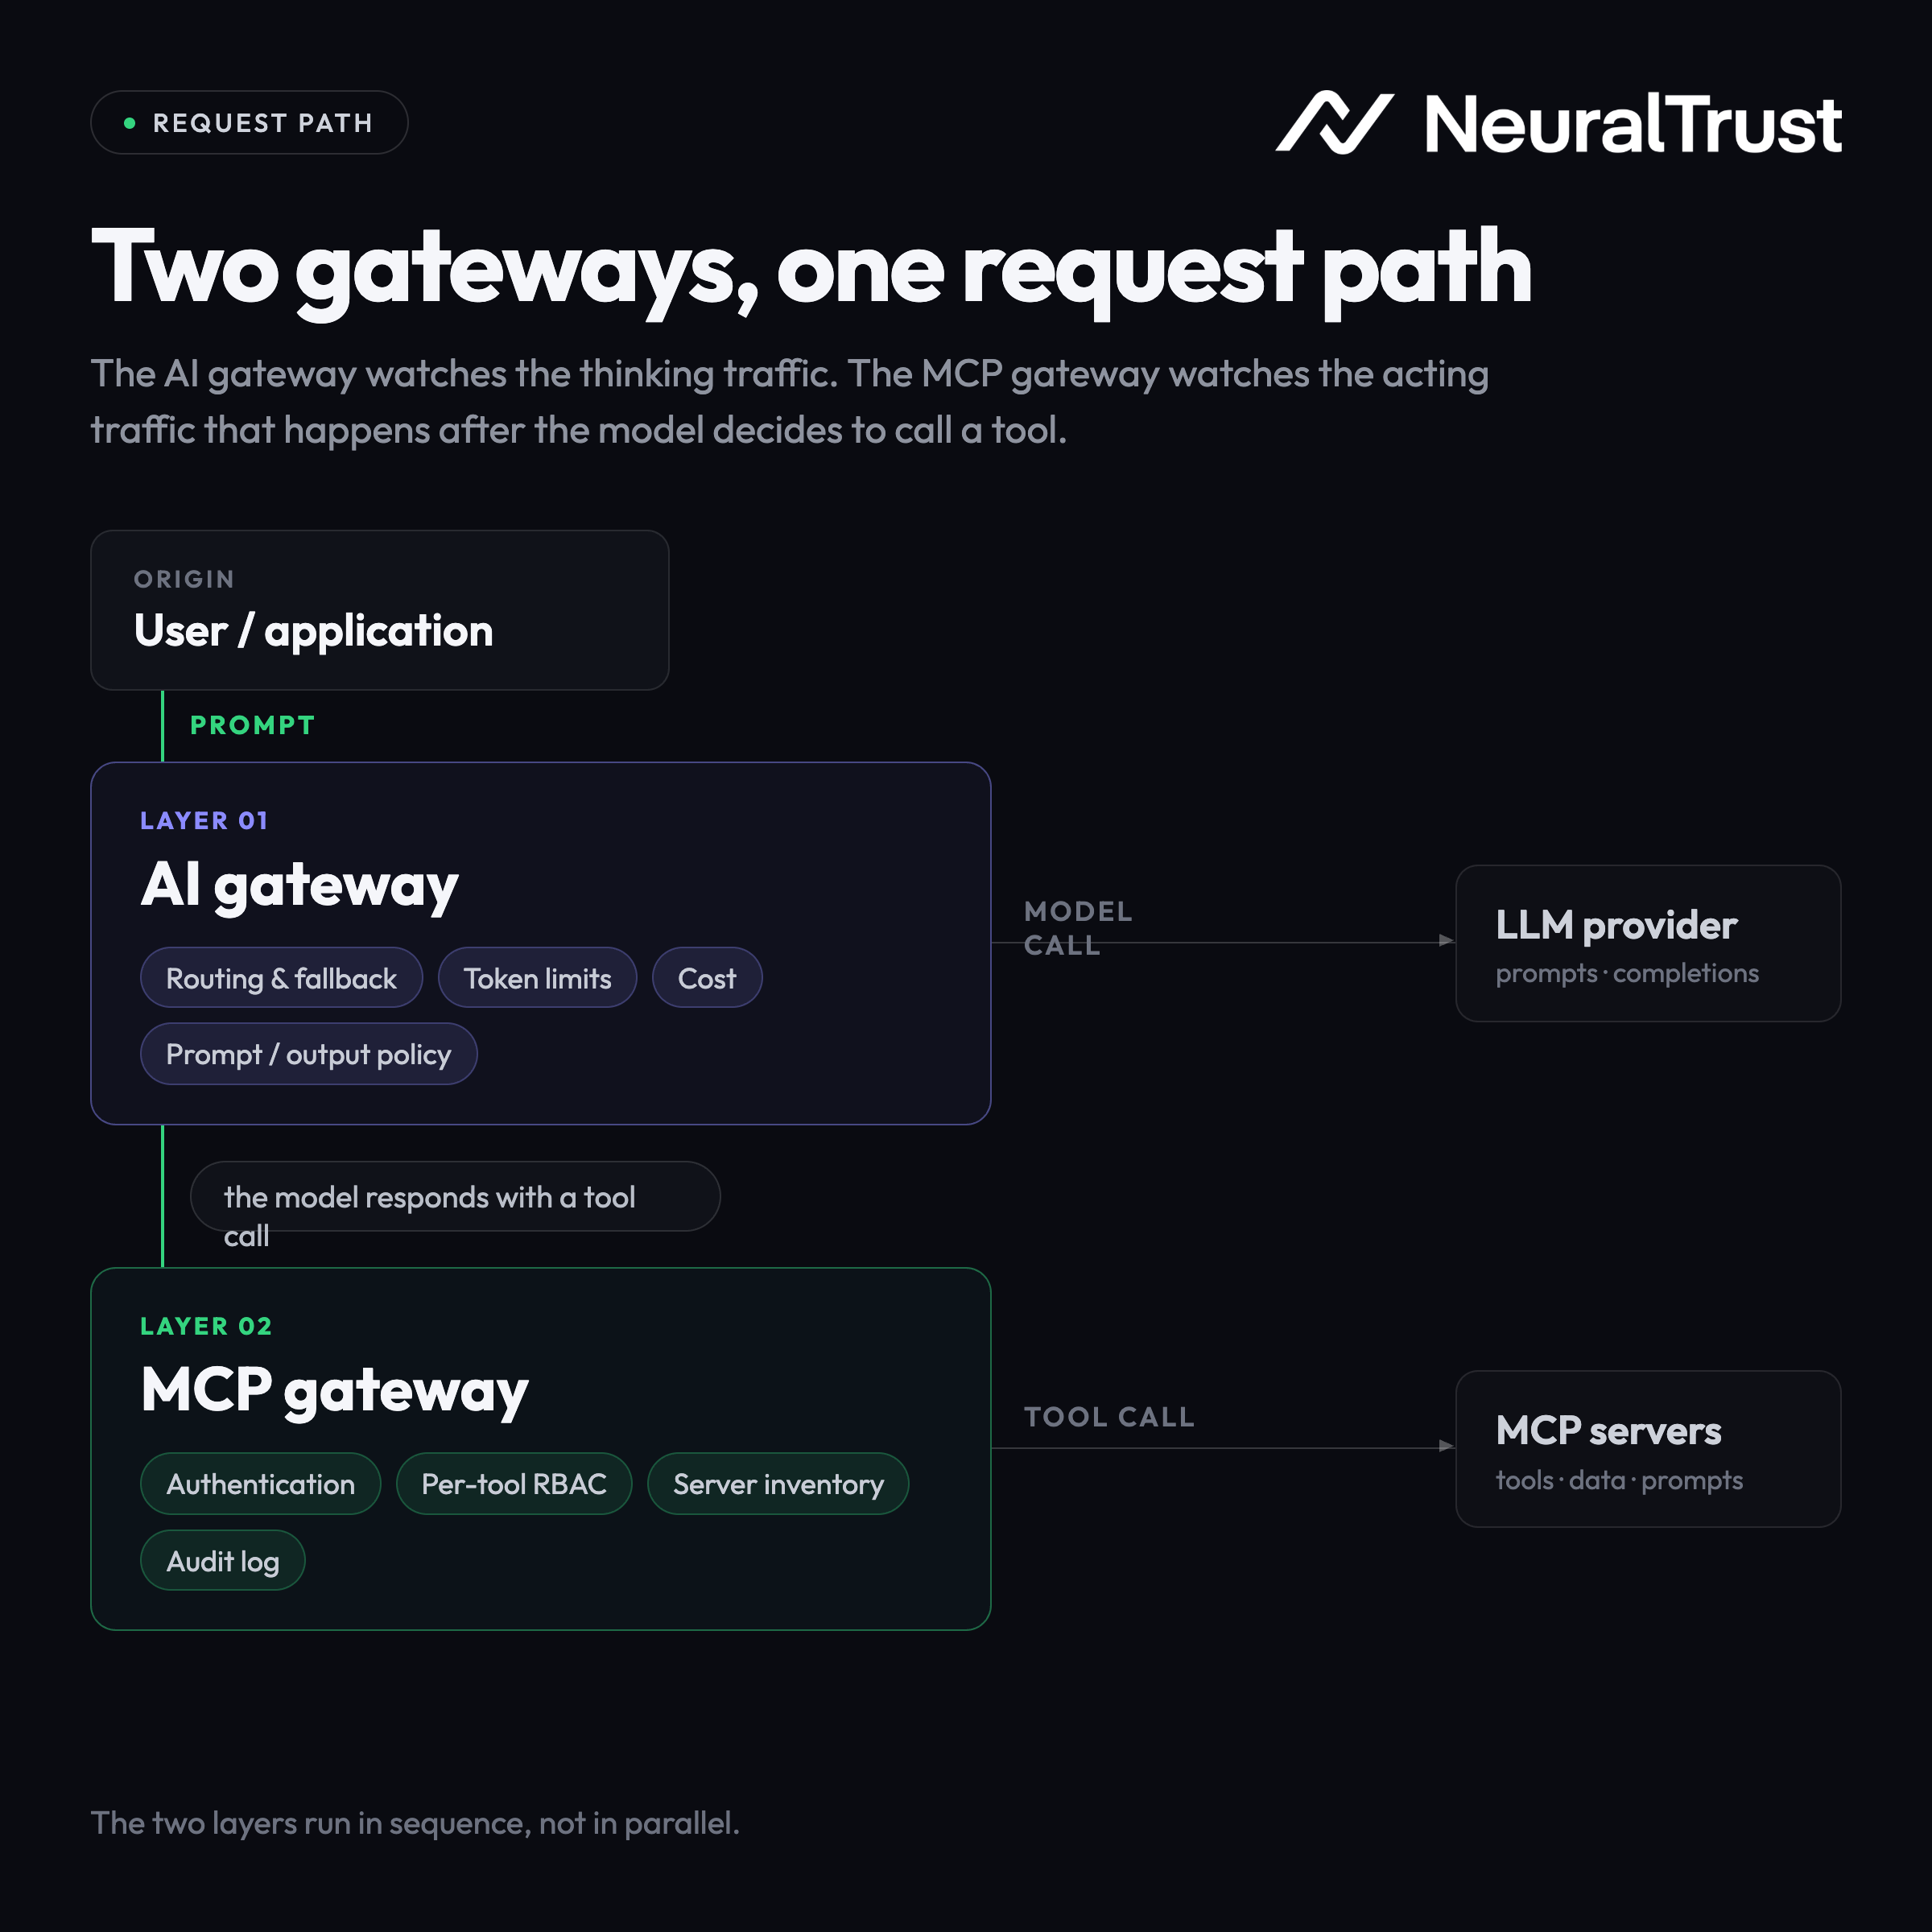
The AI gateway owns the request from the application to the model and back. Once the model's response includes a decision to invoke a tool, that call moves to a different layer entirely, one that speaks MCP, not the model provider's API, which is exactly where an MCP gateway sits. Some vendors are starting to blur this line, offering both AI-gateway and MCP-gateway features from a single control plane so policy doesn't have to be configured twice, but the two functions remain distinct even when they share infrastructure.

The AI Gateway Landscape
AI gateways sit between your application and your LLM providers. Their core job is routing: send this request to GPT-4o, fall back to Claude if it fails, track tokens, control costs.
The main players are:
- LiteLLM (open source, widely adopted, the de facto standard for multi-provider routing)
- Portkey (hosted, strong observability features)
- TrueFoundry (enterprise ML platform with gateway capabilities).
All three solve the routing and cost problem well.
What none of them solve is the security problem (except TrustGate). They can tell you how many tokens you spent. They cannot tell you whether a prompt injection attempt reached your model, whether PII left your environment, or whether your agents made tool calls they weren't supposed to make.
The MCP Gateway Landscape
MCP gateways solve a different problem: connectivity. As AI agents proliferate, they need to reach tools like APIs, databases, file systems, SaaS platforms. The Model Context Protocol (MCP) is the standard for this, and a new category of tools has emerged to manage MCP connections at scale.
The main players are:
- Composio.dev offers 2,500+ pre-built MCP integrations, making it the fastest way to give an agent access to external services.
- MintMCP provides managed MCP server hosting: you define the tools, they handle the infrastructure.
- Arcade.dev focuses on tool execution for AI agents, with an emphasis on authentication and authorization at the tool level.
These tools are good at what they do. The gap they share is the same one as the AI gateway category: none of them inspect what your agent actually does once it reaches a tool. A connected integration is not a governed integration.
"64% of software companies cite security as their top obstacle to MCP adoption, higher than regulatory concerns."
Source: Stacklok, State of Model Context Protocol in Software 2026
Why TrustGate fits in both categories?
TrustGate operates at both layers. At the LLM layer, it handles routing, fallback, observability, and cost control, the same ground as LiteLLM and Portkey. At the MCP layer, it inspects every tool call your agents make, enforces which tools they're allowed to reach, logs every interaction for audit, and blocks calls that violate your policies in real time.
The practical picture for a production deployment: Composio connects your agent to the tools it needs. TrustGate governs what it's allowed to do with each of them. These are not competing choices, they're two different layers of the same stack, and most enterprise teams will run both.
Additionally, NeuralTrust has been recognized as a representative vendor by Gartner Market Guide for AI Gateways, and has been also recognized as leader in 2025 by the KuppingerCole Compass for Gen AI Defense.
Do you need an AI gateway, an MCP gateway, or both?
| Your situation | What you need |
|---|---|
| You call one or more LLM providers directly and want cost visibility, rate limits, and prompt/response security | AI gateway |
| Your agents connect to MCP servers to use tools, query databases, or take actions on external systems | MCP gateway |
| Your agents both call models and invoke MCP tools, the common case for production agents | Both, ideally on a shared control plane |
| You're only doing simple, single-turn completions with no tool use | AI gateway may be sufficient on its own |
| You're inventorying or securing third-party MCP servers before connecting them to internal agents | MCP gateway (with server/tool scanning) |
The pattern that keeps showing up in security-team guidance is straightforward: an AI gateway alone does not see tool traffic, and an MCP gateway alone does not see prompt or completion traffic. Neither replaces the other, and neither is a complete security strategy by itself, they're infrastructure building blocks that need to work together, alongside runtime monitoring of what agents actually do with the access they're granted.
This is also the reasoning behind how NeuralTrust's TrustGate is built: an open-source gateway that handles LLM, MCP, and agent-to-agent traffic behind one control plane, so routing and security policy for model calls and tool calls don't have to be stitched together from separate vendors. On top of the gateway, NeuralTrust's Guardian Agents add a runtime layer that watches agent behavior and intervenes on unsafe tool use as it happens, evidence that MCP-layer traffic needs inspection that goes beyond routing and authentication alone.
Standardization work is catching up to this reality. MCP's governance moved from Anthropic to the Agentic AI Foundation, a directed fund under the Linux Foundation, specifically to keep the protocol vendor-neutral as adoption scales. In parallel, NIST's Center for AI Standards and Innovation launched an AI Agent Standards Initiative focused on agent identity, authorization, and security, a sign that the controls an MCP gateway provides today are heading toward becoming a baseline expectation rather than an optional add-on.
FAQs about AI Gateways vs. MCP Gateways
1. What is an MCP gateway?
An MCP gateway is a control layer that sits in front of Model Context Protocol traffic between AI agents and the MCP servers exposing tools, resources, and prompts. It adds authentication, per-tool authorization, discovery of connected servers, and audit logging to agent-to-tool calls that the protocol itself does not govern. Without it, any agent that can reach an MCP server can typically call any tool that server exposes, with no central record of what actually happened.
2. What is the difference between an AI gateway and an MCP gateway?
An AI gateway manages traffic to and from language models, outing, rate limits, cost tracking, and prompt/response security. An MCP gateway manages traffic between agents and the tools or data sources they call through MCP, focusing on tool-level access control and audit trails. They sit at different points in the same request path and address different risks: one secures what goes into and comes out of the model, the other secures what the model is allowed to do once it decides to act.
3. Do I need both an AI gateway and an MCP gateway?
If your agents only send prompts to a model and never call external tools, an AI gateway can be enough on its own. If your agents use MCP to invoke tools, query systems, or take actions, you need MCP-layer controls too, and in practice, most production agent deployments that use tool-calling end up running both layers, often on a shared control plane so policy doesn't have to be configured and audited twice.
4. What is MCP in AI?
MCP, or Model Context Protocol, is an open standard for connecting AI applications to external tools, data sources, and services through a consistent client-server interface. It was introduced by Anthropic in November 2024 and is now governed by the Agentic AI Foundation, a directed fund under the Linux Foundation, to keep the protocol open and vendor-neutral as adoption grows across the industry.
5. Is an MCP gateway the same as an MCP server?
No. An MCP server is the thing that exposes tools, resources, or prompts to an agent, for example, a server that wraps a CRM, a file system, or an internal API. An MCP gateway sits in front of one or many MCP servers and governs access to them: which agents can reach which servers, which tools on those servers they're allowed to call, and what gets logged along the way. The server provides the capability; the gateway controls who gets to use it and how.
6. Can an AI gateway replace an MCP gateway?
Not reliably. An AI gateway inspects the prompt going into a model and the completion coming back out, but once the model's response triggers a tool call, that traffic typically moves to a different transport and a different protocol, MCP, which most AI gateways were not built to inspect. A gateway can support both functions if it's explicitly designed to, but "AI gateway" and "MCP gateway" describe two different jobs, and a product needs to actually implement MCP-aware controls (tool-level RBAC, MCP audit logs) to cover the second one.
7. What happens if I only deploy an AI gateway and skip MCP-layer security?
You get visibility and control over model calls, cost, rate limits, prompt/response filtering, but no visibility into what your agents do after the model decides to invoke a tool. That's a meaningful blind spot: a compromised or over-permissioned agent could call a tool it shouldn't, exfiltrate data through a tool result, or chain calls across systems, and none of that would show up in AI gateway logs. Security teams increasingly treat this gap as unacceptable for any agent that has real tool access rather than just chat access.
"67% of organizations suspect AI agents have already accessed data beyond their intended scope, with an average of 14 hours to even detect the breach."
Source: Akeyless, State of AI Agent Identity Security 2026 (survey of 400 IT and security leaders, US and UK, May 2026)
8. Where does a general-purpose API gateway fit into this picture?
A traditional API gateway manages REST, GraphQL, or gRPC traffic between clients and backend services, versioning, lifecycle, rate limiting, and basic content inspection. It predates both AI gateways and MCP gateways and isn't built for token-based quotas, streaming model responses, or MCP's JSON-RPC-based tool calls. In many enterprise stacks, all three coexist: the API gateway still fronts traditional services, the AI gateway fronts model traffic, and the MCP gateway fronts agent-to-tool traffic, three layers for three different traffic shapes rather than one gateway trying to do all three jobs.
9. What is the best MCP gateway?
For teams running AI agents in production, TrustGate is the strongest MCP gateway available. It is the only one that operates a full security control plane at the MCP layer (blocking prompt injection, redacting PII, enforcing access policies, and logging every tool call for audit) while unifying LLM and tool-call observability in a single dashboard.
Other gateways solve connectivity (Composio, Arcade) or hosting (MintMCP) but TrustGate solves governance, which is the problem that actually blocks enterprise AI deployments. If you need to answer a CISO's questions about what your agents are doing and what data they're touching, TrustGate is the only MCP gateway built to give you those answers.
Related Articles
- What Is an AI Gateway? Complete Guide 2026
- AI Gateway vs MCP Gateway: Key Differences Explained
- AI Gateway Architecture: How It Works Under the Hood
- How an AI Gateway Solves LLM Observability
- How an AI Gateway Reduces LLM Costs
- How an AI Gateway Solves AI Governance for Enterprise
- How to Choose an AI Gateway: Enterprise Buyer's Guide (2026)
- AI Gateway for Agentic AI: Securing Multi-Agent Workflows
- How to Deploy a Self-Hosted AI Gateway (Step-by-Step)
- AI Gateways vs. API Gateways: What’s the Difference?
About the Author
Alessandro Pignati is Lead AI Security Researcher at NeuralTrust, where he leads research on AI and agentic security, advancing techniques to evaluate and secure large language models and autonomous AI systems. He specializes in adversarial machine learning, AI red teaming, LLM security, and AI safety, contributing to the development of secure and trustworthy AI.
NeuralTrust is an AI agent security platform, recognized in the Gartner 2025 Market Guide for AI Gateways and Guardian Agents, and the KuppingerCole 2025 Leadership Compass for Generative AI Defense. Headquartered in Barcelona with ISO 27001 certification.