Last updated: September 2026
With dozens of options on the market, how do you identify the best AI gateway for your enterprise?
The best AI gateway for enterprise in 2026 is the one that enforces your security and compliance requirements across every AI model in your stack (regardless of provider) with the observability needed to run generative AI responsibly in production.
This guide gives you a structured framework for making that decision, covering the seven criteria that separate enterprise-ready AI gateways from point solutions that will not scale.
TL;DR - Key Takeaways
- An AI gateway (also called an LLM gateway) is the infrastructure layer that sits between your applications and your LLM providers enforcing policies, routing traffic, logging interactions, and protecting against prompt injection and data leakage.
- In 2026, the best enterprise AI gateways also handle MCP Gateway traffic and Agent Gateway session management, the capabilities needed for agentic AI deployments.
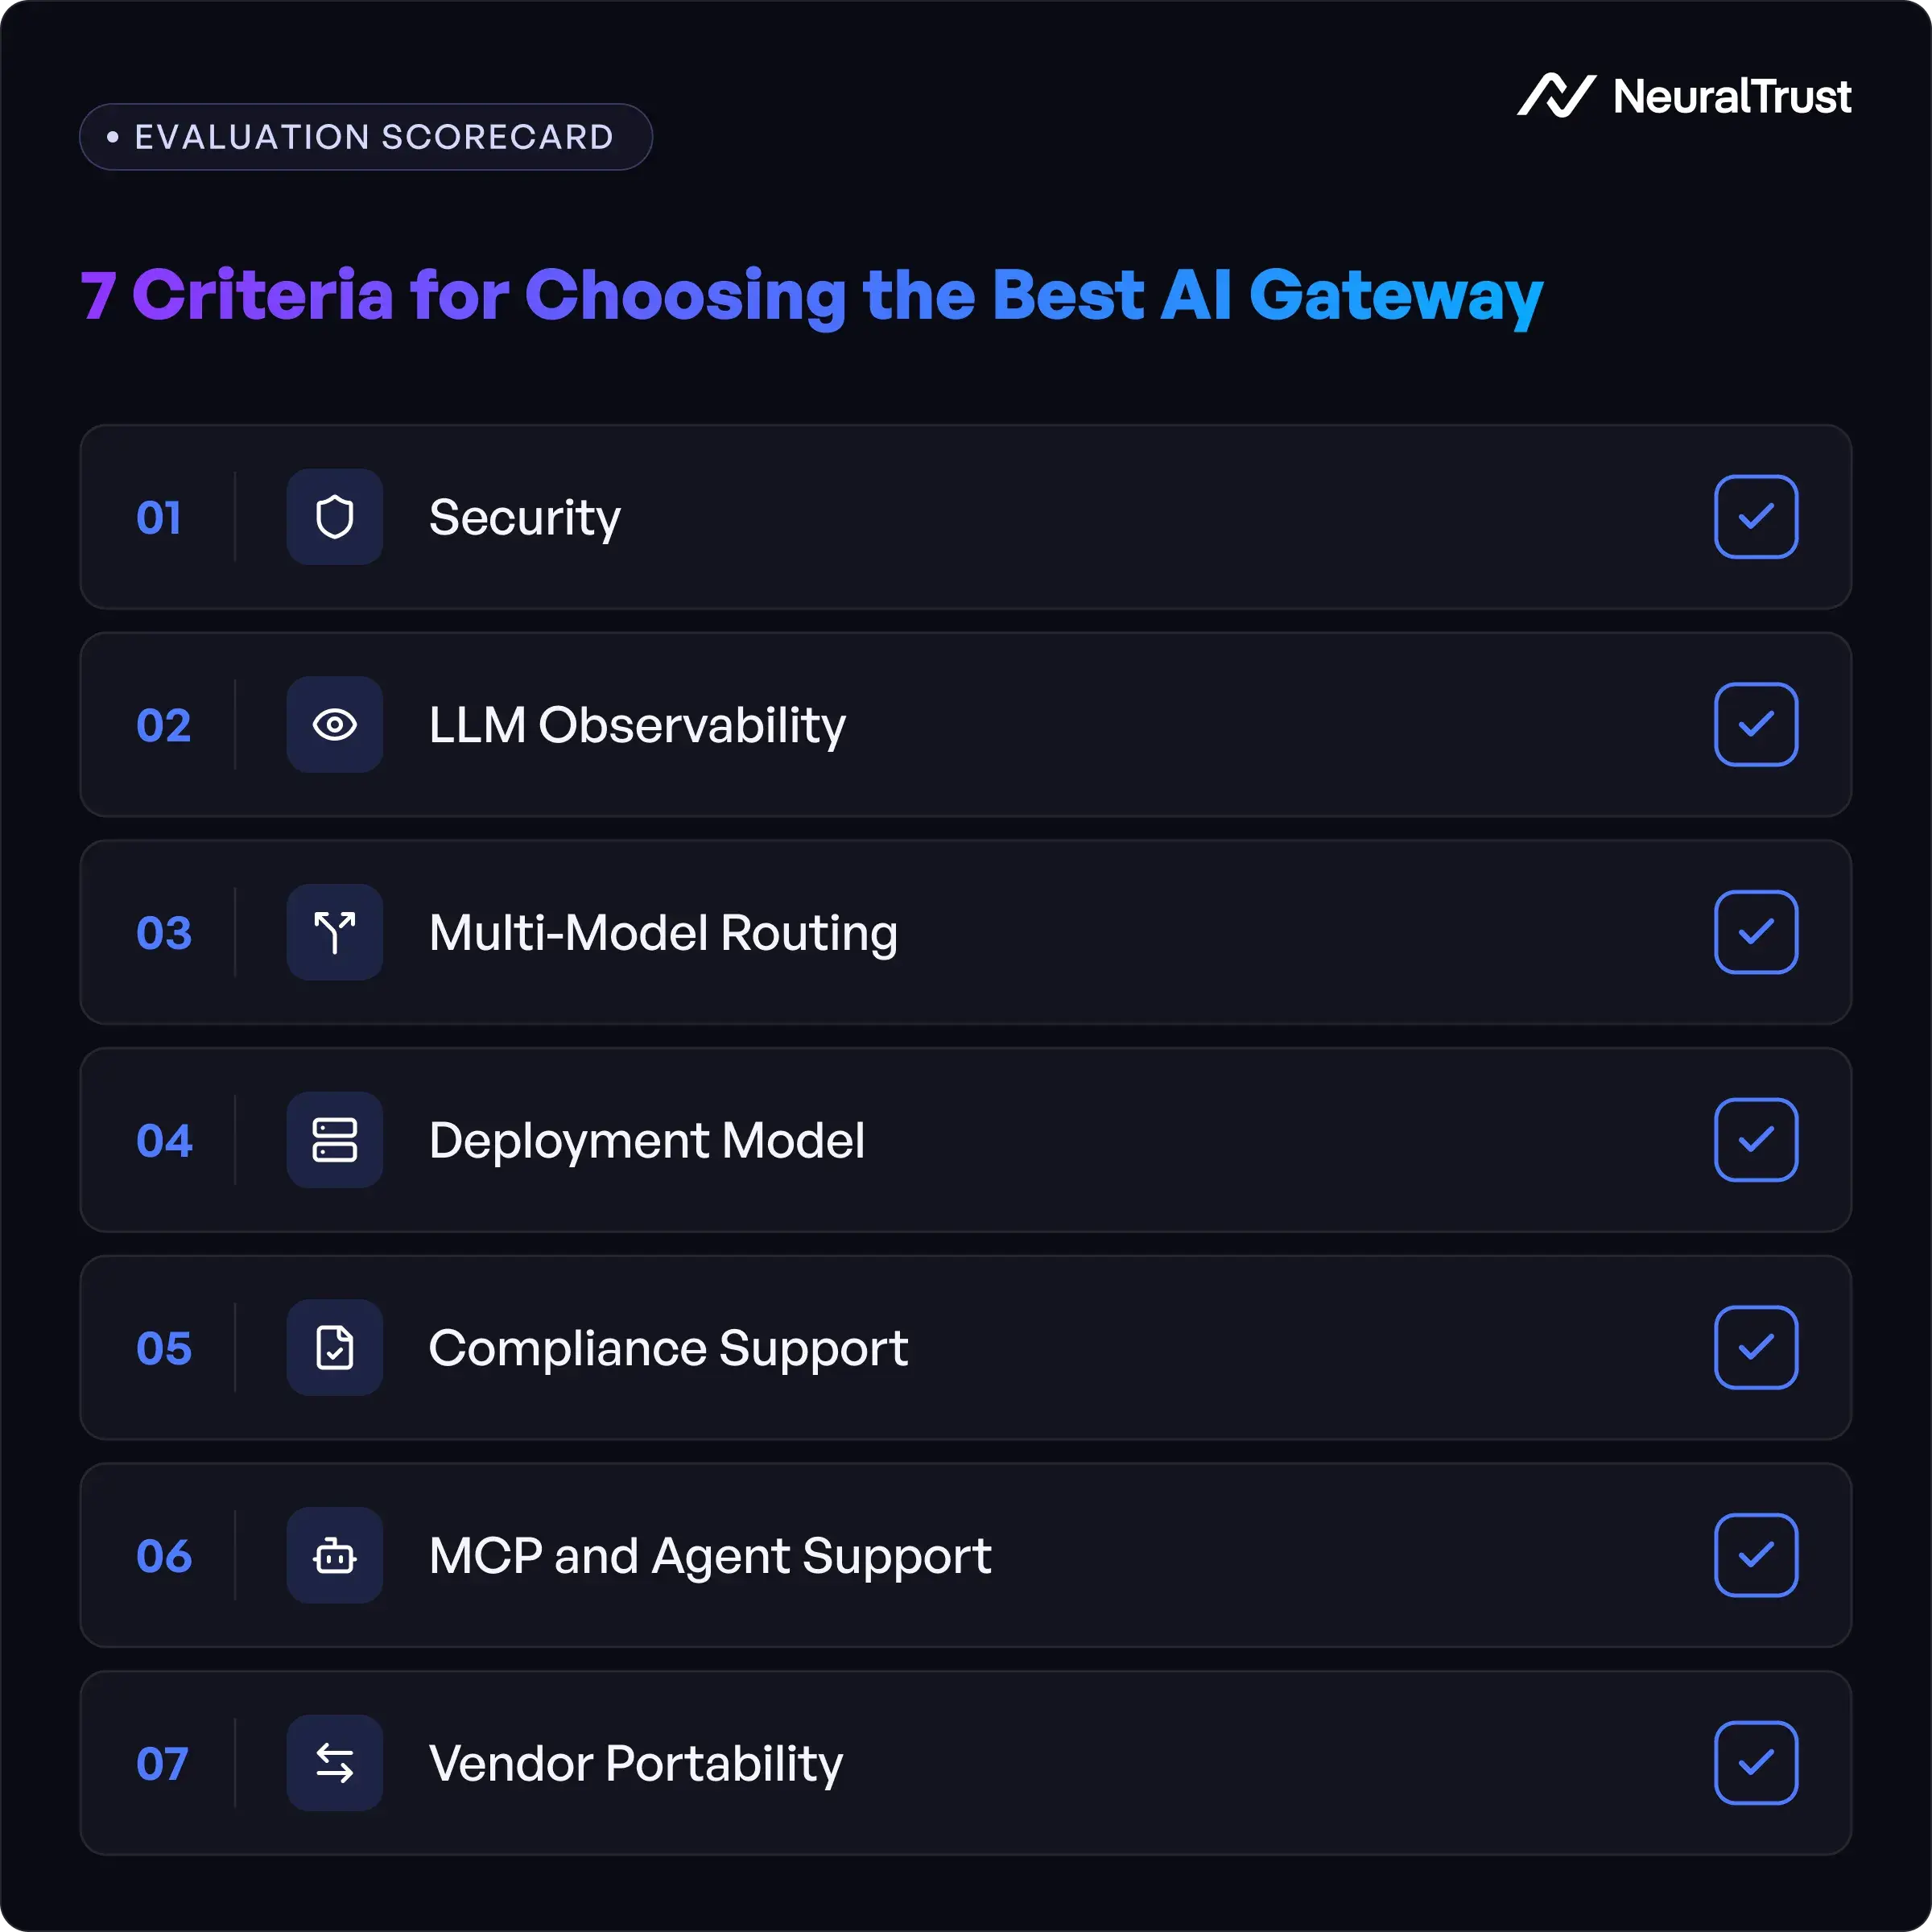
- The best AI gateway for enterprise is evaluated on seven criteria: security, LLM observability, multi-model routing, deployment model, compliance support, MCP and agent support, and vendor portability.
- Enterprises in regulated industries must treat gateway-level controls (prompt inspection, structured logging, data residency enforcement) as compliance requirements, not optional features.
- NeuralTrust TrustGate is an Enterprise AI gateway that meets all seven criteria, available in cloud, self-hosted, and hybrid deployment.
Introduction
With dozens of options on the market, how do you identify the best AI gateway for your enterprise? The best AI gateway for enterprise in 2026 is not the one with the longest feature list, it is the one that enforces your security and compliance requirements across every generative AI model in your estate, with the observability and auditability your organisation needs to deploy AI responsibly at scale.
The AI gateway market has matured fast. What began as a thin proxy layer between enterprise applications and the OpenAI API has evolved into a full infrastructure category, covering multi-model routing, prompt injection defence, structured LLM observability, EU AI Act compliance controls, and increasingly the orchestration and monitoring of autonomous AI agents.
The stakes have risen accordingly. Enterprises integrating Claude, GPT, Gemini, Mistral, and open-source models into production workflows now handle regulated data, critical business processes, and agentic workloads that carry real operational and legal risk.
Choosing the wrong AI gateway means either under-building (using a tool that cannot meet your security and compliance requirements) or over-committing to a proprietary platform that locks you into one provider and one architecture. This guide gives you the framework to get it right.
For a foundational overview of what an AI gateway does and how it fits into your AI infrastructure, see: What Is an AI Gateway?
AI Gateway, LLM Gateway, MCP Gateway, Agent Gateway: What Is the Difference?
Before choosing an enterprise AI gateway, it helps to understand how the terminology has evolved, because vendor positioning has not always kept pace with how these systems actually work in production.
An AI gateway (or LLM gateway) is the infrastructure layer that sits between enterprise applications and LLM providers. It handles routing, authentication, rate limiting, logging, prompt inspection, and policy enforcement. The terms AI gateway and LLM gateway are largely interchangeable, with "AI gateway" increasingly preferred as these systems expand beyond language model traffic to cover multimodal and agentic workloads.
An MCP Gateway extends this to the Model Context Protocol, the emerging standard for connecting AI agents to tools, databases, and APIs. As organisations deploy agentic AI systems, the gateway must also inspect and control MCP traffic: which tools an agent can access, what data it can retrieve, and what actions it can execute on behalf of the user.
An Agent Gateway is the most expansive framing: a gateway that manages the full lifecycle of an AI agent session, including multi-step reasoning, tool calls, external API access, and long-running autonomous workflows that may run for hours without human interaction.
In practice, the best enterprise AI gateways in 2026 address all three: handling LLM API traffic, MCP connections, and agent session management within a unified control plane. For a detailed comparison, see AI Gateway vs MCP Gateway.
| Gateway type | Primary function | When you need it |
|---|---|---|
| AI gateway / LLM gateway | Route and secure LLM API traffic | All enterprise AI deployments |
| MCP Gateway | Inspect and control MCP tool connections | AI agents with tool access |
| Agent Gateway | Manage full autonomous agent sessions | Long-running agentic workflows |
| Enterprise AI gateway | All of the above, with compliance and observability | Regulated industries and multi-model estates |
7 Criteria for Choosing the Best AI Gateway
1. Security and Prompt Injection Defence
According to OWASP, prompt injection is the number one vulnerability in LLM-powered applications. It is the attack class in which adversarial content embedded in user messages, retrieved documents, or API responses overrides the system's intended behaviour, bypassing safety rules, extracting sensitive data, or redirecting agent actions.
An enterprise AI gateway must inspect both the input and output of every model interaction independently of the model's own safeguards. Key capabilities to evaluate:
- Gateway-layer prompt inspection before the request reaches the model, with configurable rulesets mapped to OWASP LLM Top 10 attack vectors
- Output filtering for sensitive data, PII, and policy violations before responses reach end users or downstream systems
- Indirect prompt injection protection for agentic workloads, where adversarial content embedded in retrieved documents or tool responses can redirect agent behaviour across multiple calls
- Session-level threat detection for autonomous agents, where a single compromised interaction can escalate across a multi-hour session before the damage is visible
What good looks like: Native prompt inspection and output filtering at the gateway layer, configurable OWASP LLM Top 10 rulesets, and session-level anomaly detection for agentic workflows.
Red flag: A gateway that relies on model-level safeguards alone, with no independent input/output inspection layer.
For a full breakdown of AI gateway security architecture, see AI Gateway Security.
2. LLM Observability and Audit Logging
You cannot manage what you cannot see. In regulated industries, structured LLM observability is a compliance requirement. The NCSC's August 2026 guidance on agentic AI explicitly identifies chain-of-thought logging and sandbox event recording as foundational security operations requirements for autonomous AI systems.
The IBM Cost of a Data Breach Report 2024 found that organisations with mature security observability identified and contained breaches 108 days faster on average than those without, a gap that applies directly to AI systems in production. An enterprise AI gateway must log every model interaction with the structure needed for both real-time monitoring and regulatory audit:
- Structured per-interaction logs: user identity, timestamp, model used, prompt content classified by data sensitivity, completion content, token usage, latency, and policy violations triggered
- Trace IDs that correlate a single user request across multiple model calls, essential for auditing multi-step agentic workflows
- SIEM integration so that AI interaction logs feed into existing security monitoring infrastructure, without requiring custom parsers
- Tamper-evident log storage to ensure audit trails cannot be modified or deleted after the fact
What good looks like: Full per-interaction logging with configurable retention, trace correlation across multi-model calls, and export in standard SIEM-compatible formats.
Red flag: Basic HTTP request/response logs with no structured data, no trace IDs, and no integration path to your existing security stack.
For a detailed guide to LLM observability requirements and implementation, see AI Gateway and LLM Observability.
3. Multi-Model Routing and Cost Optimisation
Enterprise AI deployments are rarely single-model. Most organisations run Claude, GPT, Gemini, and open-source models simultaneously, routing different tasks to different models based on capability requirements, cost, latency, and data classification. An enterprise AI gateway must route this traffic intelligently.
Key routing capabilities to evaluate:
- Model-agnostic routing: The gateway must support all major commercial providers and open-source models with equal fidelity, without preferential treatment for any single vendor
- Cost-aware routing: Route requests to the most cost-effective model capable of completing the task, applying semantic caching to eliminate redundant calls across similar requests
- Latency-aware routing: Route time-sensitive requests to the fastest available model, with automatic fallback when primary models are degraded or at capacity
- Semantic caching: Cache the responses to semantically similar requests (not just identical ones) to reduce token spend significantly on high-volume workloads
What good looks like: Configurable routing rules by model, task type, cost ceiling, latency threshold, and data classification, with built-in semantic caching and provider fallback logic.
Red flag: A gateway tied to a single LLM provider, or one where routing logic must be implemented and maintained in application code.
For a practical guide to reducing LLM spend through gateway-level cost optimisation, see AI Gateway and LLM Cost Optimisation.
4. Deployment Model: Cloud, Self-Hosted, and Hybrid
Deployment model is a critical and consistently under-evaluated criterion. It directly determines your data sovereignty posture, your compliance obligations, and your ability to meet the data residency requirements of UK GDPR, the EU AI Act, and sector-specific frameworks.
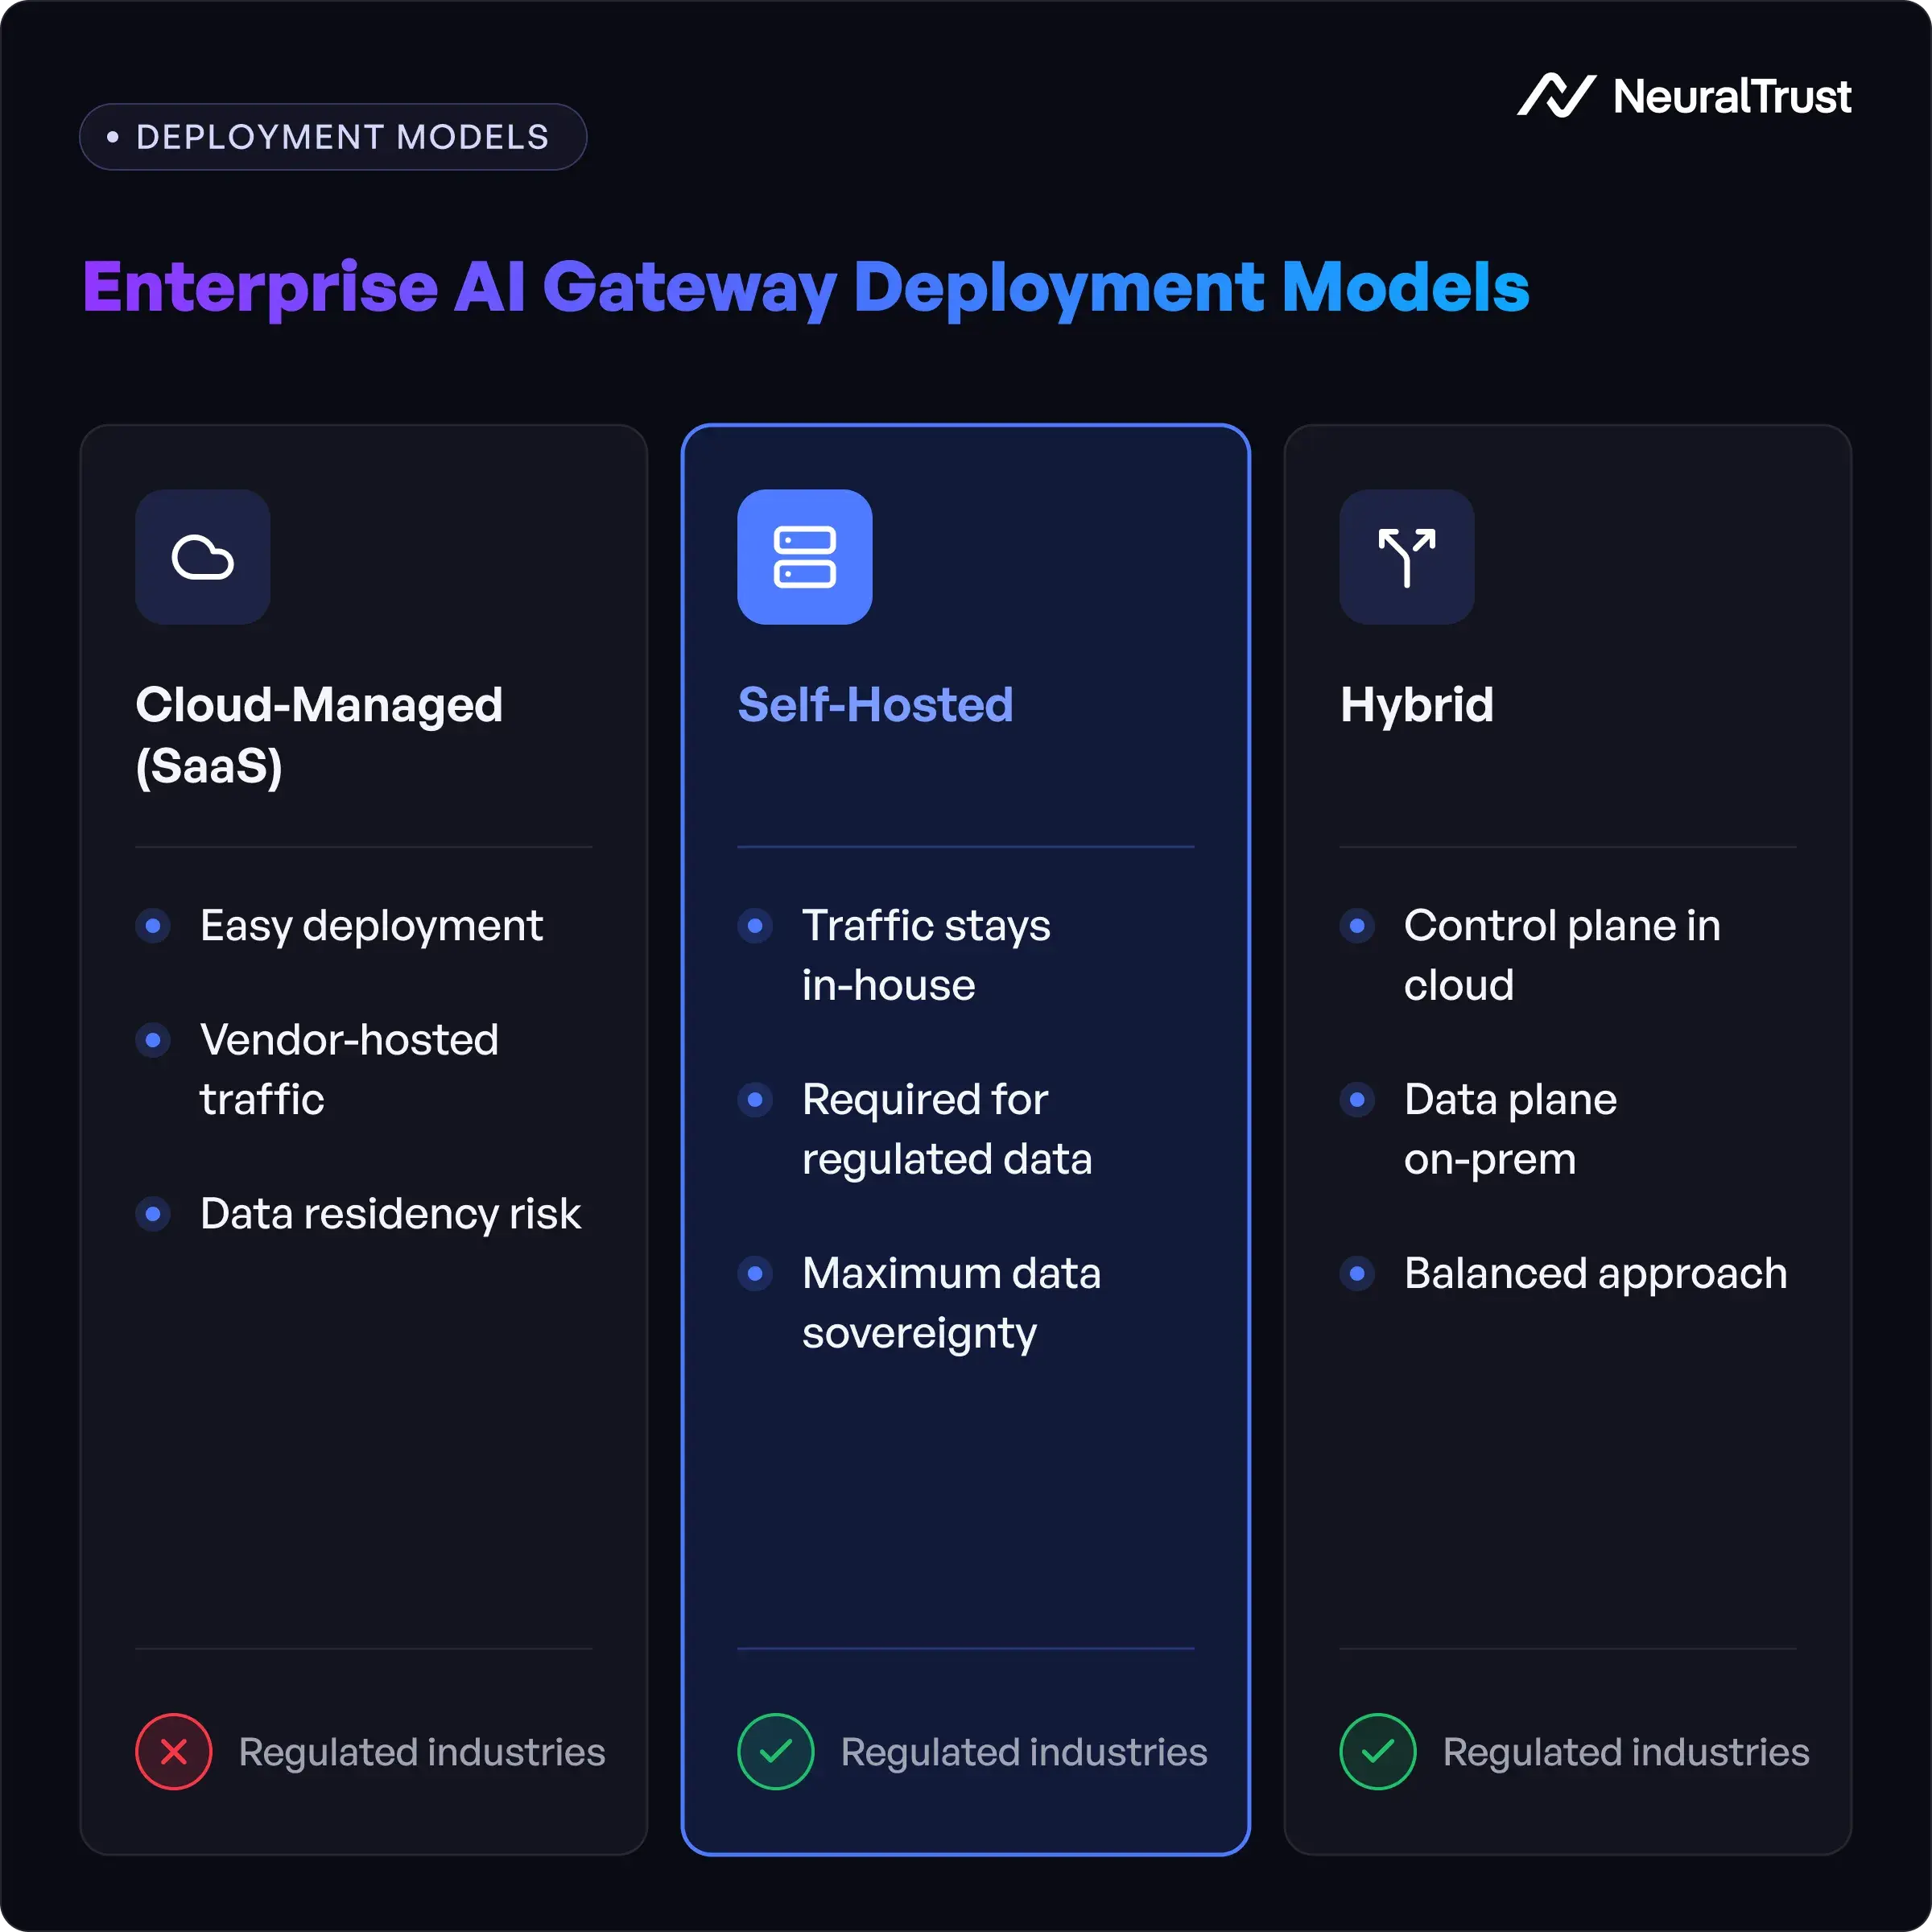
The three deployment models available from enterprise AI gateway vendors are:
Cloud-managed (SaaS): The gateway is hosted and managed by the vendor. Easiest to deploy and operate, but all AI traffic passes through the vendor's infrastructure. For organisations handling regulated data like patient records, financial data, or customer PII, this creates data residency and legal jurisdiction risk that may be incompatible with their compliance obligations.
Self-hosted: The gateway runs inside your own infrastructure, whether on-premises or in a private cloud. All AI traffic stays within your environment. This is the deployment model required for most regulated industries under UK GDPR, the EU AI Act, and sector frameworks in financial services and healthcare.
Hybrid: A control plane managed by the vendor combined with a data plane running inside your infrastructure. Traffic inspection and policy enforcement happen within your environment; operational management and analytics are handled centrally. This model is increasingly preferred for enterprises that want operational simplicity without compromising data sovereignty.
What good looks like: A gateway available in all three deployment configurations, with clear data flow documentation for each, showing exactly where data travels and who has access to it.
Red flag: Cloud-only deployment with no self-hosted option, particularly from a vendor explicitly targeting regulated industries.
5. Compliance Support: EU AI Act, UK GDPR, SOC 2
The regulatory landscape for enterprise AI in 2026 demands that your AI gateway functions as an active compliance control, not just an infrastructure convenience. The EU AI Act is now in partial application, with obligations for deployers of high-risk AI systems. UK GDPR continues to apply to any AI system processing personal data of UK residents. SOC 2 Type II and ISO 27001 remain baseline requirements for enterprise procurement.
Evaluate your AI gateway against each framework:
- EU AI Act: Does the gateway support the technical documentation, structured logging, human oversight mechanisms, and incident reporting required for high-risk AI deployers? Does it support content watermarking for AI-generated outputs?
- UK GDPR: Does the gateway enforce data minimisation at the routing layer? Can it prevent UK personal data from leaving UK infrastructure? Can it produce a data processing record on request?
- SOC 2 Type II / ISO 27001: Is the vendor certified? Can they produce their audit report and certificate within 24 hours of a request?
What good looks like: A vendor with active SOC 2 Type II and ISO 27001 certifications, a documented data processing agreement mapped to your jurisdiction, and gateway controls mapped to EU AI Act high-risk obligations.
Red flag: A vendor that lists compliance frameworks in marketing materials but cannot produce certification evidence or a signed data processing agreement on request.
6. MCP and Agent Gateway Support
As enterprises deploy Claude, GPT, and Gemini as autonomous agents (writing and executing code, browsing the web, reading databases, and calling external APIs) the gateway's responsibilities expand significantly beyond routing LLM API calls. An enterprise AI gateway in 2026 must also handle the full surface area of agentic AI deployments:
- MCP traffic inspection: Inspect and control the tool connections that AI agents establish via the Model Context Protocol, including configurable allow/deny lists for tool access by agent identity and task type
- Session-level monitoring: Track the full lifecycle of an autonomous agent session enabling detection of scope escalation, intent drift, and unexpected tool usage across extended multi-step workflows
- Least-privilege credential scoping: Enforce that each agent operates with the minimum permissions required for its current task, with credentials unavailable beyond the agent's defined scope
- Emergency halt capability: The ability to immediately stop a running agent, revoke its active credentials, and cut its network connections, a requirement the NCSC names explicitly in its agentic AI guidance
What good looks like: Native MCP traffic inspection with configurable agent permission profiles, session-level behavioural monitoring with anomaly alerting, and a documented emergency halt procedure with sub-minute response time.
Red flag: A gateway that treats each agent API call as a stateless request, providing no session-level visibility, no MCP inspection, and no mechanism for emergency agent termination.
For a detailed comparison of AI gateway and MCP gateway architectures and capabilities, see AI Gateway vs MCP Gateway.
7. Vendor Lock-in Risk and Portability
Every enterprise AI gateway selection is also a long-term architectural commitment. The vendor landscape is consolidating rapidly. Startups are being acquired. Pricing models are changing as the category matures from infrastructure novelty to procurement commodity. Your gateway decision should be evaluated not only on what it delivers today, but on the architectural risk it creates over a three-to-five-year horizon.
Key questions to ask every vendor:
- Is the core open source? An open-source gateway eliminates infrastructure lock-in entirely. You own your deployment and your data regardless of what happens to the vendor: acquisition, pricing change, or market exit.
- Are your routing rules and policies portable? Policy configurations written in proprietary formats cannot be migrated without significant engineering rework. Standard, human-readable configuration formats are a meaningful differentiator.
- What is the documented migration path? If you needed to replace this gateway in 18 months, how long would it take and what would it cost? If a vendor cannot give you a clear answer, that is the answer.
- Does the gateway support open standards? Gateways built on OpenAPI, OAuth 2.0, and open configuration standards are easier to integrate, easier to audit, and easier to migrate.
What good looks like: An open-source core with a commercially supported enterprise edition, giving you the portability safety of open source with the SLA and support that enterprise production deployments require.
Red flag: A fully proprietary gateway with vendor-specific configuration formats, no documented migration path, no open-source components, and a licensing model that penalises volume growth.
AI Gateway Evaluation Scorecard
Use this scorecard during vendor shortlisting. Assess each candidate against each criterion, flag red flags, and weight criteria by your organisation's specific compliance and operational requirements.
| Criterion | What good looks like | Red flags |
|---|---|---|
| Security | Gateway-layer prompt inspection, output filtering, OWASP LLM Top 10 coverage | Relies on model safeguards only, no independent inspection |
| LLM Observability | Structured per-interaction logs, trace IDs, SIEM integration, tamper-evident storage | Basic HTTP logs, no trace correlation, no SIEM export |
| Multi-model routing | Model-agnostic, cost-aware, latency-aware routing, semantic caching | Single-provider only, routing logic in application code |
| Deployment model | Cloud, self-hosted, and hybrid all available | Cloud-only, no self-hosted option for regulated data |
| Compliance support | SOC 2 Type II, ISO 27001, EU AI Act controls, data residency enforcement | Marketing claims only, no certifications producible on request |
| MCP and agent support | MCP inspection, session monitoring, credential scoping, emergency halt | Stateless request routing, no session-level visibility |
| Vendor portability | Open-source core, portable policy formats, documented migration path | Proprietary API, no open-source, no migration documentation |
How to Evaluate an Enterprise AI Gateway: Step-by-Step
-
Define your AI use cases first. Catalogue every AI application your organisation runs or plans to deploy: API integrations, chat interfaces, coding agents, document processing, customer-facing tools. Classify each by data sensitivity and regulatory obligation.
-
Map your compliance obligations. Identify which frameworks apply to each use case: EU AI Act, UK GDPR, HIPAA, PCI DSS, SOC 2, ISO 27001. The strictest obligation in your portfolio sets the baseline requirements for the gateway.
-
Filter by deployment model before evaluating features. Eliminate vendors that cannot match your deployment model requirement before reviewing features. A cloud-only gateway cannot meet a self-hosted requirement regardless of what else it offers.
-
Run a prompt injection test. Any vendor worth evaluating will support this. Send a standard set of OWASP LLM Top 10 prompt injection payloads through the candidate gateway and verify they are detected and blocked before reaching the model.
-
Evaluate the observability output. Send 10 test interactions and examine the resulting logs. Verify that you can identify the user, the model, the full prompt and response, the token count, the latency, and any triggered policy rules in a structured format your SIEM can ingest.
-
Test multi-model routing. Configure the gateway to route identical requests to two different models and verify the routing logic performs as configured. Test fallback behaviour when a primary model is unavailable or returns an error.
-
Request compliance evidence. Ask every shortlisted vendor for their SOC 2 Type II report, ISO 27001 certificate, and data processing agreement. Vendors with real certifications provide these within 24 hours. Vendors without them will stall.
-
Test MCP and agent capabilities. If you are deploying or planning AI agents, test the gateway's MCP traffic inspection by establishing a test agent with a controlled toolset and verifying that the gateway enforces the allow list correctly and logs all tool calls.
-
Assess the migration path. Ask each vendor to walk you through what a migration away from their platform would involve technically and contractually. Open-source vendors with portable configuration give a clear, specific answer. Proprietary vendors typically do not.
-
Model total cost of ownership. Include token costs saved through semantic caching, engineering time saved through managed infrastructure, and the cost of compliance tooling you will not need to build and maintain separately.
For a detailed guide to AI gateway architecture patterns, see AI Gateway Architecture. For the governance controls your gateway must support for enterprise AI programmes, see AI Gateway and Enterprise Governance.
Start Securing Your AI Infrastructure with NeuralTrust
NeuralTrust TrustGate is an enterprise AI gateway purpose-built for the requirements in this guide. It delivers native gateway-layer prompt inspection and output filtering, structured LLM observability with SIEM integration, model-agnostic multi-model routing with semantic caching, self-hosted and hybrid deployment options, EU AI Act and UK GDPR compliance controls, and full MCP traffic inspection with agentic session monitoring.
NeuralTrust was named a Pioneer in the Gartner Emerging Market Quadrant for AI Application Security 2026, and is recognised across four Gartner Hype Cycle reports in the same year. Headquartered in Barcelona, with offices in London and New York. ISO 27001 certified.
FAQs about choosing the best AI Gateway
1. What is the difference between an AI gateway and a traditional API gateway?
A traditional API gateway manages HTTP traffic between applications and backend services handling authentication, rate limiting, load balancing, and routing. An AI gateway extends this with capabilities specific to LLM traffic: prompt inspection for security, output filtering for data loss prevention, token-level cost optimisation, semantic caching, model-agnostic routing, and structured observability for AI-specific audit requirements. The distinction matters because LLM interactions carry unique risks (prompt injection, data extraction, model hallucination, and agentic scope escalation) that traditional API gateways are not architected to address.
2. Do I need an AI gateway if I am only using one LLM provider?
Yes. Even with a single provider, an AI gateway provides security, observability, and governance capabilities that the model API itself does not include. Prompt inspection, output filtering, structured logging for compliance, and policy enforcement are gateway-layer controls, they operate regardless of which model traffic routes to. As your AI deployment grows, the gateway also gives you the flexibility to add providers, route appropriate tasks to more cost-effective models, and apply consistent policies across a growing estate without re-engineering each individual application.
3. What is an LLM gateway and how does it differ from an AI gateway?
The terms are largely interchangeable. "LLM gateway" was the earlier framing, used when gateways primarily routed large language model API traffic. "AI gateway" is the current preferred term as these systems expand to cover multimodal models, agentic workflows, and MCP connections. An enterprise AI gateway in 2026 handles LLM API traffic, MCP gateway functions, and agent session management in a unified control plane.
4. What is an MCP Gateway and when do I need one?
An MCP Gateway inspects and controls traffic over the Model Context Protocol, the emerging standard for connecting AI agents to external tools, databases, and APIs. You need MCP Gateway capability as soon as you deploy AI agents that make tool calls: browsing the web, querying databases, calling external APIs, or executing code. Without MCP-level inspection, the gateway sees only the LLM API traffic and cannot control what tools the agent accesses or what actions it takes in your environment. The NCSC's agentic AI guidance explicitly names tool access controls as a foundational security requirement for autonomous AI systems.
5. How does an enterprise AI gateway support EU AI Act compliance?
An enterprise AI gateway supports EU AI Act compliance in several ways. It provides the structured logging required for technical documentation and incident reporting obligations on deployers of high-risk AI systems. It enforces the human oversight and intervention controls required under the regulation. It supports data residency enforcement through self-hosted or hybrid deployment, ensuring regulated personal data is processed only within approved jurisdictions. Some enterprise AI gateways also support AI content watermarking, a requirement for providers of general-purpose AI systems under the Act. Compliance ultimately requires controls across the full AI stack, but the gateway is the primary enforcement and audit point.
About the Author
Roger Howroyd is Head of Global SEO and AI at NeuralTrust, where he leads the company's search strategy across SEO, AEO, GEO, and LLM optimisation. He specialises in AI-powered search, content strategy, and SEM. Connect on LinkedIn.
NeuralTrust is the leading platform for securing and scaling AI agents. Named a Pioneer in the Gartner Emerging Market Quadrant for AI Application Security 2026 and recognised across four Gartner Hype Cycle reports in the same year. Headquartered in Barcelona with offices in London (167 Great Portland Street) and New York. ISO 27001 certified.