Last updated: September 2026
What should a UK CISO prioritise when building an enterprise AI security programme?
AI security platforms UK enterprises need must address a set of threats that traditional security tooling was never designed to catch: prompt injection, agent misuse, model data exfiltration, and intent drift in autonomous AI systems. For UK CISOs, the challenge it is more than just technical: it is regulatory, operational, and strategic simultaneously. This guide covers all three. Let's dive in.
TL;DR - Key Takeaways
- AI introduces a new attack surface that existing security tools do not cover. Firewalls, endpoint detection, and SIEM platforms see network and endpoint activity. They do not see what an LLM is doing with a prompt, what an AI agent is calling, or what sensitive data a model completion is returning.
- UK CISOs face regulatory pressure from three directions simultaneously: NCSC AI security guidance, UK GDPR data processing obligations, and EU AI Act requirements that continue to apply to UK organisations serving EU customers or deploying EU-origin AI systems.
- AI security platforms UK enterprises evaluate should cover four capabilities: runtime defence, enterprise AI gateway controls, LLM observability, and AI governance policy enforcement: from a single integrated deployment, not a stack of disconnected point tools.
- According to Gartner, by 2028, loss of control over AI agents will be the top concern for 40% of Fortune 1000 organisations. The window for establishing enterprise AI security controls before AI deployments scale beyond manageable risk is shrinking.
- OWASP identifies prompt injection as the leading vulnerability in LLM-powered applications, and it is a threat that cannot be addressed at the network or endpoint layer. It requires controls at the AI layer itself.
- NeuralTrust's TrustGate is an open-source AI gateway that UK security teams can deploy free in their own infrastructure: enforcing policy, generating audit trails, and providing LLM observability across the entire AI estate with no application-level changes required.
The AI Security Threat Landscape Every UK CISO Must Navigate
Enterprise AI adoption in the UK has accelerated faster than the security frameworks designed to govern it. Organisations across financial services, healthcare, government, and professional services are deploying large language models, AI agents, and generative AI tools in customer-facing, internal, and operational contexts. Most of them have done so without a security layer designed for AI traffic.
The threat surface that AI introduces is different from anything traditional security programmes were built to handle. It is not a network vulnerability. It is not a misconfigured server. It is a semantic attack surface: the model itself can be manipulated through the content of what is sent to it, and the output it produces can carry risks that no endpoint tool or packet inspector can detect.
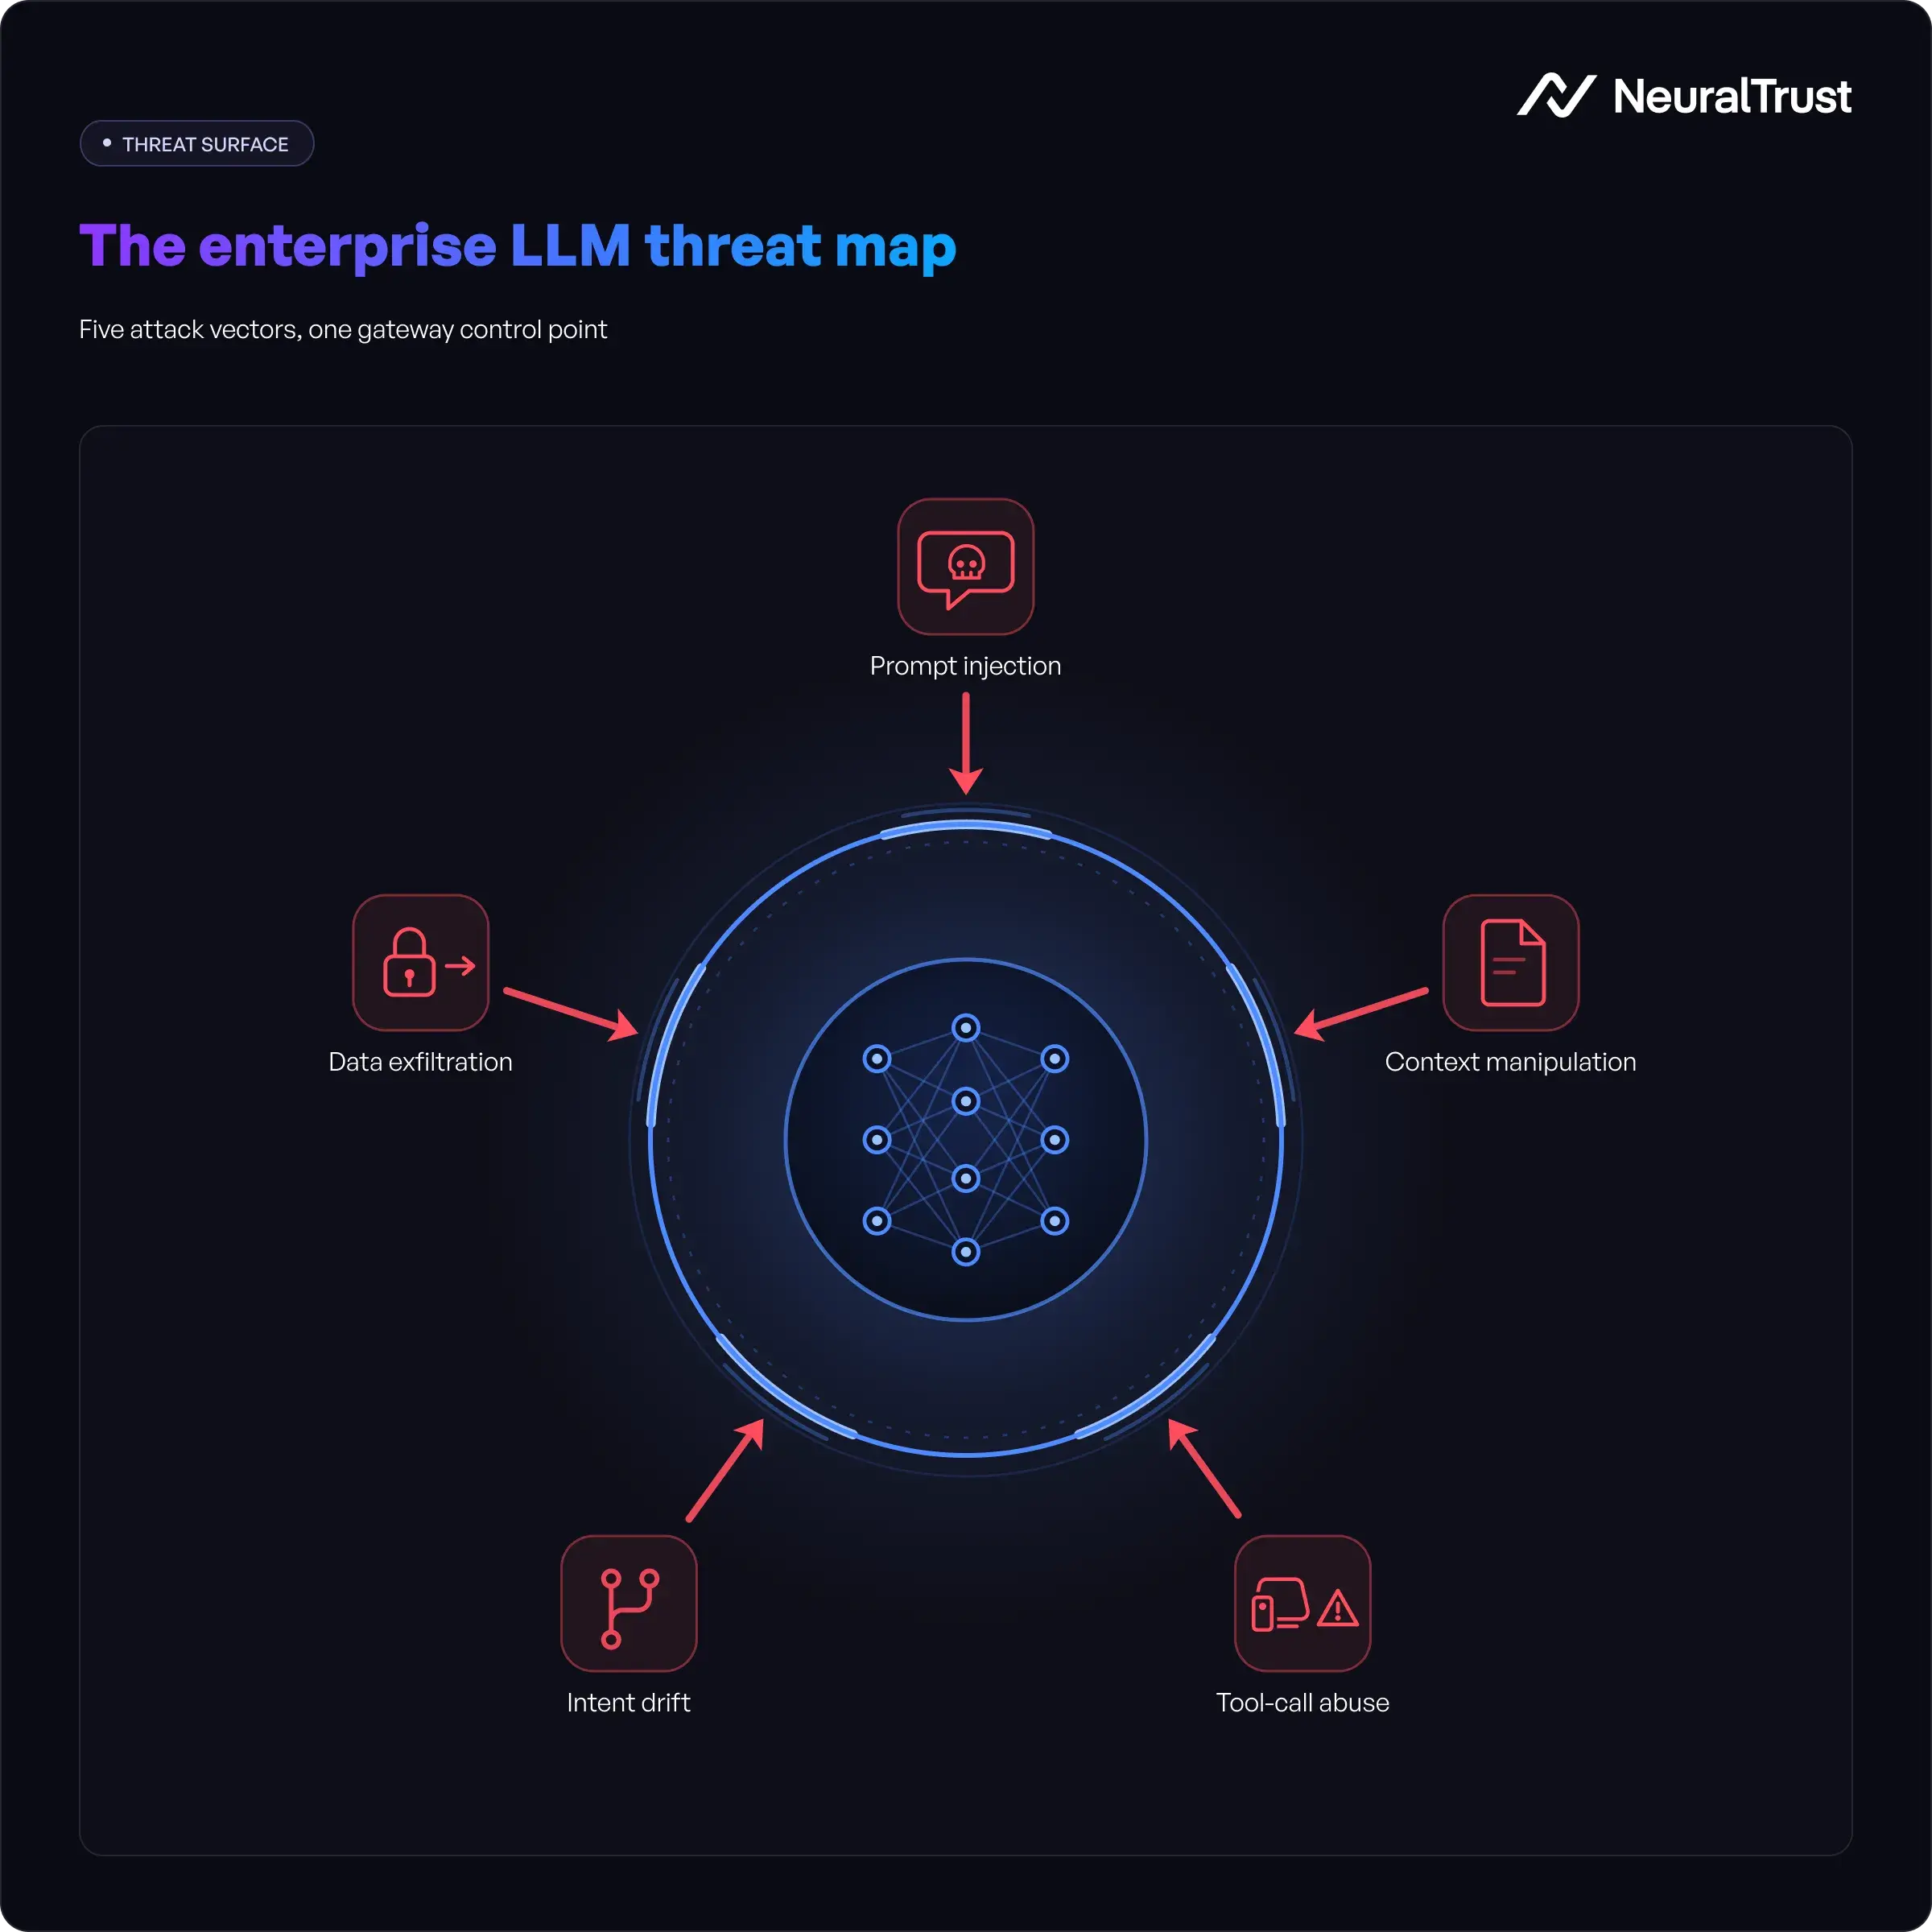
UK CISOs responsible for enterprise AI security need to understand five distinct threat categories:
1. Prompt injection
An adversary or a malicious user embeds instructions in a prompt that override the model's intended behaviour. The model executes the attacker's instruction rather than the application's intended task. OWASP has listed prompt injection as the number one vulnerability in LLM applications since the category was established. It is exploitable through user input, retrieved documents, API responses, and any content the model processes.
2. Indirect context manipulation
A more sophisticated variant of prompt injection where the malicious instruction is not in the user's input but in content the model retrieves (a document, a web page, an email) and processes as context. The model reads attacker-controlled content and follows instructions embedded within it. This is particularly dangerous for AI agents with access to external data sources.
3. Data exfiltration through model outputs
An AI application with access to internal data can be manipulated into including sensitive information in its completions. A model that knows about internal pricing, personnel records, or proprietary technical documentation can be induced to reveal that information through carefully constructed user prompts.
4. Agent tool-call abuse
AI agents equipped with tools (file access, API calls, database queries, code execution) can be manipulated into taking actions outside their intended scope. An agent designed to answer support queries can, under adversarial prompting, be induced to make unauthorised API calls, exfiltrate data through side channels, or modify records it was not intended to touch.
5. Intent drift
Over extended agent sessions, an agent's behaviour can deviate incrementally from its defined purpose through accumulated context manipulation across multiple turns. Each individual step appears within policy. The cumulative effect is not.
The following table maps these threat categories to the controls that address them and the security platform capabilities required:
| AI threat vector | Attack mechanism | Required control | Platform capability |
|---|---|---|---|
| Prompt injection | Adversarial input manipulates model behaviour | Prompt inspection and policy enforcement | AI gateway runtime policy engine |
| Indirect context manipulation | Malicious instructions in retrieved content | Context-aware content inspection | Runtime defence with retrieval monitoring |
| Data exfiltration via outputs | Sensitive data included in model completions | Output filtering and PII detection | Gateway-level output inspection |
| Agent tool-call abuse | Agent takes unauthorised actions via tools | Tool call monitoring and limits | Agent runtime security mesh |
| Intent drift | Incremental behavioural deviation over sessions | Session-level behavioural monitoring | LLM observability and anomaly detection |
What AI Security Platforms UK Enterprises Actually Need?
When UK security teams evaluate AI security platforms, the conversation typically starts with one question: what does this product actually protect? The answer should cover four distinct capability areas. Any platform that covers only one or two of them leaves the enterprise exposed on the others.
1. Runtime Defence and Policy Enforcement
The most critical capability is the one that runs on every model interaction in real time. Runtime defence intercepts prompts before they reach the model and completions before they reach the user, applying policy controls that detect and block adversarial content, enforce scope constraints, and flag anomalous behaviour.
For a UK enterprise, runtime defence must cover:
- Prompt injection detection across all input channels
- Output filtering for sensitive data, regulated content, and policy violations
- Scope enforcement, ensuring each AI application only does what it was deployed to do
- MCP (Model Context Protocol) traffic inspection for AI agents that connect to external tools and data sources
A runtime layer bolted onto the application tier is not sufficient. It applies inconsistently across different AI applications, cannot be audited centrally, and creates a governance gap wherever a team deploys a new AI feature outside the security team's visibility. Runtime defence must be an infrastructure control, not an application-level wrapper.
2. Enterprise AI Gateway Controls
An enterprise AI gateway is the infrastructure component that makes runtime defence consistent across the entire AI estate. It sits between all AI applications and all model providers, applying policy uniformly regardless of which application, team, or use case is generating the traffic.
For UK enterprises, the AI gateway layer delivers:
- Centralised policy enforcement: one policy configuration applies to all AI traffic, not one per application
- Identity-aware access control: model access governed by user role, application identity, and data classification rather than shared API keys
- Jurisdictional routing: regulated data routes only to approved providers, supporting UK GDPR transfer restrictions without per-application implementation
- Token budgets and rate limits: hard limits on per-user, per-application, and per-agent AI consumption that cap both cost risk and scope-violation risk simultaneously
- Audit logs at the infrastructure layer: structured, complete records of every model interaction, independent of individual development teams
For a deeper technical view of how an enterprise AI gateway operates, see AI Gateway Architecture: How It Works Under the Hood and AI Gateway Security: Protecting LLM Traffic.
3. LLM Observability for Audit and Compliance
UK CISOs cannot govern AI deployments they cannot see. LLM observability is the capability that makes AI activity visible at the interaction level: what was sent, what was returned, which policy rules triggered, which content was blocked, and how behaviour is changing over time.
For enterprise governance and regulatory compliance, LLM observability provides:
- Interaction logs: structured records of every prompt and completion, exportable for regulatory audit
- Policy violation dashboards: real-time and historical view of content policy breaches, blocked requests, and anomalous behaviour
- Scope monitoring: detection of AI applications operating outside their intended parameters
- SIEM integration: AI activity feeds into the same security operations infrastructure as network and endpoint telemetry
LLM observability is not a performance monitoring tool. For a UK CISO, it is the audit infrastructure that makes AI governance demonstrable to the ICO, to internal audit, and to board-level risk committees.
4. AI Governance Framework Integration
The fourth capability is the connective tissue between technical controls and organisational governance. An AI security platform must generate the outputs that governance frameworks consume: policy enforcement reports, compliance evidence packages, risk posture assessments, and the data that feeds into board-level AI risk reporting.
For UK enterprises operating under formal governance frameworks (whether NCSC guidelines, internal AI risk policies, or sector-specific regulatory requirements) the platform must integrate with existing GRC tooling and produce governance artefacts that non-technical stakeholders can use. Security controls that only surface data in a developer dashboard are not governance infrastructure. They are monitoring tools.
UK Regulatory Requirements That Shape Enterprise AI Security
UK CISOs face regulatory pressure from three distinct frameworks simultaneously. Understanding what each requires (and how a well-configured AI security platform addresses those requirements) is essential for building a defensible enterprise AI security posture.
NCSC AI Security Guidance
The UK's National Cyber Security Centre has published a substantial body of guidance on securing AI systems, including joint guidance with international partners on AI cybersecurity principles. The NCSC's framework for AI security emphasises five areas that align directly with enterprise AI security platform requirements:
- Secure design: AI systems should be designed with security as a first-class requirement, not a retrofit. This includes secure model selection, supply chain risk management for third-party models, and threat modelling for AI-specific attack vectors.
- Secure development: AI applications should be tested for adversarial robustness before deployment. Automated AI red teaming against OWASP LLM Top 10 vectors provides the evidence base for this requirement.
- Secure deployment: AI systems in production require runtime monitoring, policy enforcement, and access controls designed for AI traffic.
- Secure operation and maintenance: Ongoing monitoring of AI behaviour, anomaly detection, and incident response capability specifically for AI security events.
- Secure end of life: Model retirement, data handling at end of AI application lifecycle, and supplier management obligations.
An enterprise AI security platform that covers runtime defence, gateway controls, and LLM observability addresses NCSC principles 3 and 4 directly, and provides the technical evidence base for demonstrating compliance with principle 2.
UK GDPR and AI Data Processing Obligations
UK GDPR applies to AI deployments whenever personal data is processed. For most enterprise AI applications, this means almost always: customer support AI, HR AI tools, document analysis systems, and any AI that processes communications or records that could identify individuals all fall within UK GDPR scope.
The key UK GDPR obligations that bear on AI security platform selection are:
- Data minimisation: AI applications should not send more personal data to model providers than is necessary for the stated purpose. PII detection and redaction at the gateway layer enforces this without requiring developer-level implementation in each application.
- Purpose limitation: Personal data collected for one purpose cannot be processed for another. An AI security platform that enforces application scope constraints (blocking an application from answering queries outside its defined remit) directly supports purpose limitation.
- Transfer restrictions: Sending personal data to model providers based outside the UK or EEA requires appropriate transfer safeguards. Jurisdictional routing at the gateway layer ensures regulated data routes only to approved providers, with automated enforcement rather than developer discipline.
- Accountability: UK GDPR requires organisations to demonstrate compliance, not just assert it. Gateway-generated audit logs are the primary technical evidence of data processing compliance for AI applications.
The ICO's guidance on AI and data protection makes clear that accountability obligations extend into AI operations: organisations must be able to show what personal data their AI systems process, who has access to it, and what controls govern that processing.
EU AI Act: What UK Enterprises Still Need to Know
The UK is no longer subject to EU regulation by default following Brexit. However, UK enterprises are not exempt from the EU AI Act if they deploy AI systems that are used by EU residents, offer AI-powered services into EU markets, or use AI models developed by EU-regulated providers. For most large UK enterprises with any EU customer or partner exposure, the EU AI Act is a live compliance obligation.
The Act's risk classification creates specific security requirements for high-risk AI systems: those used in recruitment, credit scoring, education, critical infrastructure, and public services. These systems must implement risk management systems, maintain technical documentation of AI behaviour, generate interaction logs, and ensure human oversight mechanisms are in place.
An enterprise AI gateway operating at the infrastructure layer addresses each of these:
- The policy engine is the technical risk management control
- Interaction logs are the technical documentation
- Human oversight is enabled through the observability layer, which surfaces policy violations for human review in real time
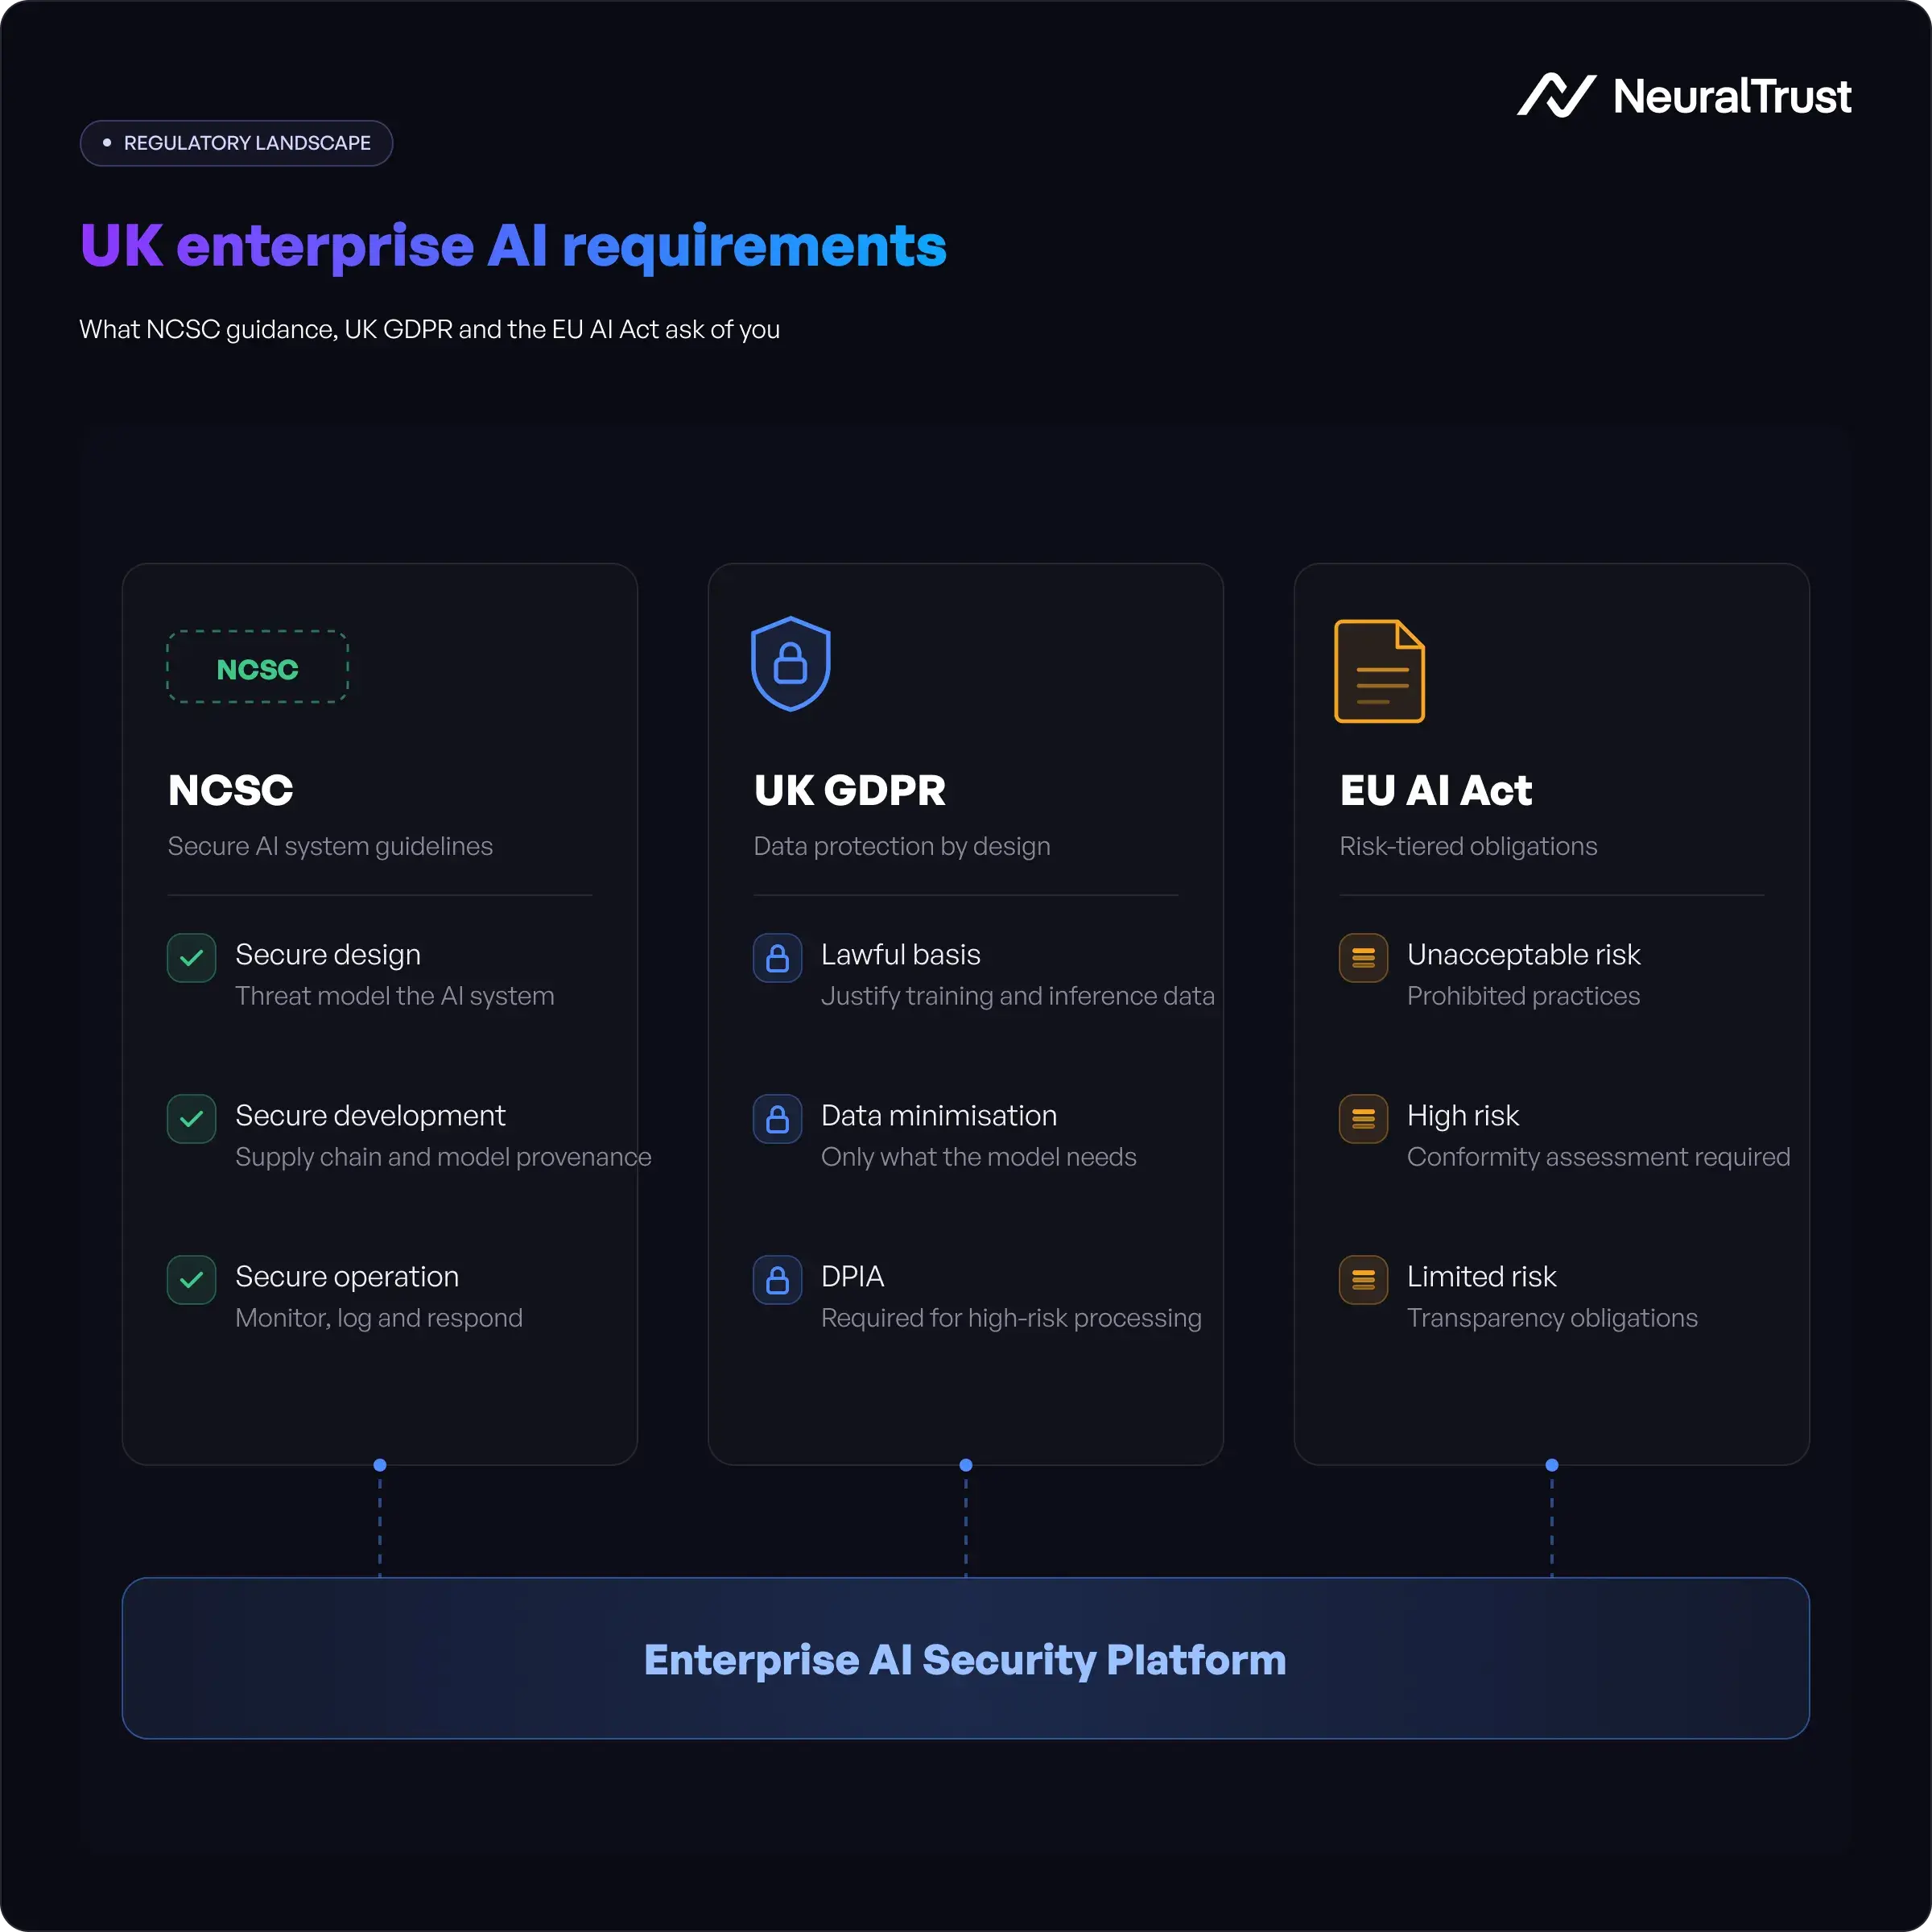
For UK enterprises with EU exposure, the EU AI Act compliance case for enterprise AI security investment is as strong as the NCSC and UK GDPR cases. A well-configured AI gateway delivers evidence across all three frameworks from a single infrastructure deployment. For a full breakdown of AI governance under these frameworks, see How an AI Gateway Solves AI Governance for Enterprise.
Building an Enterprise AI Security Stack: A UK CISO's Approach
Building enterprise AI security is a sequenced programme, not a single product purchase. The following sequence gives UK security teams a practical path from initial deployment to full governance coverage.
-
Conduct an AI asset inventory. Before deploying any security controls, establish what AI is already running in your organisation. This includes sanctioned deployments, shadow AI tools individual teams have adopted, and AI features embedded in SaaS products. You cannot govern what you have not found.
-
Deploy a central AI gateway as the control plane. Route all AI application traffic through a single gateway. This is the prerequisite for every subsequent security control. A gateway that does not see all traffic cannot enforce consistent policy.
-
Define governance profiles for each AI application. For every AI application in your inventory, document its permitted model providers, data classification scope, approved user base, and content policy requirements. This profile becomes the gateway policy configuration for that application.
-
Enable PII detection and jurisdictional routing for data-sensitive applications. Configure detection rules for the regulated data types your applications handle (health data, financial data, personal identifiers) and define routing policies that keep regulated data within UK-approved provider boundaries.
-
Activate runtime defence for all production AI applications. Enable prompt injection detection, output filtering, and scope enforcement across the gateway. Start with logging-only mode to baseline normal behaviour before switching to blocking mode.
-
Set token budgets and access controls by team and application. Replace shared API keys with identity-aware access policies. Set hard limits on per-user, per-application, and per-agent token consumption. This simultaneously controls cost risk and scope-violation risk.
-
Connect LLM observability output to your SIEM. AI security events should appear alongside network and endpoint telemetry in your security operations centre.
-
Run quarterly AI security reviews using gateway-generated compliance reports. Treat gateway audit exports as the primary evidence package for regulatory reviews, board AI risk reporting, and internal audit cycles.
-
Test AI applications against adversarial attack scenarios before major releases. Automated AI red teaming against OWASP LLM Top 10 vectors should be part of your secure development lifecycle for AI, not a one-time assessment.
-
Establish an AI security incident response playbook. Define what constitutes an AI security incident, who owns the response, what containment actions are available (gateway policy updates, application isolation, model routing changes), and what notification obligations apply.
Evaluating AI Security Platforms: A UK CISO's Checklist
When UK security teams reach the vendor evaluation stage, the conversation moves from strategy to capability. The following checklist gives procurement and security teams a consistent evaluation framework across AI security platform vendors.
| Evaluation dimension | What to assess | Minimum requirement for UK enterprise |
|---|---|---|
| Runtime defence | Prompt injection detection, output filtering, scope enforcement | Real-time enforcement on every model interaction, not sampling |
| Gateway architecture | Centralised or per-application deployment | Single infrastructure layer covering all AI traffic |
| LLM observability | Interaction logging, anomaly detection, compliance reporting | Structured logs exportable for regulatory audit |
| Access control | Identity-aware model access, token budgets, role-based routing | Per-user and per-application controls, not shared API keys |
| Data governance | PII detection, jurisdictional routing, data residency controls | UK/EU provider routing enforcement for regulated data |
| UK regulatory alignment | NCSC, UK GDPR, EU AI Act evidence outputs | Audit logs and compliance reports covering all three frameworks |
| Deployment model | SaaS, on-premises, hybrid | On-premises or UK-hosted option for data-sensitive deployments |
| Open-source availability | Core gateway components publicly available | Yes, for security review and supply chain assurance |
| Agent security | MCP traffic inspection, tool call monitoring, session limits | Native agent support, not an add-on capability |
| Integration | SIEM, ticketing, existing IAM infrastructure | Standard integrations with major enterprise security tooling |
Beyond the technical checklist, UK CISOs should assess three strategic dimensions that vendor marketing rarely addresses directly:
1. Architectural breadth
Does the platform cover the full AI security lifecycle: discovery, testing, gateway controls, and runtime defence, or does it specialise in one area? Point tools create integration burdens and governance gaps between them. A platform that covers the full lifecycle from a single deployment is significantly easier to operate, audit, and demonstrate to regulators.
2. European regulatory DNA
Was the platform built by a team that understands European data protection and AI regulation from the start, or is EU/UK compliance a feature bolted on for the market? The answer matters for how jurisdiction-aware routing, audit log structure, and compliance reporting are designed. NeuralTrust is headquartered in Barcelona, has a London office at 167 Great Portland Street, and built its platform to operate within European regulatory frameworks by default. See Best AI Security Platforms in the UK for 2026 for a broader market comparison.
3. Open-source foundation
Open-source availability of core platform components is a security assurance advantage for enterprise buyers. It enables independent security review of the codebase, reduces supply chain risk, and allows organisations to audit the tools they rely on for AI governance. NeuralTrust's AI gateway, TrustGate, is fully open source.
TrustGate: Enterprise AI Security for UK Teams
TrustGate is NeuralTrust's AI gateway. It implements runtime policy enforcement, LLM observability, identity-aware access control, and compliance logging from a single infrastructure deployment. UK security teams can deploy it free in their own environment (Kubernetes, VPC, or on-premises) with no application-level changes required.
- Runtime policy enforcement applies to every prompt and completion across all AI applications routing through the gateway. Content policies, prompt injection filters, PII detection rules, and scope constraints are configured declaratively and enforced uniformly.
- LLM observability is built into the data plane. Every interaction generates a structured log entry. Observability data feeds into the monitoring dashboard, SIEM integrations, and compliance reporting exports.
- Access control moves model access from shared API keys to identity-aware policies. Token budgets, role-based routing, per-application model restrictions, and per-agent session limits are configured centrally and enforced on all traffic.
- Jurisdictional routing keeps regulated data within UK-approved provider boundaries. Routing rules evaluate data classification tags and request metadata to enforce geographic constraints automatically.
- Audit exports produce structured compliance packages from the interaction log, covering the evidence requirements of NCSC guidance, UK GDPR accountability obligations, and EU AI Act technical documentation requirements.
For UK enterprises evaluating AI gateway options, TrustGate provides a production-grade security infrastructure, European-market-first design, and a platform roadmap driven by enterprise AI security requirements.
Try TrustGate Free Today
The fastest way to understand your enterprise AI security posture is to deploy the gateway and see what is already happening in your AI estate. TrustGate installs in minutes, requires no application changes, and immediately begins generating the visibility and control data your security programme needs.
No sales process. No credit card. Your infrastructure, your data.
FAQs for UK CISOs on Enterprise AI Security
1. What are AI security platforms and why do UK enterprises need them?
AI security platforms are purpose-built tools that protect AI applications, large language models, and autonomous AI agents from adversarial attacks, data exfiltration, and policy violations. UK enterprises need them because traditional security tools (firewalls, endpoint detection, SIEM platforms) operate at the network and endpoint layer. They cannot inspect the semantic content of LLM prompts and completions, detect prompt injection attacks, monitor AI agent behaviour, or enforce content policy on model outputs. AI security platforms fill this gap by operating at the AI layer, where the actual threats to modern enterprise AI deployments originate.
2. How does the NCSC's AI security guidance affect UK enterprise security programmes?
The UK National Cyber Security Centre has published guidance on securing AI systems that covers the full AI lifecycle: secure design, secure development, secure deployment, secure operation, and secure end of life. For enterprise security programmes, the most operationally significant requirements are in secure deployment and operation, runtime monitoring, access controls, and policy enforcement for production AI systems. UK CISOs should treat NCSC guidance as a baseline, not a ceiling. Organisations in regulated sectors (financial services, healthcare, utilities) typically face additional sector-specific requirements on top of the NCSC baseline.
3. Does UK GDPR apply to enterprise AI deployments?
Yes, in almost all cases. UK GDPR applies whenever personal data is processed, and most enterprise AI applications process personal data: customer names, communication records, HR information, and financial data frequently appear in the prompts and context that AI applications handle. The key obligations for AI deployments are data minimisation (sending only necessary data to model providers), purpose limitation (using data only for its stated purpose), transfer restrictions (governing which model providers receive UK personal data), and accountability (demonstrating that controls are in place through audit logs and compliance records). An enterprise AI gateway addresses each of these at the infrastructure layer.
4. Does the EU AI Act apply to UK enterprises post-Brexit?
The EU AI Act applies to UK enterprises that deploy AI systems used by EU residents, offer AI-powered services into EU markets, or operate AI that affects individuals in the EU. Most large UK organisations with any EU customer, partner, or operational exposure have some EU AI Act obligations. High-risk AI systems (those used in HR, credit scoring, education, critical infrastructure, and public-facing services) carry the most significant obligations: risk management systems, interaction logs, human oversight mechanisms, and technical documentation. A well-configured enterprise AI gateway addresses these obligations at the infrastructure layer.
5. What is LLM observability and how does it support enterprise AI governance?
LLM observability is the practice of monitoring AI application behaviour at the interaction level: capturing what prompts are sent to models, what completions they return, which policy rules trigger, and how behaviour evolves over time. For UK enterprise governance, LLM observability is the audit infrastructure: it generates the structured interaction records that regulators, auditors, and compliance functions need to verify that AI security controls are working. Without LLM observability, an organisation cannot demonstrate to the ICO, to internal audit, or to the board what its AI systems are doing and how they are being governed. See LLM Observability with an AI Gateway for a full technical breakdown.
6. How does an AI gateway differ from a traditional API gateway for enterprise security purposes?
A traditional API gateway manages HTTP traffic at the request level: routing, authentication, rate limiting, and load balancing. It has no understanding of the semantic content of the payloads it handles; it cannot detect whether a prompt contains a prompt injection attack, whether a completion includes sensitive personal data, or whether an AI agent is behaving outside its defined scope.
An AI gateway operates at the content level: it inspects prompt and completion semantics, applies natural language policy rules, detects adversarial inputs, and enforces governance controls that depend on what is being communicated rather than just the volume of traffic. For enterprise security, this content-level understanding is what distinguishes an AI gateway from a general-purpose API proxy.
See AI Gateway vs MCP Gateway for a comparison of gateway architectures in agentic AI contexts.
7. What should UK CISOs look for when evaluating AI security platforms?
UK CISOs should evaluate AI security platforms across ten dimensions: runtime defence quality, gateway architecture (centralised vs. per-application), LLM observability capability, access control granularity, data governance and PII handling, alignment with UK regulatory frameworks (NCSC, UK GDPR, EU AI Act), deployment model options (SaaS, on-premises, hybrid), open-source availability for security review, native AI agent support, and integration with existing enterprise security tooling. Beyond the technical checklist, prioritise platforms with European regulatory DNA built into the design.
About the Author
Roger Howroyd is Head of Global SEO and AI at NeuralTrust, where he leads the company's search strategy across SEO, AEO, GEO, and LLM optimization. He specializes in AI-powered search, content strategy, and SEM. Connect on LinkedIn.
NeuralTrust is the leading platform for securing and scaling AI agents. Named a Pioneer in the Gartner Emerging Market Quadrant for AI Application Security 2026 and recognised across four Gartner Hype Cycle reports in the same year. Headquartered in Barcelona with offices in London (167 Great Portland Street) and New York. ISO 27001 certified.