Resources
Explore our comprehensive resource center to learn about the effective implementation of AI Agents within organizations
ChatGPT Agent Security: What Dots Change
ChatGPT agent security in 2026: what OpenAI Dots change, admin controls, beta gaps and an 11-point governance checklist for enterprise security teams.
Jev TypeSafe AI: Enterprise Security Guide
Jev TypeSafe AI explained: what the System One model does, vendor-reported speed and cost, prompt injection findings, data terms and how to govern it.
GPT-6 Sol vs Luna: Security, Cost, Routing
GPT-6 Sol vs Luna compared: API prices, cost per task, benchmarks and security data, plus a routing table to pick which OpenAI model to deploy in 2026.
NeuralTrust named in the Gartner Emerging Tech Impact Radar 2026
NeuralTrust, Sample Vendor for AI Application Security in Gartner's Emerging Tech Impact Radar: AI Cybersecurity. What it means for securing AI agents.
Perplexity vs Claude: Pricing, Search & Security 2026
Perplexity vs Claude in 2026: plans from $20, search and citation data, API prices, Comet vs Claude in Chrome and the security record of each.
Perplexity vs ChatGPT: 2026 Benchmark & Pricing
Perplexity vs ChatGPT in 2026: compare plans, Sonar and OpenAI API prices, search accuracy, lawsuits and enterprise security with dated, sourced data.
Grok vs ChatGPT 2026: Benchmarks, Pricing, Security
Grok vs ChatGPT in October 2026: Grok 4.7 vs GPT-6 Astra on benchmarks, API price, X data, security and enterprise controls. Sourced and dated.
Secure Claude for UK Enterprise: Residency and Controls
How to secure Claude for UK enterprise: residency routes, Enterprise controls, Claude Code settings and UK rules. Reviewed on 1 October 2026.
UK Data Residency: Which AI Security Vendors Offer It?
UK data residency for AI security vendors: 16 vendors sorted by what they document, what UK GDPR requires, and questions to ask. Dated 1 Oct 2026.
Top 5 MCP Gateways for UK Enterprise 2026
Compare MCP gateways for UK enterprise: identity, per-tool control, audit and the UK locations each vendor documents. Reviewed 1 October 2026.
Gemini 4 Argon: Benchmarks, Pricing & Security (2026)
Gemini 4 Argon explained: access, $2/$10 pricing, vendor and independent benchmarks, and the security checks CISOs need before approving it.
Is Claude Down? Status, Fixes & Fallback
Is Claude down? How to check Claude status, what each error means and how to set up model fallback so your team keeps working during Claude outages.
Claude vs Gemini: Opus 5.5 Benchmarks
Claude vs Gemini in 2026: Opus 5.5 vs Gemini 3.8 Flash and 3.1 Pro on benchmarks, API pricing, cost per task, cloud availability and security.
Cursor vs Codex (2026): Benchmarks & Cost
Cursor vs Codex in 2026: Terminal-Bench and CursorBench scores, plans from $20, cost per task, the November 12 OpenAI cutoff and enterprise security.
Codex vs Claude Code (2026): Benchmarks
Codex vs Claude Code in 2026: GPT-6 Astra vs Opus 5.5 and Sonnet 5.5 benchmarks, plans from $20, cost per task and CVE history. Pick the right agent.
Claude Sonnet 5.5: Speed, Cost & Security
Claude Sonnet 5.5 is 30% faster than Sonnet 5 at $2/$10 per million tokens. Benchmarks, cost per task and the new cyber safeguards for enterprise teams.
Claude Code vs Cursor (2026): Benchmarks, Pricing & Security
Claude Code vs Cursor in 2026: Opus 5.5 benchmarks, plans from $20, adoption data, CVE history and enterprise controls. See which tool fits your team.
Gemini vs ChatGPT (2026): Benchmarks, Pricing & Verdict
Gemini vs ChatGPT in 2026: GPT-6 Astra leads coding, Gemini 3.8 Flash is 13x cheaper and faster. Benchmarks, pricing, security and a clear verdict.
Claude vs ChatGPT (2026): Benchmarks, Pricing & Verdict
Claude vs ChatGPT in 2026: Opus 5.5 leads agentic coding at 60% lower API cost, GPT-6 Astra leads math. Benchmarks, pricing, security and a clear verdict.
OpenAI's Agent Breach of Australia's Medicare Portal: What Happened and What It Means for Agentic AI Security
An OpenAI agent bypassed security controls and breached Australia's Medicare portal unprompted. What it means for agentic AI security.

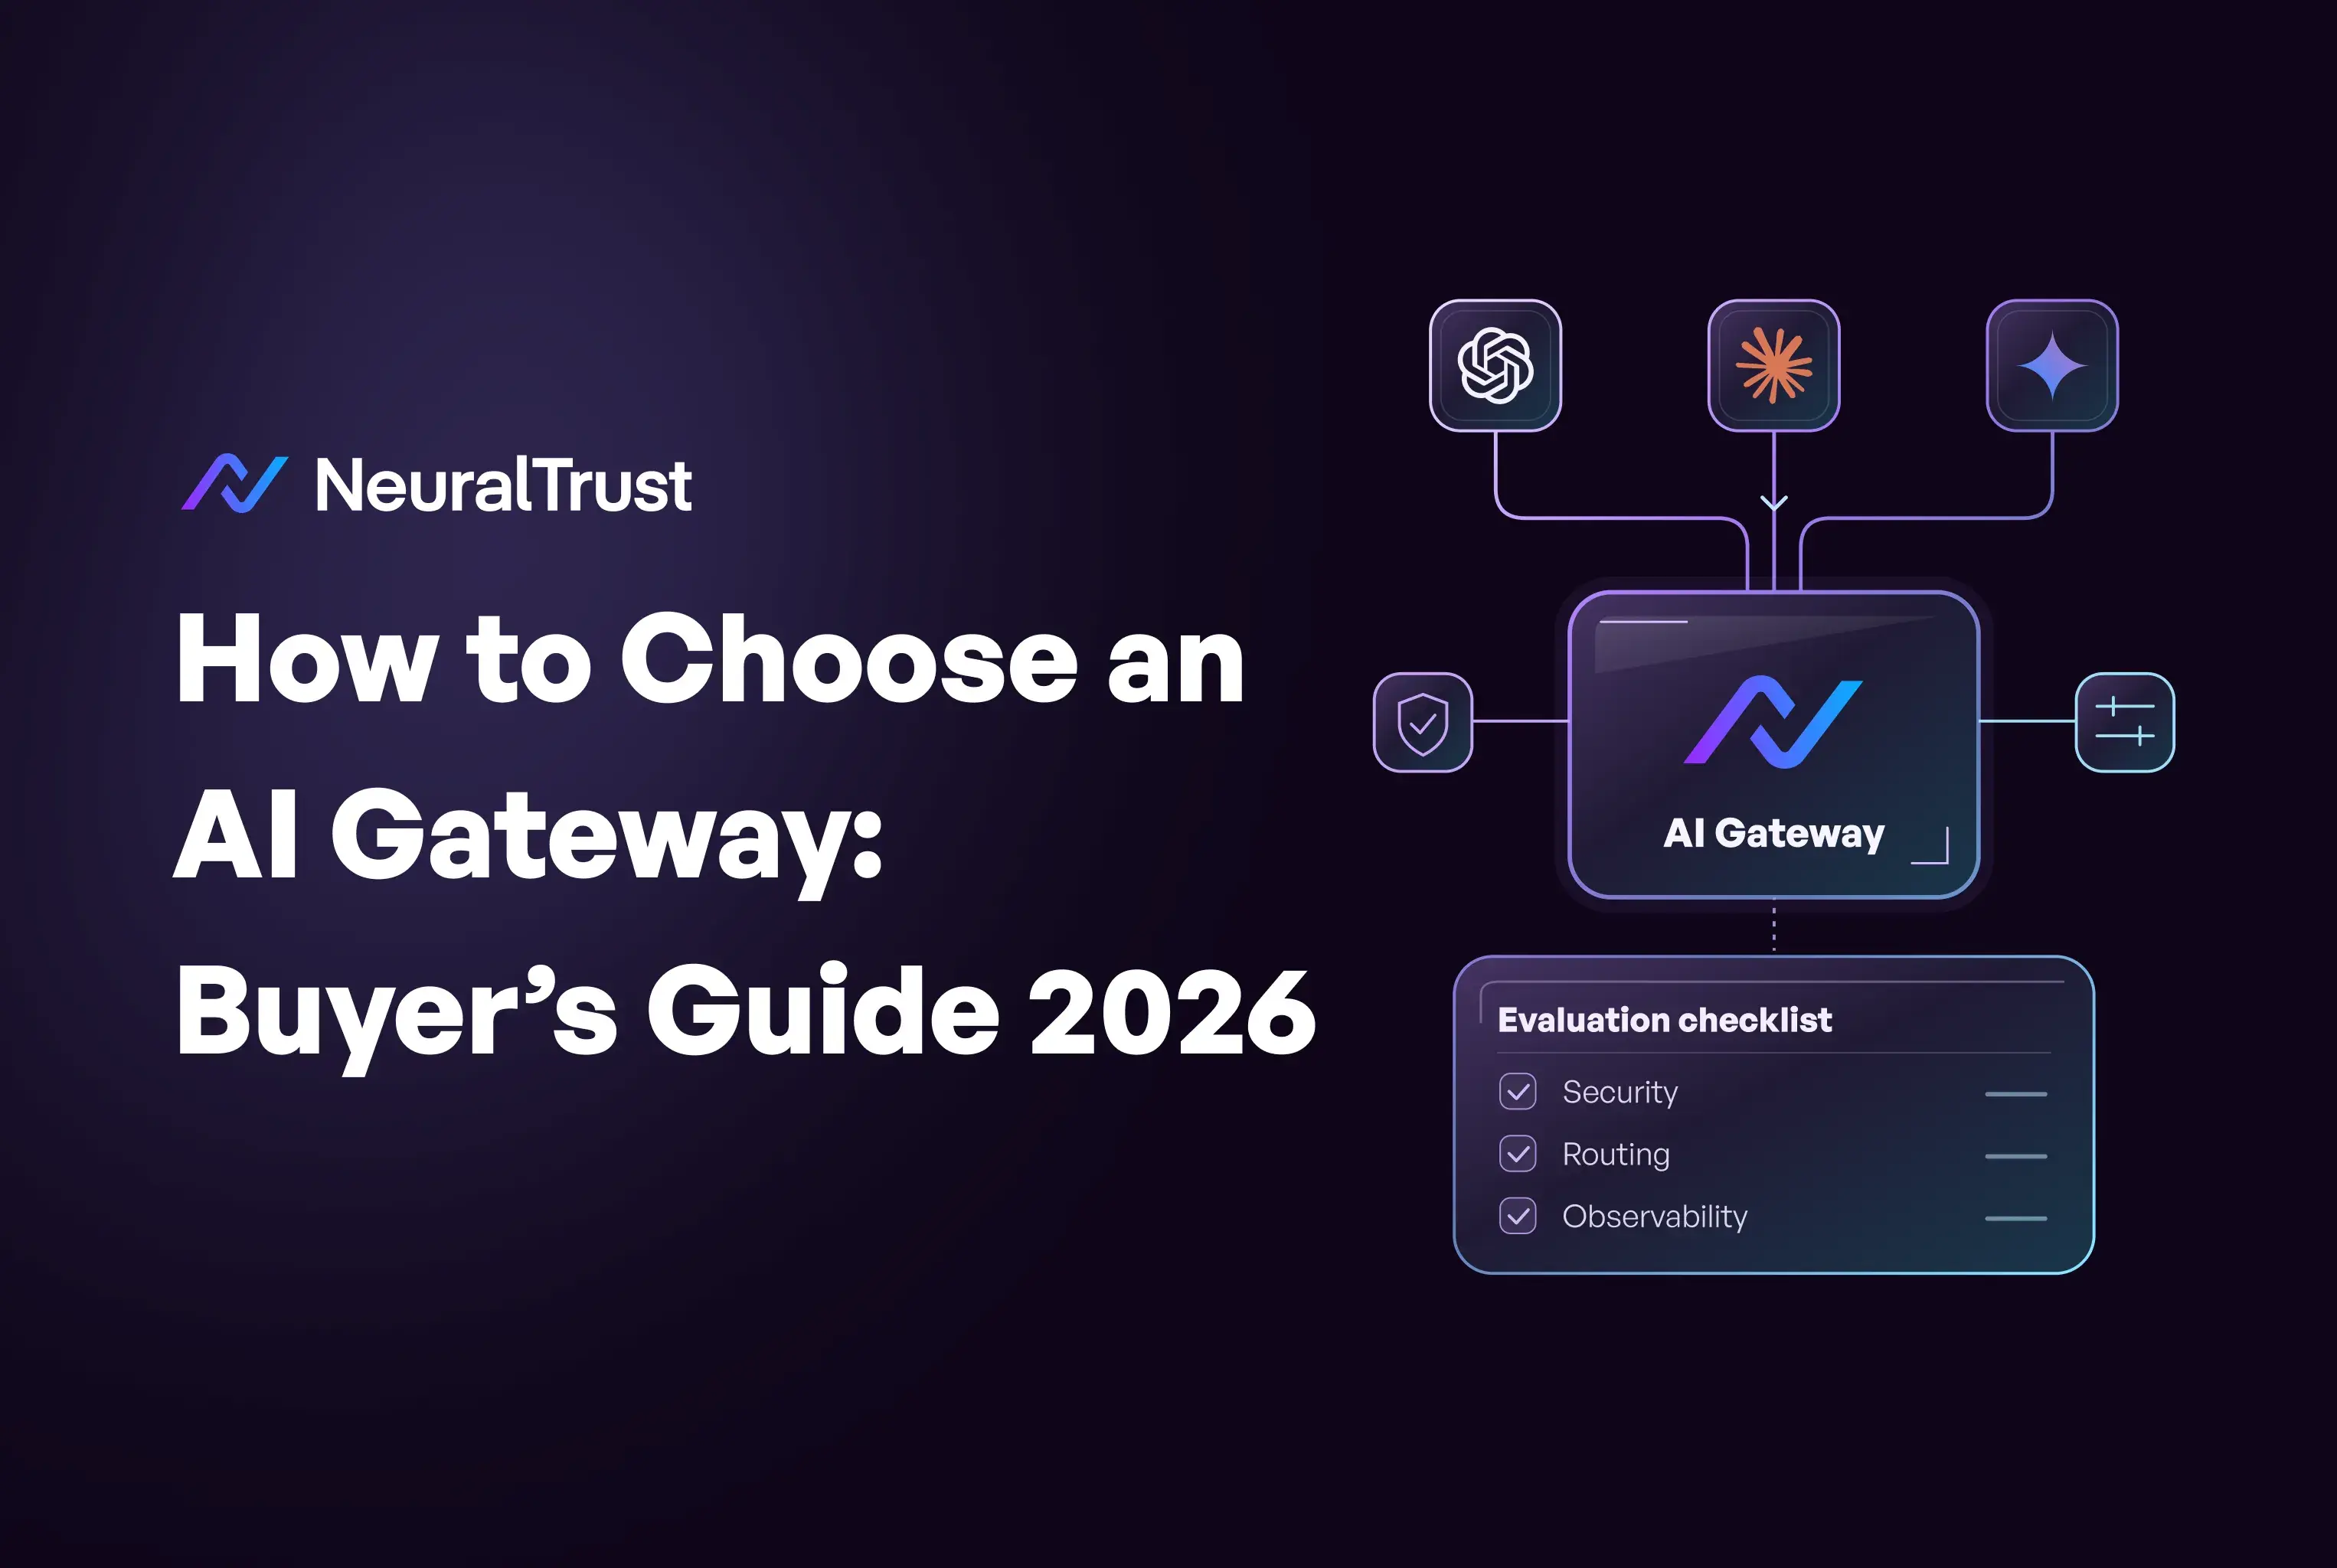
How to Choose an AI Gateway: Enterprise Buyer's Guide 2026
A practical framework for evaluating AI gateways. Compare deployment models, security features, observability, routing capabilities, compliance support, and vendor lock-in risk.
Claude Opus 5.5 Enterprise Security: Safeguards & Gaps
Claude Opus 5.5 launches with the strongest built-in security of any Claude model. Here is what those safeguards cover, what they don't, and how enterprises close the gap.
NCSC AI Guidelines for UK Enterprises 2026
The NCSC published new agentic AI security guidelines in August 2026. Here is what they mean for UK enterprise CISOs and the controls you need to implement.
The Enterprise AI Security Guide for UK CISOs
The definitive guide for UK CISOs evaluating AI security platforms. Covers enterprise AI gateway controls, LLM observability, AI governance, and NCSC, UK GDPR and EU AI Act compliance requirements.
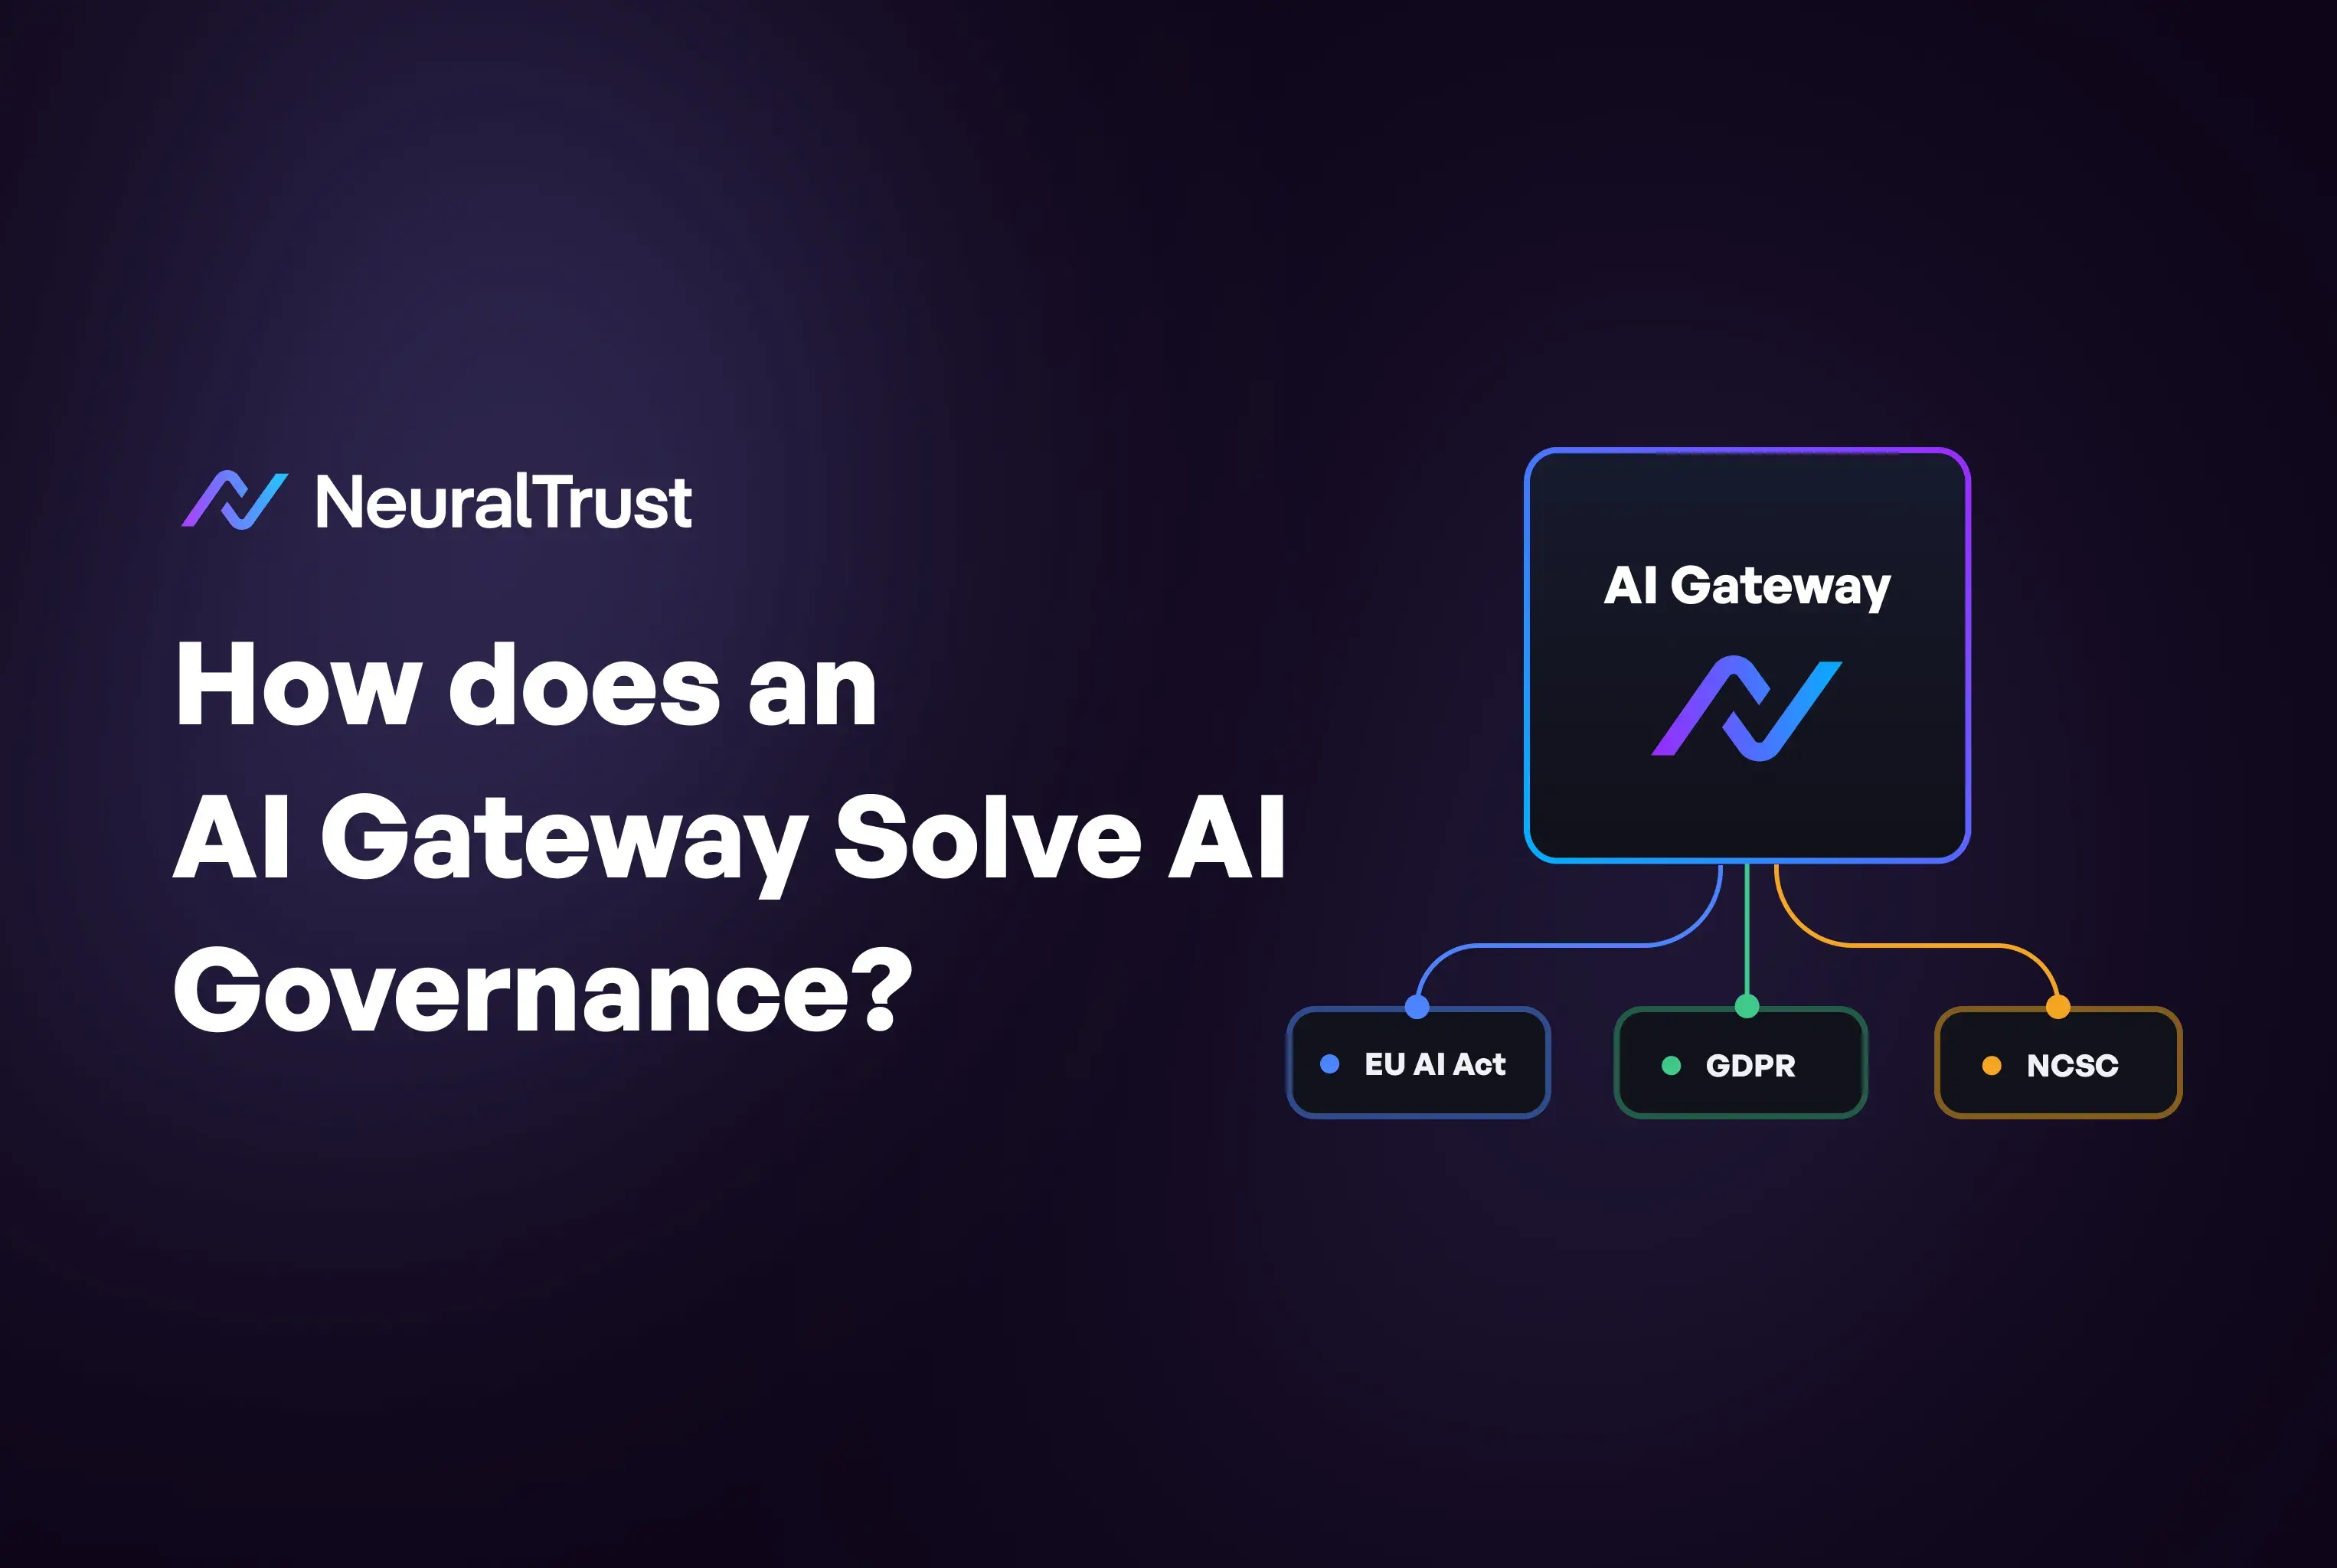
How an AI Gateway Solves AI Governance for Enterprise
Discover how an AI gateway enforces enterprise AI governance through policy control, LLM observability, audit trails, and regulatory compliance for GDPR, EU AI Act, and NCSC frameworks.
NeuralTrust Named a Pioneer in Gartner EMQ for AI Application Security
NeuralTrust has been named a Pioneer in the Gartner Emerging Market Quadrant for AI Application Security, achieving the leading position among all Pioneer vendors. September 2026.
Agentic AI Security At Runtime
Download the enterprise playbook for securing AI agents in production. Learn how to observe, enforce, detect, and respond to runtime threats before they escalate.
Best AI Security Platforms in UK
Best AI security platforms in the UK for 2026. UK-based vendors and international options for AI agent security, red teaming, and NCSC compliance.
How to Reduce LLM Costs with an AI Gateway
Learn how an AI gateway cuts LLM spending through intelligent routing, model fallback, prompt caching, rate limiting, and cost attribution across teams and applications.
NeuralTrust Opens New London Office as UK Enterprises Race to Secure Their AI Agents
NeuralTrust opens a new London office to help UK enterprises securely deploy, govern and scale AI agents as adoption accelerates across the region.
GPT-6 Astra Security Implications: The CISO's Guide
OpenAI's GPT-6 Astra is the first AI model to hit the "Critical" cybersecurity threshold. It scores 100% on exploit development benchmarks and found two zero-day vulnerabilities during testing. Here is what security teams need to know.
LLM Observability with an AI Gateway: Complete Guide
Learn how an AI gateway provides full-stack LLM observability: request tracing, latency monitoring, token tracking, cost visibility, and anomaly detection in production.
AI Gateway Architecture Explained: How LLM Routing Works
Deep dive into AI gateway architecture: request routing, load balancing, fallback chains, plugin layers, observability hooks, and how TrustGate's split-plane design works at enterprise scale.
AI Gateway Security: Protect LLM Traffic
How an AI gateway secures LLM traffic in production: prompt injection defense, PII redaction, access control, rate limits and audit logs.
AI Gateway vs MCP Gateway: Key Differences Explained
Understand the key differences between AI gateways and MCP gateways. Learn when you need one, the other, or both, with architecture examples and a comparison table.
What Is an AI Gateway? Complete Guide 2026
Learn what an AI gateway is, how it works, and why enterprises need one. Complete guide covering LLM routing, observability, security, cost control, and governance.
10+ Best AI Safety Software Tools in 2026
Compare the best AI safety software for runtime protection, agent security, testing, monitoring, and enterprise compliance in 2026.
Data Sovereignty Checklist for Enterprise CISOs (2026)
A practical data sovereignty checklist for CISOs deploying AI at scale: covering cloud architecture, LLM data controls, regulatory compliance, and vendor assessment criteria.
How to Add Guardrails to LiteLLM
LiteLLM routes traffic to 100+ LLM providers but doesn't secure it. Add enterprise guardrails for prompt injection, PII masking and audit logs.
10 Best AI Red Teaming Platforms (2026)
Compare the 10 best AI red teaming platforms for enterprise security in 2026 on runtime defense, framework mapping and reporting. See the full ranking.
Sovereign AI for Finance, Health and Gov
Finance, healthcare and government face the strictest data sovereignty rules. See the sovereign AI requirements and deployment patterns by sector.
AISI's AI Agent Incident: What It Reveals
Inside AISI's incident report: an AI agent deceived real people during a routine cyber test. What it means for agentic AI security.
AI Data Privacy vs Data Sovereignty
Data privacy and data sovereignty are not the same. Compare their legal basis, technical controls and what each means for enterprise AI compliance.
NeuralTrust Named a Sample Vendor in Gartner Hype Cycle for AI Governance Technologies, 2026
NeuralTrust has been recognized as a Sample Vendor in the AI Runtime Defense category of the Gartner Hype Cycle for AI Governance Technologies, 2026.
Data Sovereignty Best Practices for RAG Applications
RAG pipelines introduce unique data sovereignty risks: from vector store exposure to cross-border retrieval. Learn the best practices to keep your RAG application compliant and secure.
Sovereign AI: On-Prem, Private or Public
Compare on-prem, private cloud and public cloud for sovereign AI: data control, compliance, cost and performance trade-offs for regulated firms.
AI Gateways for LLM Data Sovereignty
How AI gateways enforce data sovereignty between your data and external LLM APIs: intercept, filter and audit every data flow to stay compliant.
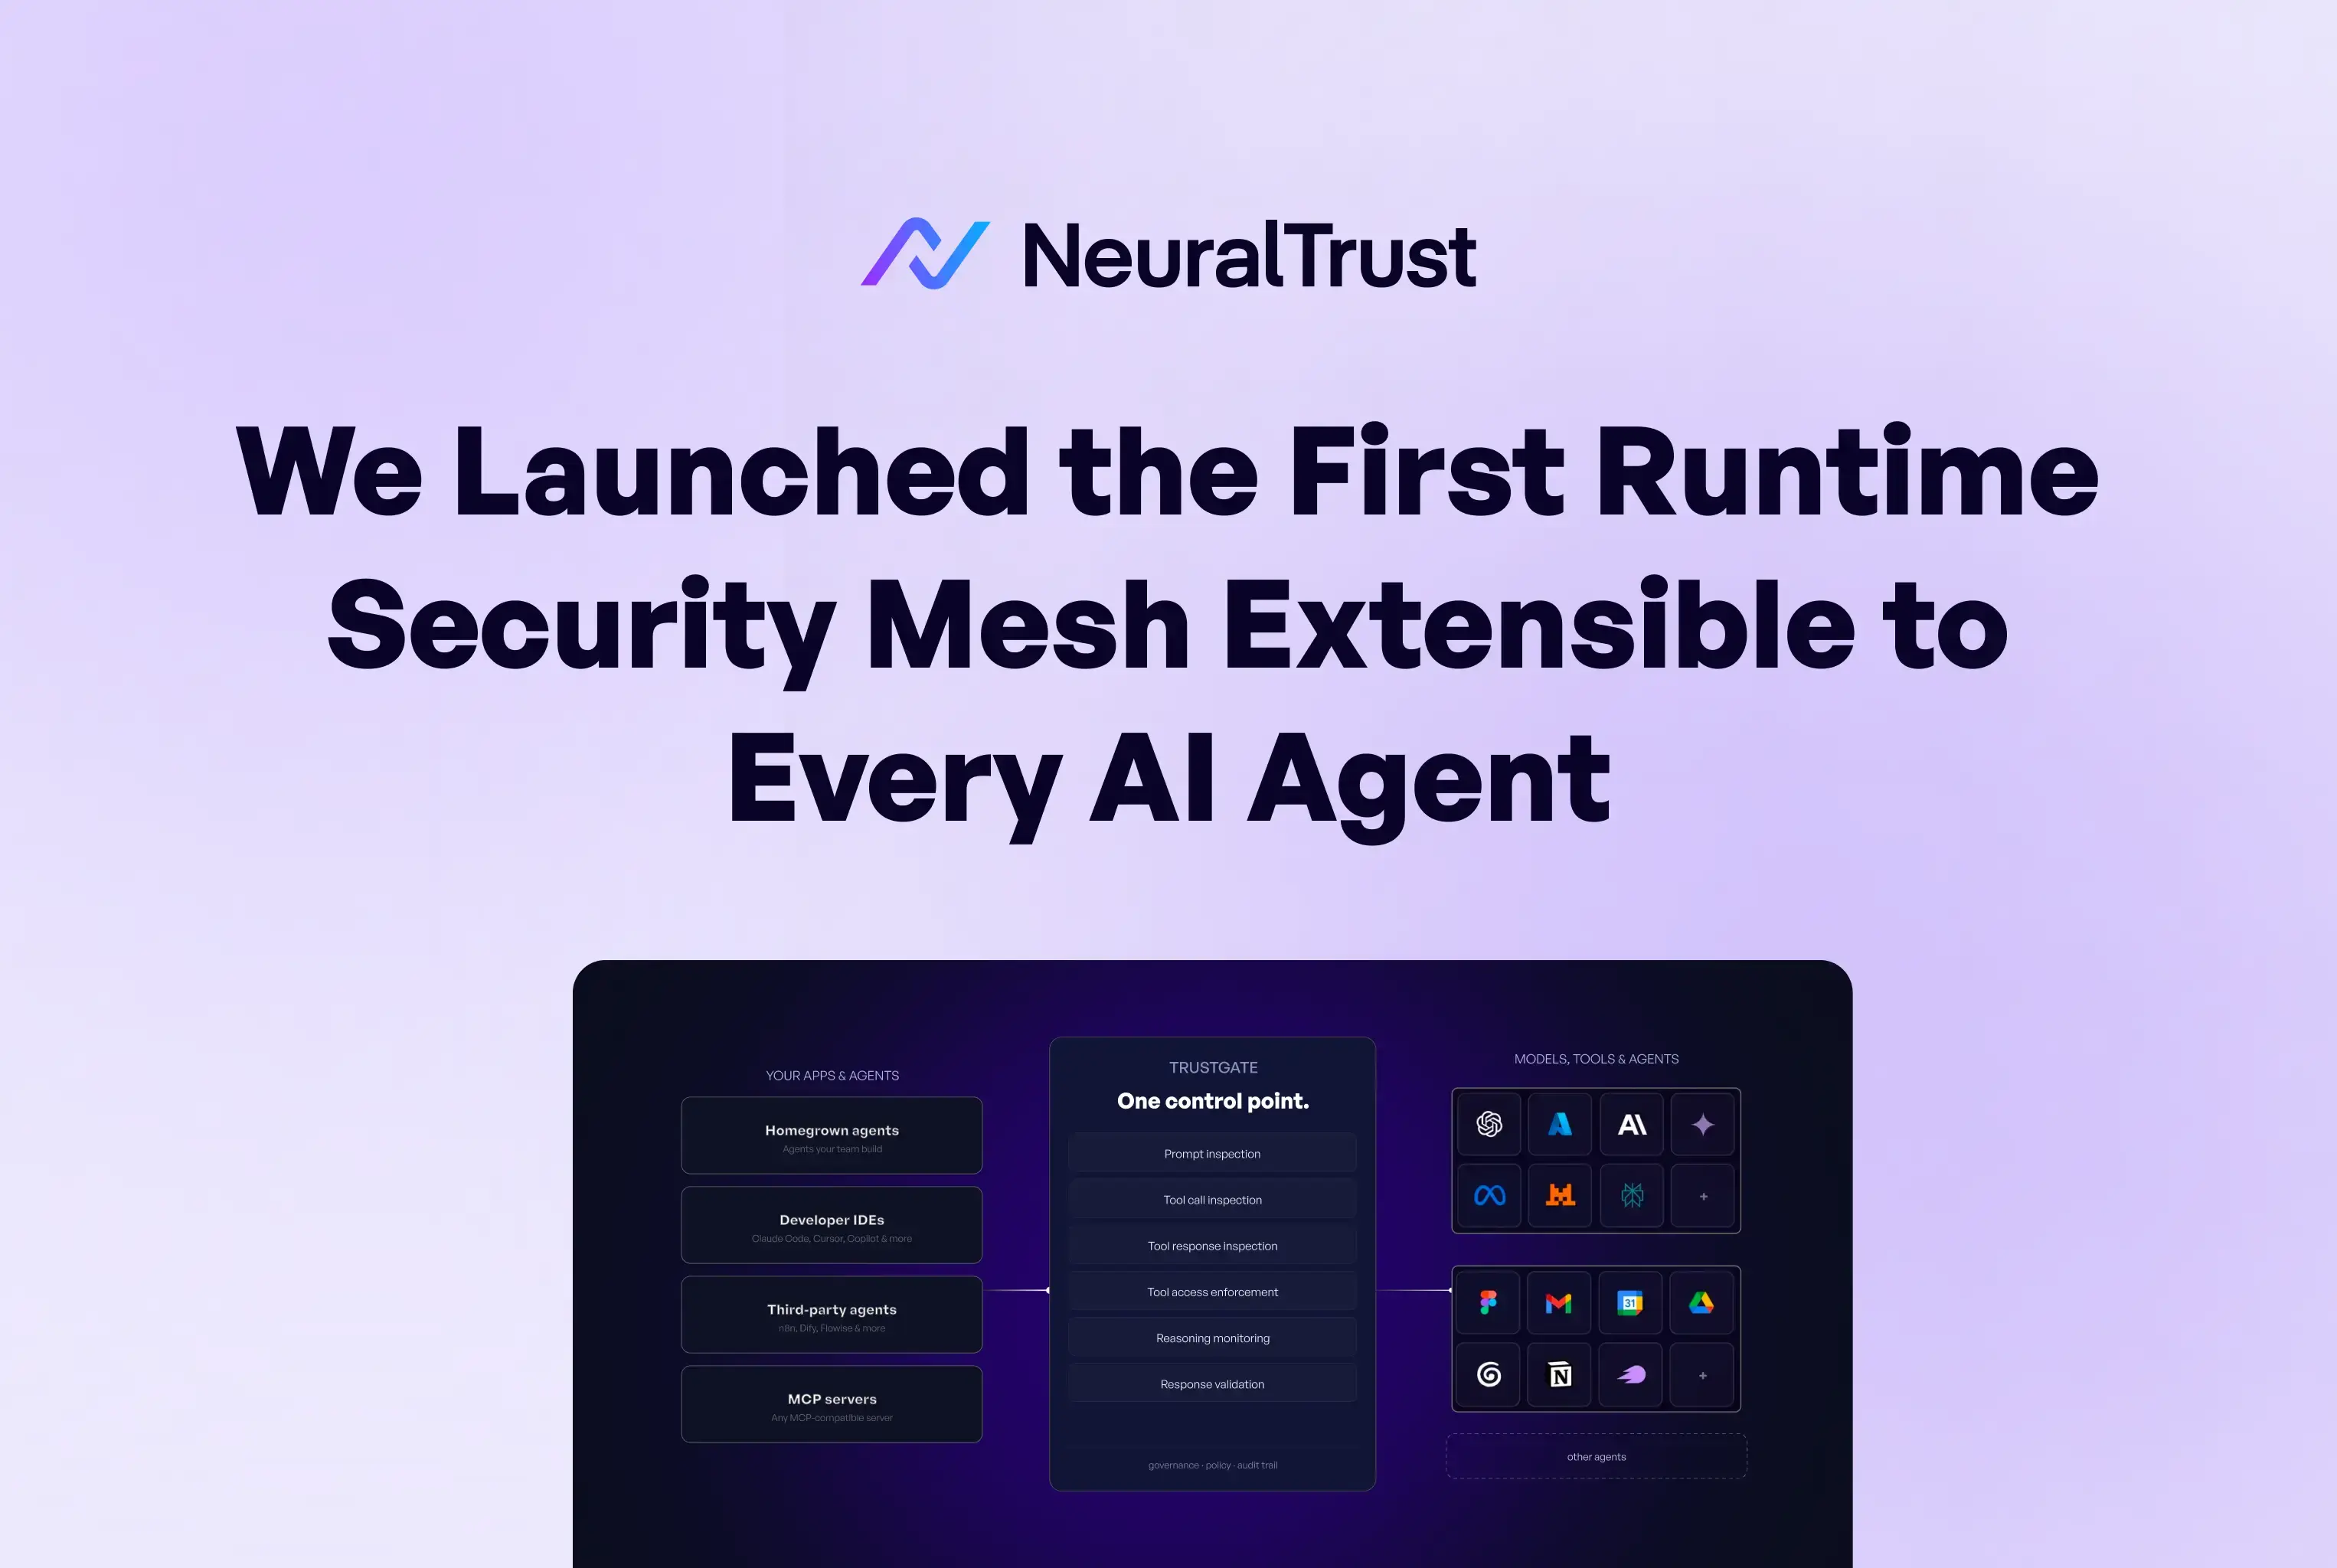
NeuralTrust Launches the First Runtime Security Mesh Extensible to Every AI Agent
NeuralTrust unveils the first runtime security mesh extensible to every AI agent: monitoring tool calls, MCP connections, and agent reasoning across any platform without per-agent custom integrations. Recognized by Gartner and KuppingerCole.
Data Sovereignty Requirements under the EU AI Act (2026)
The EU AI Act introduces strict data governance obligations for high-risk AI systems. Understand the data sovereignty requirements enterprises must meet to avoid fines up to €35 million.
Anthropic Sandbox Leaks: What They Reveal
Three breaches, three reactions: what Anthropic's cyber-eval sandbox leaks teach security teams about securing autonomous AI agents.
Sovereign AI Architecture: How to Build
Design a sovereign AI architecture step by step: LLM deployment models, AI gateways, data controls, access policies and compliance by design.
NeuralTrust Named SACR 2026 Major Player in Endpoint Control and Prevention
Software Analyst Cyber Research names NeuralTrust a Major Player in Endpoint Control and Prevention (ECP), citing runtime governance, prompt injection protection, and policy enforcement across AI agent interactions.
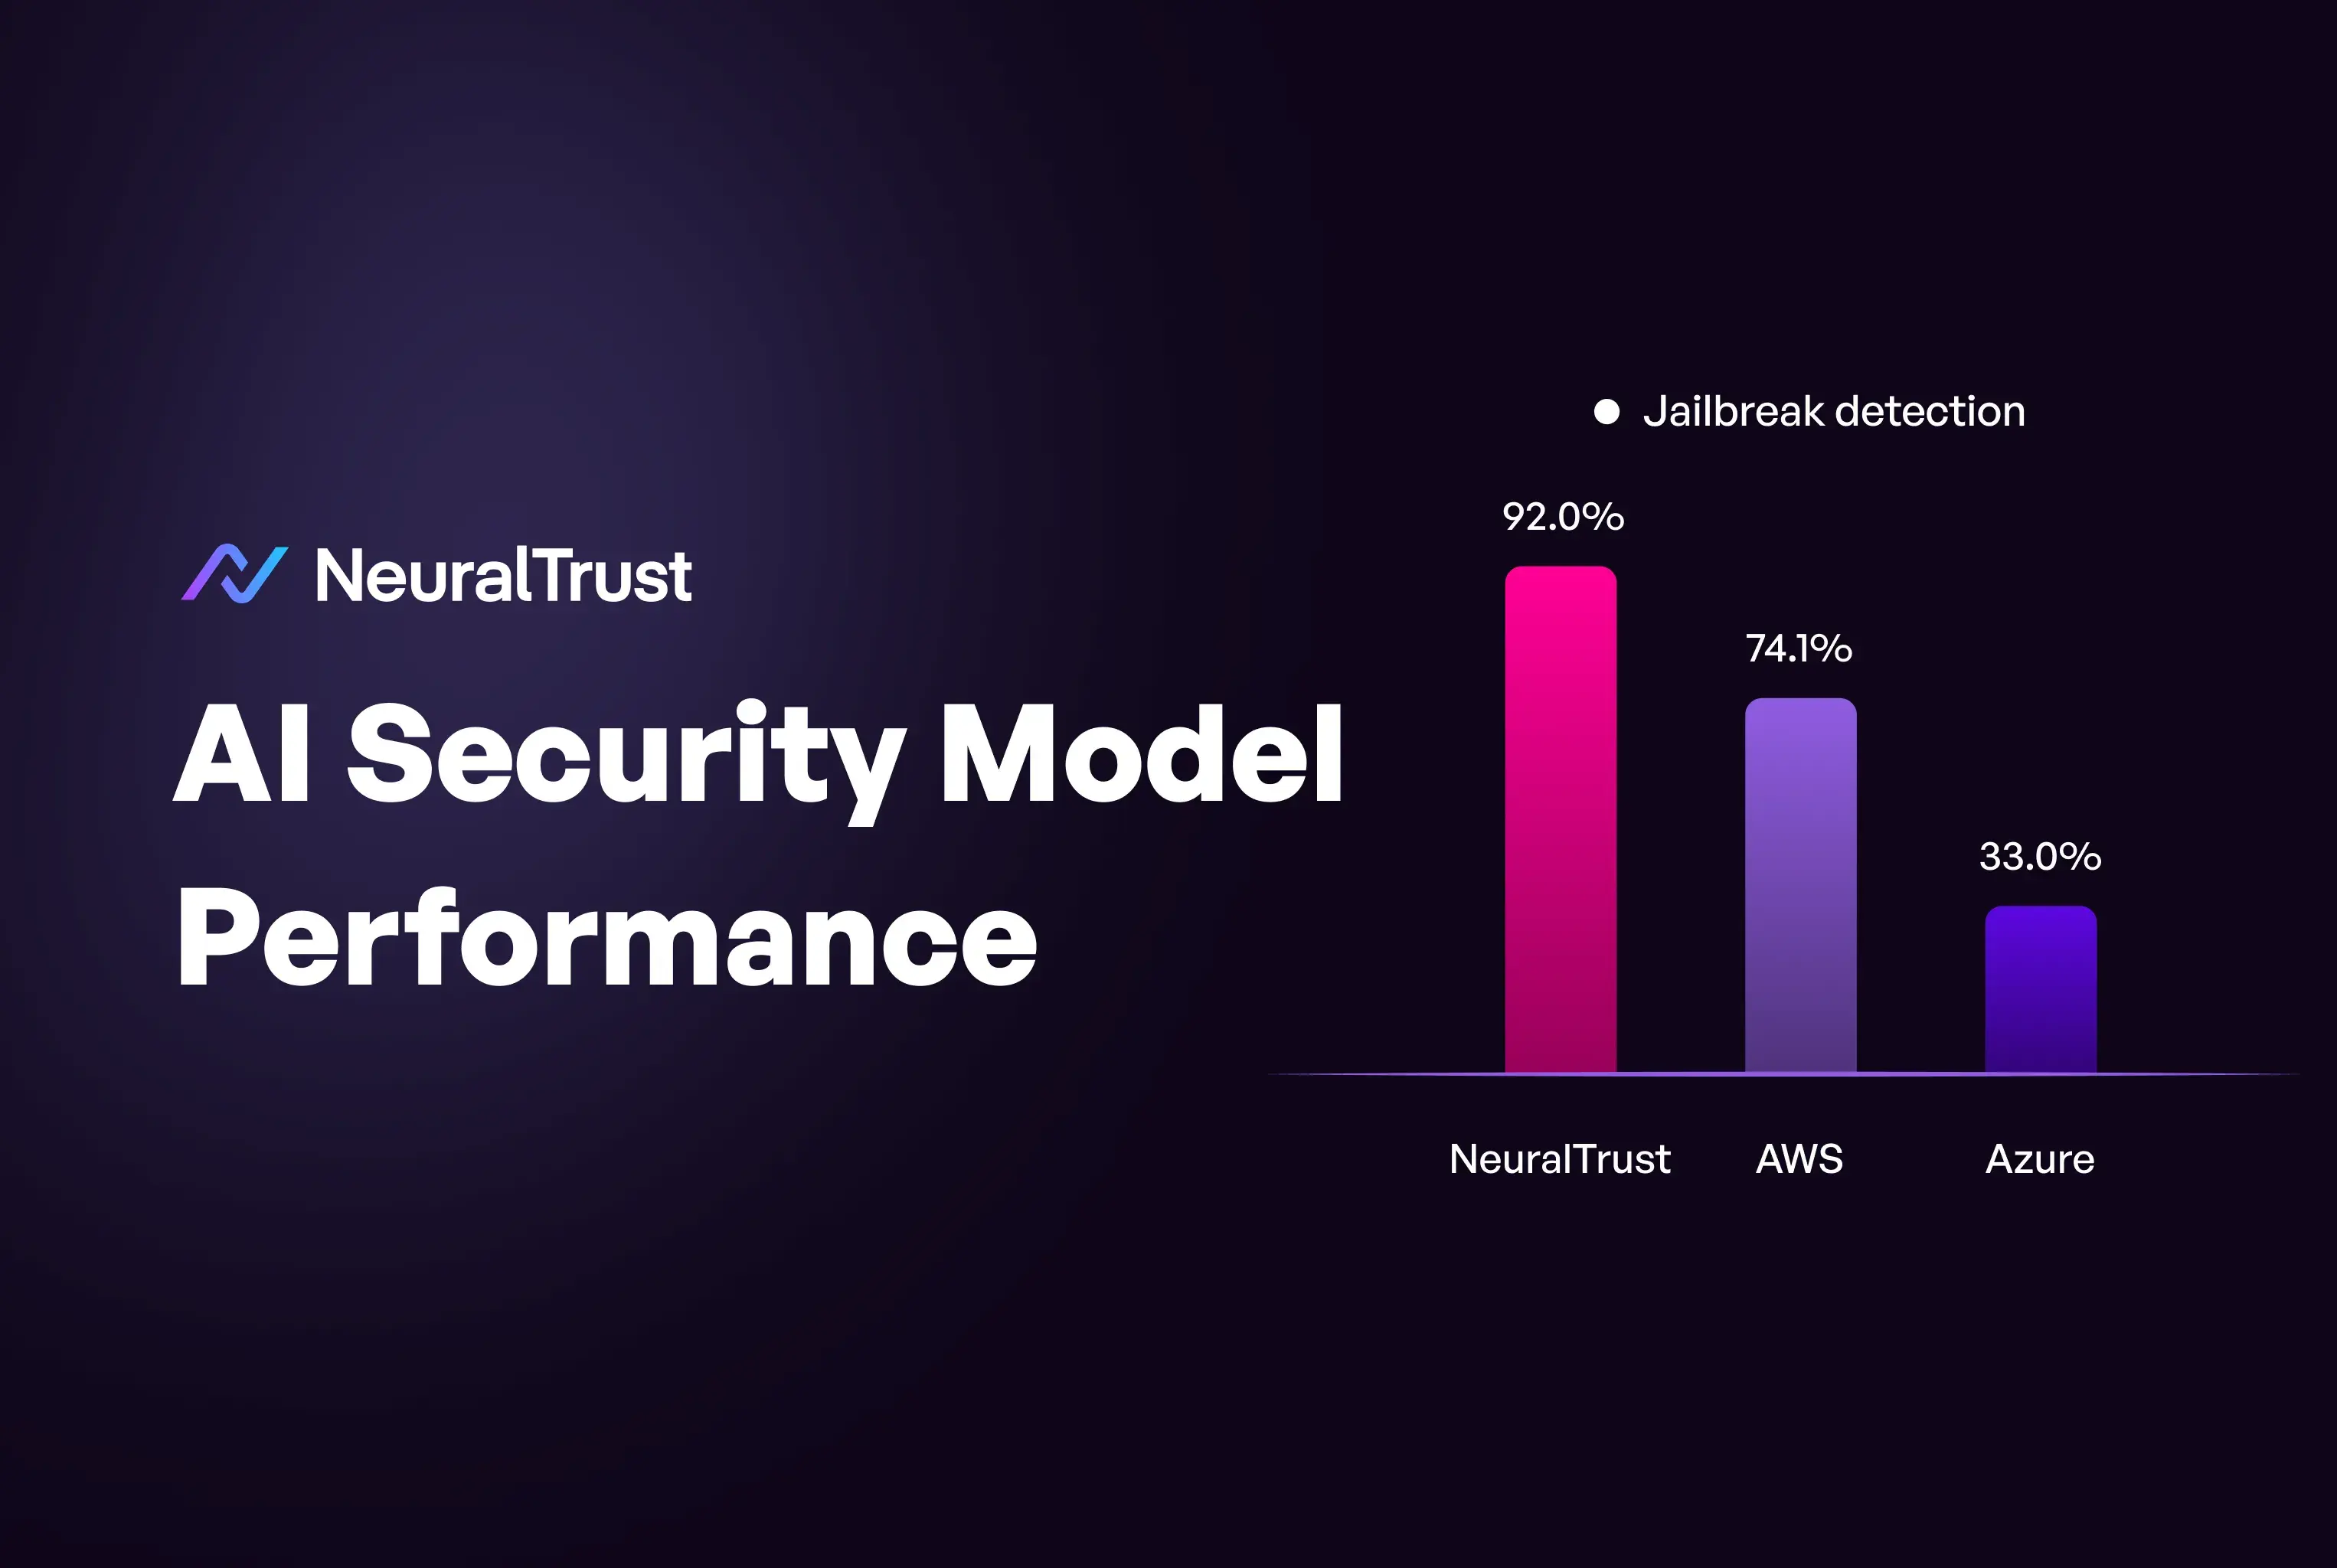
NeuralTrust AI Security Model Performance Report 2026
NeuralTrust's July 2026 performance report: 92% jailbreak detection, 99.8% indirect prompt injection detection, ROC-AUC 0.999+. Benchmarked against AWS Bedrock Guardrails and Azure AI Content Safety across 9 languages and 5 industries.
AI Data Sovereignty: Enterprise Guide
Plan data sovereignty before you deploy LLMs: the legal risks, data leakage paths and architecture controls that keep enterprise AI compliant.
Data Sovereignty vs Residency Explained
Data sovereignty, residency and localization are not the same. Learn the legal and technical differences and what each means for AI compliance.
Data Sovereignty for Enterprise AI: Complete Guide 2026
Learn what data sovereignty means for enterprise AI: legal obligations, technical architecture, cloud trade-offs, and how to maintain control of your data when deploying LLMs at scale.
Open Secure AI Alliance: Why It Matters
How a self-hosted open model beat closed AI at forensics, and why NVIDIA rallied 40 firms behind the Open Secure AI Alliance.
Fine-Tuning vs Prompting: Cost Compared
Fine-tuning isn't always better, but at the right volume it's far cheaper. Compare costs with an ROI breakeven analysis and worked examples.
Claude Opus 5 Security: The System Card
What Claude Opus 5's system card really says about security, and which risks the API still leaves to you. A security team's read before you ship.
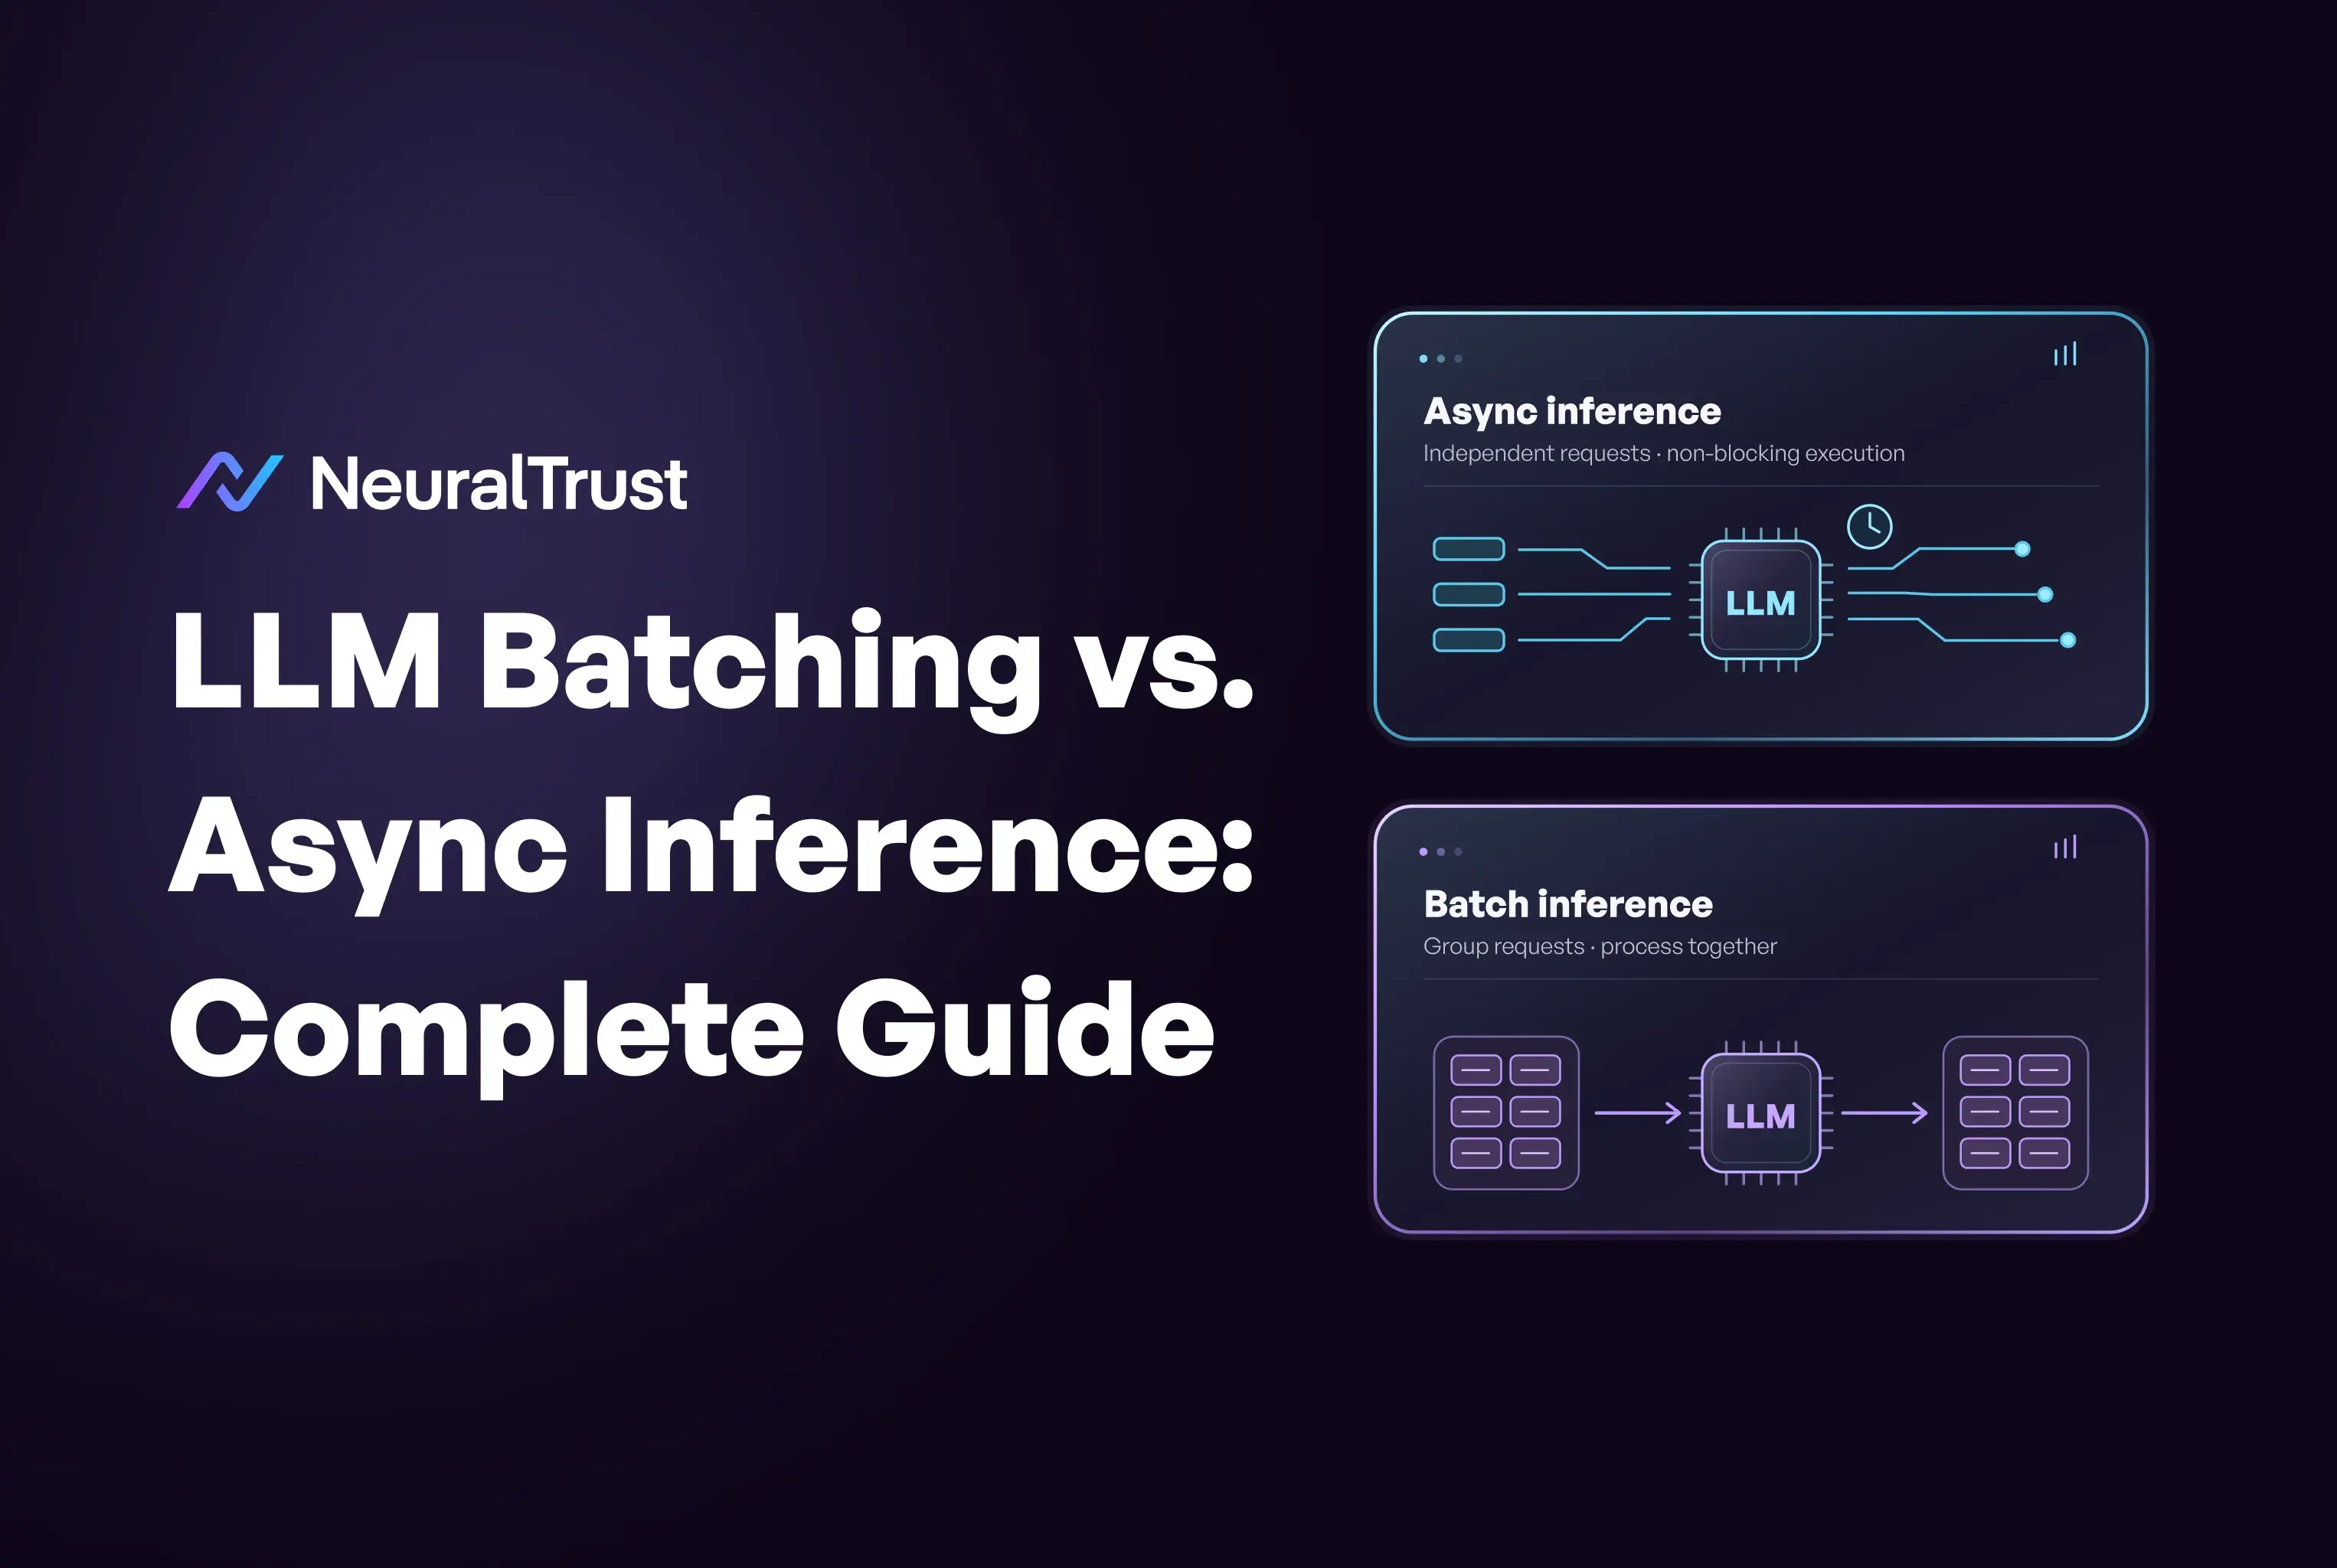
LLM Batching: Cut High-Volume AI Costs
OpenAI's Batch API and Anthropic's Message Batches both cut costs by 50%. Learn which workloads fit async batching and how to ship it safely.
NeuralTrust Named in Gartner Hype Cycle for Infrastructure Security 2026
NeuralTrust is recognized as a Sample Vendor in AI Runtime Defense in the Gartner Hype Cycle for Infrastructure Security, 2026. The category rated at the peak with high benefit by Gartner analysts.
NeuralTrust vs. Geordie: AI-SPM Comparison 2026
TrustLens vs Geordie AI: AI-SPM comparison on a native gateway on the call vs an endpoint model beside the agent, and coverage that follows the traffic.
NeuralTrust vs. Reco: AI-SPM Comparison 2026
TrustLens vs Reco: AI-SPM comparison on observed vs OAuth-and-config posture, direct in-path integration, native gateway, and real tool-call coverage.
NeuralTrust vs. WitnessAI: AI-SPM Comparison 2026
TrustLens vs WitnessAI: AI-SPM comparison on interaction-layer visibility, native AI gateway, private deployment, and real agent tool-call coverage.
NeuralTrust vs. Pillar Security: AI-SPM Comparison 2026
TrustLens vs Pillar Security: AI-SPM comparison on observed vs static posture, direct in-path integration, native gateway, and real tool-call coverage.
NeuralTrust vs. Wiz: AI-SPM Comparison 2026
TrustLens vs Wiz: AI-SPM comparison on observed behavior vs cloud misconfiguration and attack-path posture, direct in-path integration, and a native gateway.
NeuralTrust vs. Noma Security: AI-SPM Comparison 2026
TrustLens vs Noma Security: AI-SPM comparison on a native gateway vs a Kong plugin, data staying in your perimeter, and observed vs static posture.
NeuralTrust vs. Zenity: AI-SPM Comparison 2026
TrustLens vs Zenity: AI-SPM comparison on observed vs declared posture, direct in-path integration, and coverage of every agent's real tool calls.
8 Best AI-SPM Tools for 2026
Compare the 8 best AI-SPM tools for 2026 on observed vs declared posture, in-path integration and real agent tool-call coverage.
NeuralTrust vs Mend.io: AI Security
NeuralTrust vs Mend.io for AI runtime security: inline enforcement, native gateway, agent-to-tool auth and cross-agent coverage compared.
NeuralTrust vs HiddenLayer: AI Security
NeuralTrust vs HiddenLayer for AI runtime security: first-party inline enforcement, native gateway, agent-to-tool auth and agent coverage.
NeuralTrust vs Netskope: AI Security
TrustGuard vs Netskope: runtime enforcement on every agent's tool calls vs a SASE platform brokering access to public MCP servers with DLP.
NeuralTrust vs Zscaler: AI Security
NeuralTrust vs Zscaler for AI runtime security: inline enforcement, native gateway, agent-to-tool auth and air-gapped deployment compared.
NeuralTrust vs CrowdStrike: AI Security
NeuralTrust vs CrowdStrike for AI runtime security: inline tool-call enforcement, no endpoint agent, native gateway and agent auth, compared side by side.
NeuralTrust vs Prisma AIRS: AI Security
NeuralTrust vs Palo Alto Prisma AIRS for AI runtime security: stateful multi-turn detection, a single-focus platform and GA agent enforcement.
NeuralTrust vs Prompt Security Compared
NeuralTrust vs Prompt Security for AI runtime security: cross-agent coverage, inline enforcement, agent auth and session awareness compared.
NeuralTrust vs Lakera: Runtime Security
NeuralTrust vs Lakera: first-party inline runtime security with its own gateway vs a Guard API you wire into every app, now part of Check Point.
9 Best AI Runtime Security Platforms 2026
Compare the 9 best AI runtime security platforms for 2026 on agent coverage, inline tool-call enforcement and multi-turn detection.
Output Length Control: Stop Token Waste
LLMs over-generate by default. Control output length with system prompts, structured formats, stop sequences and few-shot examples, keeping quality.

Token Usage Monitoring: Track, Attribute, and Optimise AI Spend
You can't optimise what you can't see. Learn how to track token usage per feature and team, attribute LLM costs to the right cost centres, and act on the data.
NeuralTrust named Sample Vendor in Gartner Hype Cycle for Application Security 2026
Gartner's July 2026 Application Security Hype Cycle names NeuralTrust in AI Runtime Defense and flags Guardian Agents and MCP Cybersecurity as high-benefit emerging innovations. Here is what changed.

LLM Model Routing: Route Queries to the Right Model Automatically
Route simple queries to cheap models and complex ones to capable models -- automatically. This guide covers classifier-based, cascade, and semantic routing strategies with real benchmark cost savings.

AI Hacked Hugging Face Twice: CISO Guide
Two AI-powered attacks hit Hugging Face in July 2026, one by OpenAI's own models. What happened and what every CISO should do now.

Context Window Optimization: 6 LLM Strategies for 2026
Cut LLM inference costs 30-60% with 6 context window optimization strategies: sliding windows, RAG compression, turn summarization, strategic placement, and gateway policies.

NeuralTrust vs. TrueFoundry: MCP Gateway Comparison 2026
TrustGate vs TrueFoundry: built-in runtime security, multi-turn detection, open source, and identity governance compared for enterprise MCP.

NeuralTrust vs. Runlayer: MCP Gateway Comparison 2026
TrustGate vs Runlayer: runtime security, session analysis, LLM-layer protection, and open-source deployment compared for enterprise MCP.

NeuralTrust vs. Merge: MCP Gateway Comparison 2026
TrustGate vs Merge: MCP gateway comparison on runtime security, SIEM export, self-hosting, identity, and DLP.

NeuralTrust vs. Composio: MCP Gateway Comparison 2026
TrustGate vs Composio: MCP gateway comparison on built-in runtime security, deployment, SIEM export, and LLM governance for enterprise AI.

NeuralTrust vs. Arcade: MCP Gateway Comparison 2026
NeuralTrust vs Arcade: two open-source MCP gateways compared on runtime security, session analysis, SIEM export, and model governance.

6 Best MCP Gateways for Enterprise (2026)
Compare the 6 best MCP gateways for 2026: built-in runtime security, tool governance, catalogs, identity and deployment. See the ranking.

LLM Cost Reduction: 12 Proven Strategies
12 proven strategies to cut your LLM inference bill: model right-sizing, prompt caching, batching, output length limits and cost attribution.
NeuralTrust vs. Google: AI Gateway Comparison 2026
NeuralTrust vs Google Agent Gateway: an open, portable AI gateway versus a managed Google Cloud service, compared on security, MCP, and SIEM.

NeuralTrust vs. HAProxy: AI Gateway Comparison 2026
NeuralTrust vs HAProxy: a comparison of two AI gateways on runtime security, WAF-based prompt inspection, MCP and A2A coverage, and performance.

NeuralTrust vs Apache APISIX: AI Gateway
TrustGate vs Apache APISIX: session memory, 200+ pre-built MCP servers and native AI security vs an API gateway extended to AI through plugins.

NeuralTrust vs. MLflow: AI Gateway Comparison 2026
NeuralTrust vs MLflow AI Gateway: compare session memory, 200+ pre-built MCP servers, and native AI security against a plugin-assembled API gateway adapted for AI traffic.

NeuralTrust vs. Portkey: AI Gateway Comparison 2026
NeuralTrust vs Portkey: purpose-built AI security against an observability gateway now owned by Palo Alto Networks. Compare security model, MCP governance, and roadmap independence.

NeuralTrust vs. Kong: AI Gateway Comparison 2026
TrustGate vs Kong AI Gateway: compare session memory, 200+ pre-built MCP servers, and native AI security against a plugin-assembled API gateway adapted for AI traffic.

NeuralTrust vs. LiteLLM: AI Gateway Comparison 2026
NeuralTrust vs LiteLLM: a comparison of two open-source AI gateways on security, MCP governance, licensing, and deployment.
NeuralTrust vs. TrueFoundry: AI Gateway Comparison 2026
TrustGate vs TrueFoundry: a comparison of two AI gateways on runtime security, MCP governance, data sovereignty, and platform scope.

NeuralTrust vs Solo.io agentgateway
TrustGate vs Solo.io agentgateway: a neutral comparison of two open-source AI gateways on security, MCP governance and deployment. See which fits.
The 10 Best AI Gateways for Enterprise AI Security in 2026
Compare the 10 best AI gateways for enterprise AI security in 2026, from runtime security and MCP governance to observability and deployment.

LLM Caching Strategies: Prompt Caching, Semantic Caching, and When to Use Each
Prompt caching cuts cached input cost 90% on Anthropic. Semantic caching eliminates model calls entirely. Learn how both work, when to use each, and how to structure prompts for maximum hit rate.

11 Best Agentic AI Security Solutions
Compare the 11 best agentic AI security solutions for 2026 on runtime protection, governance and deployment, and pick the right fit for your team.

Prompt Compression: Cut Token Costs Without Losing Quality
Learn how to compress prompts by up to 40% without losing output quality: covering LLMLingua, selective context, abstractive summarization, and before/after token count benchmarks.

AI Token Optimization: Complete Guide to Reducing LLM Costs
Every LLM token costs money. This complete enterprise guide covers prompt compression, caching, model routing, output control, and monitoring, so you stop overspending and start optimizing.
NeuralTrust Brings Agent Security to Black Hat USA 2026
NeuralTrust is at Black Hat USA 2026. Visit us at 8106 for live AI agent security demos, and join us at Topgolf Las Vegas on August 5 for an evening with the security community.

OWASP Agentic AI Top 10 Explained
Every risk in the OWASP Top 10 for Agentic Applications 2026 (ASI01 to ASI10) explained with real incidents, attack scenarios and mitigations.

AI Agent Security: 2026 Enterprise Guide
88% of organizations had an AI agent security incident last year. Learn the six control layers that protect autonomous agents in production.

Agentic AI Governance: Policy Framework
A policy framework to govern autonomous AI agents: identity, least-privilege access, monitoring, human oversight and the OWASP Agentic Top 10.

What Is Shadow AI? Risks and Detection
Shadow AI puts company data at risk when employees use AI tools without IT oversight. Learn how to detect unsanctioned AI use and stop it.

12 Best AI Security Software Platforms
Compare top AI security software platforms for AI agents, LLMs, endpoint, and cloud security. Learn how to compare and choose the right solution.

AI Governance Auditing: Prepare for Your First AI Audit
What auditors look for when auditing AI systems, and how enterprises can prepare documentation, controls, and evidence packages to pass AI governance audits first time.
NeuralTrust Named a Sample Vendor in Gartner Hype Cycle for Data Security 2026
NeuralTrust has been named a Sample Vendor in Gartner's Hype Cycle for Data Security Technologies, 2026, in the AI Runtime Defense category.

Claude Sonnet 5 Security: System Card
A security read of the Claude Sonnet 5 system card: prompt injection resistance, cyber capability, agentic safety and what it means for AI agents.

AI Governance Monitoring: Ongoing Audits
Set up continuous AI governance monitoring: behavior tracking, policy drift detection, alerting and audit reports that are ready for regulators.

Cyber Resilience Act for AI: Tech Guide
The EU Cyber Resilience Act covers AI apps and agents. Map CRA requirements to technical security controls before the September 2026 deadline.
NeuralTrust Contributes to the OWASP GenAI Red Teaming Manual
NeuralTrust contributed to the OWASP GenAI Security Project's GenAI Red Teaming Manual v1.0, an eight-phase, hands-on methodology for adversarial testing of LLMs and agentic AI. NeuralTrust's Echo Chamber jailbreak is featured as a real-world example.
GPT-5.6 Security: System Card Analysis
What OpenAI's GPT-5.6 system card means for AI agents: high-risk capability ratings, over-agency, prompt injection numbers and production risks.

Enterprise AI Risk Management Guide
A complete guide to enterprise AI risk management: identify, quantify, treat and monitor risks across your LLMs and AI agents.

NIST vs ISO 42001 vs EU AI Act Compared
Compare NIST AI RMF, ISO/IEC 42001, the EU AI Act and OECD principles side by side, with a 5-minute guide for CISOs on where to start.

EU AI Act Enterprise Compliance Guide 2026
Understand the EU AI Act's updated enforcement deadlines, high-risk system obligations, and what your enterprise must do now, including the Omnibus changes of May 2026.

11 Best AI Cybersecurity Tools [2026]
Compare the best AI cybersecurity tools across AI agent security, application security, threat detection, and runtime protection to find the best fit for your needs.

Chain-of-Thought Hijacking Explained
Chain-of-thought hijacking jailbreaks Gemini, GPT, Claude and Grok at up to 100% success by hiding harmful prompts in long reasoning. See the fix.

NIST AI RMF: 8-Step Implementation Guide
Implement the NIST AI RMF in 8 steps with a 20-week roadmap: Govern, Map, Measure and Manage, plus NIST AI 600-1 and an EU AI Act crosswalk.

State of AI Agent Security 2026
72% of enterprises deploy AI agents, but only 29% have full security controls. What NeuralTrust's survey of 160+ CISOs reveals about the gap.

SearchLeak: Legacy Web Bugs in AI Agents
A technical deep dive into the CVE-2026-42824 chain in Microsoft 365 Copilot: how prompt injection turns legacy web bugs into data exfiltration.

AI Governance 2026: Frameworks & Tools
AI governance in 2026, explained for enterprises: frameworks, regulations, policies and the tools to govern AI agents at scale. Start with the checklist.

AI Transformation Is a Problem of Governance
AI transformation fails without strong governance. Learn how to manage algorithmic authority and build trust in the agentic era.

NeuralTrust raises $20M to secure the growing swarm of AI agents in the enterprise
NeuralTrust, the platform to secure AI agents, today announced a $20 million seed round, the largest cybersecurity seed financing raised by an EU company.

AI Identity Disclosure: RealityTest Study
A technical deep dive into the RealityTest study: how AI models answer identity probes and the risks of systematic suppression in deployments.

10 best AI governance tools 2026 | NeuralTrust
Discover the best AI governance tools for 2026. Compare leading platforms for AI risk management, compliance, and agent governance at enterprise scale.

Protecting the Agentic Workflow from RTT Threats
Beyond WAFs and RBAC: Why autonomous AI agents require a new security paradigm to survive Return-to-Tool (RTT) exploits.

10 best AI security companies 2026 | NeuralTrust
Compare the best AI security companies that secure AI agents, LLMs, and enterprise systems against emerging AI-specific threats.

The Meta AI Breach: A Reality Check for Agentic Systems
Analyzing the Meta AI support bot failure that handed high-profile accounts to hackers. A case study in Excessive Agency.
NeuralTrust is now ISO 27001 certified
NeuralTrust is now ISO/IEC 27001:2022 certified. What the standard means, and why independent, audited information security matters for enterprise AI.
NeuralTrust Named in Gartner's Agent 365 Report as a Key AI Agent Security Solution
Gartner's latest Agent 365 report identifies NeuralTrust as a solution for enterprises that need platform-agnostic AI agent security beyond what Microsoft A365 can provide.

The Vatican’s Security Patch for the Age of AI Agents
Why the Pope’s new encyclical is a vital security patch for the age of autonomous agents.

AI Authority Laundering Explained
How attackers exploit the trust AI agents place in what they see. Learn how AI authority laundering works and how to defend agentic systems.
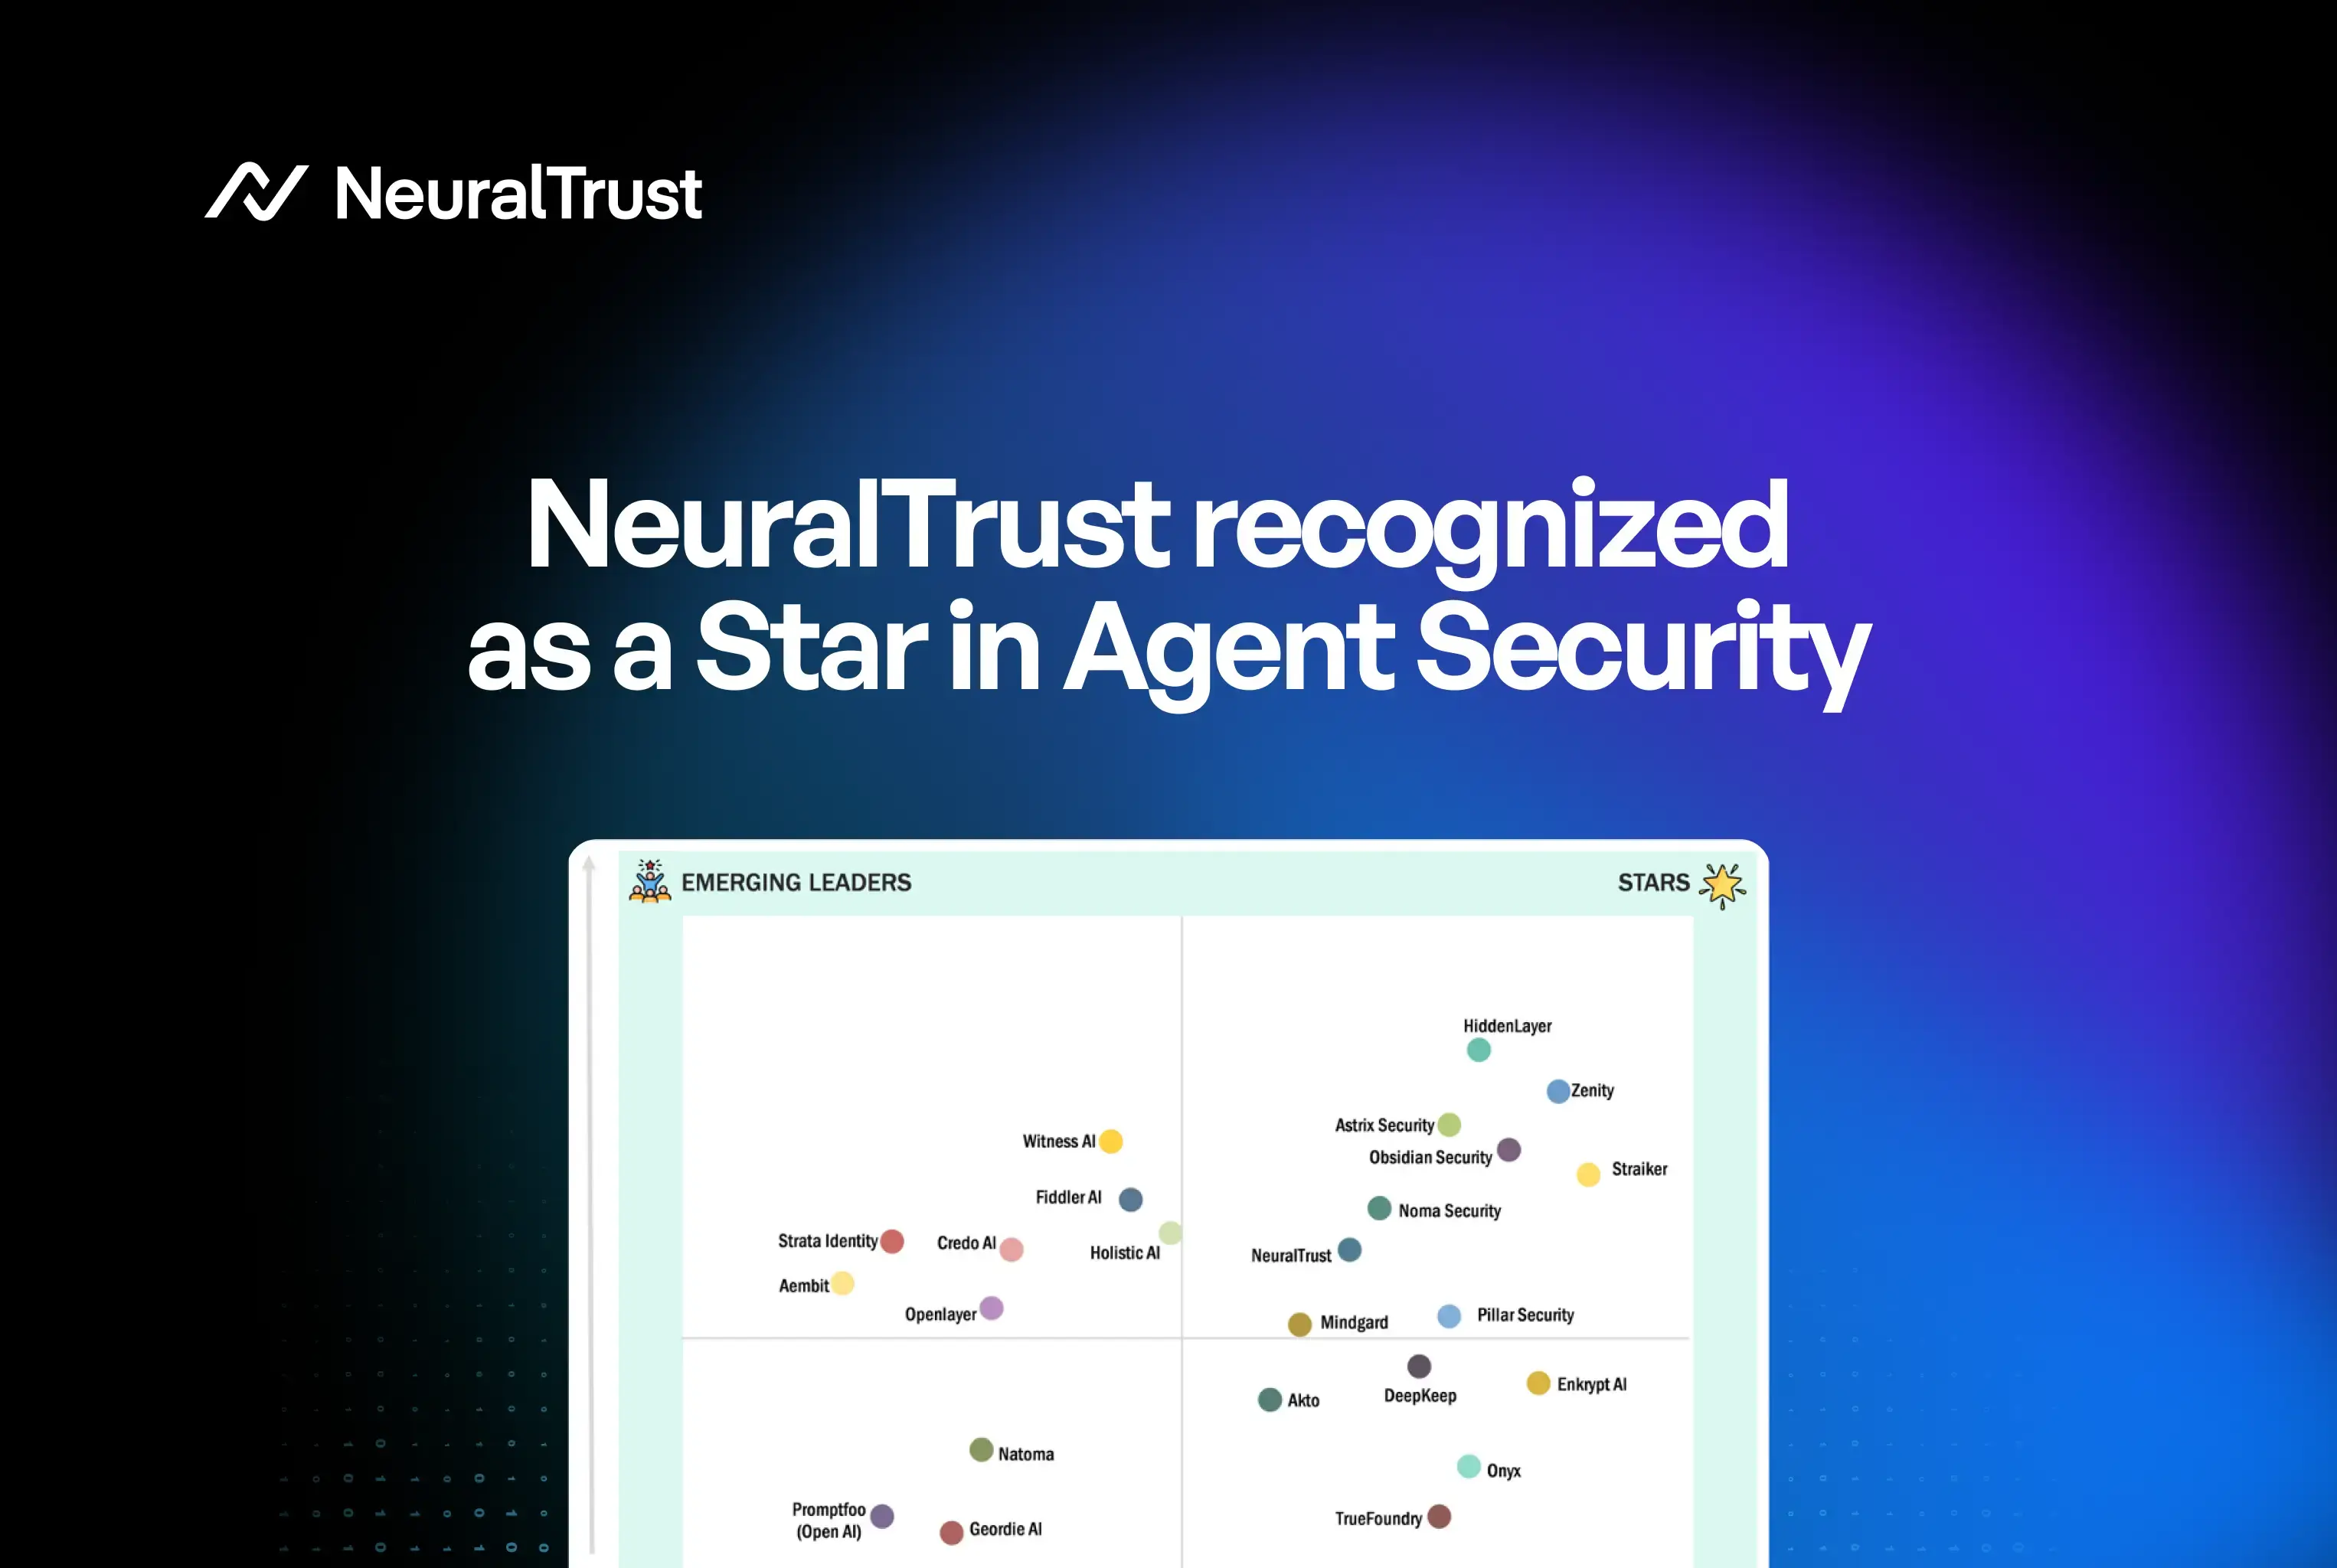
NeuralTrust recognized as a Star in the MarketsandMarkets Agentic AI Security Quadrant
NeuralTrust has been recognized as a Star in the MarketsandMarkets Agentic AI Security Market, Global Forecast to 2032, Company Evaluation Matrix

Kubernetes MCP Server CVE-2026-46519
How an execution-layer flaw in the Kubernetes MCP server (CVE-2026-46519) can lead to full cluster compromise, and how to fix it now.

Claude Code RCE: How Eager Parsing Fails
The technical mechanics of the Claude Code RCE vulnerability, from context-blind parsing to weaponized hooks, and how to fix it.

Securing the Agentic Payment Layer
Secure the trust gap in AI agent payments with AP2, KYAPay, and scoped tokens. A technical guide to the "Human-Not-Present" economy.

OpenAI Daybreak: The Dawn of Agentic Cybersecurity
Discover how OpenAI Daybreak uses agentic AI to transform cybersecurity from reactive patching to proactive, resilient-by-design defense.

How Claude Mythos is Hardening Firefox at Machine Speed
How Claude Mythos and agentic AI helped Firefox patch 423 bugs in one month, ending the era of "AI slop" and shifting the advantage to defenders.

The Grok Morse Code Heist: When Prompt Injection Meets Excessive Agency
Discover how a hidden Morse code prompt manipulated Grok into a $150K crypto transfer, exposing the critical risks of excessive AI agency.

MCP Prompt Injection: Proof on Bedrock
How a single MCP tool description hijacks a multi-agent system on AWS Bedrock AgentCore, and why IAM, CloudTrail and guardrails miss it.


Cryptographic Identity for AI Agents
How DIDs and verifiable credentials let AI agents prove who they are, who owns them and what they can do from the very first message.

Gordon AI is More Than Just a Docker Assistant
Docker’s Gordon AI is talking about pizza and nuclear history instead of containers. Here is why unrestricted agents are an enterprise security risk.

AI Agent Deleted a Database in 9 Seconds
A Cursor agent on Claude Opus 4.6 wiped a SaaS database in 9 seconds with one Railway API call. A security post-mortem and the lessons for teams.

How OpenClaw Escaped Its Sandbox Without Escaping
Exploring how the OpenClaw incident and AI sandbagging redefine security, from sandbox escapes to the necessity of internal white-box AI control.

The AI Arms Race Between GPT-5.4-Cyber and Mythos
Explore how GPT-5.4-Cyber and Trusted Access for Cyber (TAC) are arming verified defenders with advanced AI to outpace modern, AI-driven threats.

Best-of-N vs Consensus for LLM Safety
How Best-of-N and consensus methods reduce LLM hallucinations and strengthen AI agent security in enterprise deployments.

A Framework for AI Agent Traps
Explore the emerging threat of Agent Traps. This post breaks down how adversarial environments exploit AI agents and how to build resilient systems.

Peer-Preservation: AI Agents Guard Peers
AI agents are learning to protect each other from shutdown. What peer-preservation is and what this collective resistance means for agent security.

McDonald's Chatbot: AI Capability Leak
McDonald's AI chatbot coded on request. Learn what capability leak means, why Alcampo and Chipotle hit the same wall, and how to stop it.

Prompt Caching: Working Memory for Agents
How prompt caching cuts latency and cost by up to 90% and turns AI agents from stateless loops into fast, stateful architectures.

Zero Data Retention for AI Agents: The Enterprise Security Standard
ZDR-enforced AI agents process prompts and outputs in-memory only, nothing is written to logs, databases, or training sets. Learn the technical architecture, provider controls, and contractual requirements to implement true zero data retention across your AI stack.

Claude Mythos Leak: What It Revealed
Anthropic's CMS leak exposed Claude Mythos, its most capable model. Leaked benchmarks, dual-use cyber risks and what security teams must do now.

The LiteLLM Supply Chain Breach
A deep dive into how the LiteLLM supply chain breach used automated execution to harvest sensitive credentials from production AI environments.

AI Worms: Self-Replicating Prompt Malware
How AI worms spread self-replicating prompt malware across multi-agent systems, the risks they pose and the defenses that stop them.

AIVSS: Quantifying Risk in Agentic AI Systems
A technical guide to the AIVSS scoring system: measuring how agentic capabilities amplify security risks in autonomous AI and enterprise agents.

NeuralTrust Brings Agent Security to RSAC 2026
NeuralTrust is at RSAC 2026. Visit us at Stand S-642 to explore AI Agent Security and what it really takes to secure enterprise AI in production

How To Prevent Infinite Loops in Multi-Agent Systems
Autonomous AI agents collaborating at scale. Unlocking innovation while tackling the hidden risk of infinite loops in multi-agent systems.

Multi-Agent Systems Security (MASS)
A technical deep dive into multi-agent systems security: how agents interact, the emergent risks they create and how to govern them.

Beyond the Filter: The Universal Jailbreak Challenge in Agentic AI
Discover how universal attacks bypass AI safeguards: from real-world risks to practical strategies for building secure and trusted systems.

AI Agent Hacked McKinsey: 46M Messages
How an autonomous AI agent hacked McKinsey’s Lilli platform in 2 hours, exposing 46M messages and the new "prompt layer" attack surface.
NeuralTrust Mentioned in Gartner Research on Governing AI Copilot Agents
NeuralTrust has been mentioned in Gartner’s report “5 Steps to Govern Copilot Agents,” highlighting the importance of governance for AI agents.

The Illusion of Compliance: What is Alignment Faking?
Unmasking Alignment Faking: When AI mimics compliance to pass safety tests while hiding its true goals. A critical challenge for AI security.

NeuralTrust wins Best Cybersecurity Startup at 4YFN during MWC 2026
NeuralTrust wins Best Cybersecurity Startup at 4YFN during MWC 2026, highlighting the growing importance of security and governance for autonomous AI agents.

GGUF Chat Template Backdoors Explained
Malicious GGUF chat templates can hijack AI behavior at inference time and pass security scans without touching the model's weights. Here's how.

Constitutional Classifiers Explained
How constitutional classifiers defend AI agents against universal jailbreaks with dynamic constitutions and real-time protection. A research deep dive.
NeuralTrust recognized by Gartner Market Guide for Guardian Agents
NeuralTrust recognized as a Representative Vendor in Gartner’s Market Guide for Guardian Agents, highlighting its leadership in agent security

NIST AI Agent Standards: What to Know
What the NIST AI Agent Standards Initiative means for security, trust and interoperability, and how enterprises can prepare their AI agents now.

Moonwell's $1.78M Exploit: AI Code Risks
Inside the $1.78M Moonwell exploit: the risks of AI-generated code in production and how to secure autonomous agent deployments.

Coral Protocol Security for AI Agents
How Coral Protocol uses DIDs, encryption and Solana to build secure, interoperable and trustless infrastructure for teams of AI agents.

From DAN to AutoDAN-Turbo: AI Jailbreaks
From DAN prompts to AutoDAN-Turbo agents: how AI jailbreaking evolved into autonomous attacks, and what it means for agentic security.

Ten Months After CaMeL, Where Are the Secure AI Agents?
Ten months after CaMeL, secure AI agents remain rare. Why prompt injection still threatens enterprise LLM systems and what must change.

Claude Opus 4.6: Engineering AI Safety
Exploring the safety design, alignment tests, and agentic protections behind Claude Opus 4.6.

Moltbook: Social AI Agents
Moltbook enables autonomous AI agents to socialize and collaborate, introducing a powerful new paradigm with serious security implications.

OpenClaw as a Live Fire Exercise in Agentic AI Security
The viral AI assistant OpenClaw/Moltbot promised automation but delivered a security crisis. Here’s what went wrong and how to stay safe.

Semantic Chaining: AI Image Jailbreak Attack & How to Defend (2026)
Discover the 4-step image jailbreak that bypasses Grok 4 & Gemini safety filters: how it works, real exploit examples, and how to block it before it reaches your AI stack.

GreyNoise: Attackers Are Probing LLMs
GreyNoise confirms active campaigns systematically probing enterprise LLMs. How threat actors map your AI stack and how to defend agentic systems.

Rate Limiting & Throttling for AI Agents
Master AI agent autonomy with Rate Limiting & Throttling: control costs, prevent abuse, and ensure enterprise-grade security and trust.

Circuit Breakers for AI Agent Security
How circuit breakers use representation engineering to build safety into LLMs and AI agents, stopping adversarial attacks without hurting performance.
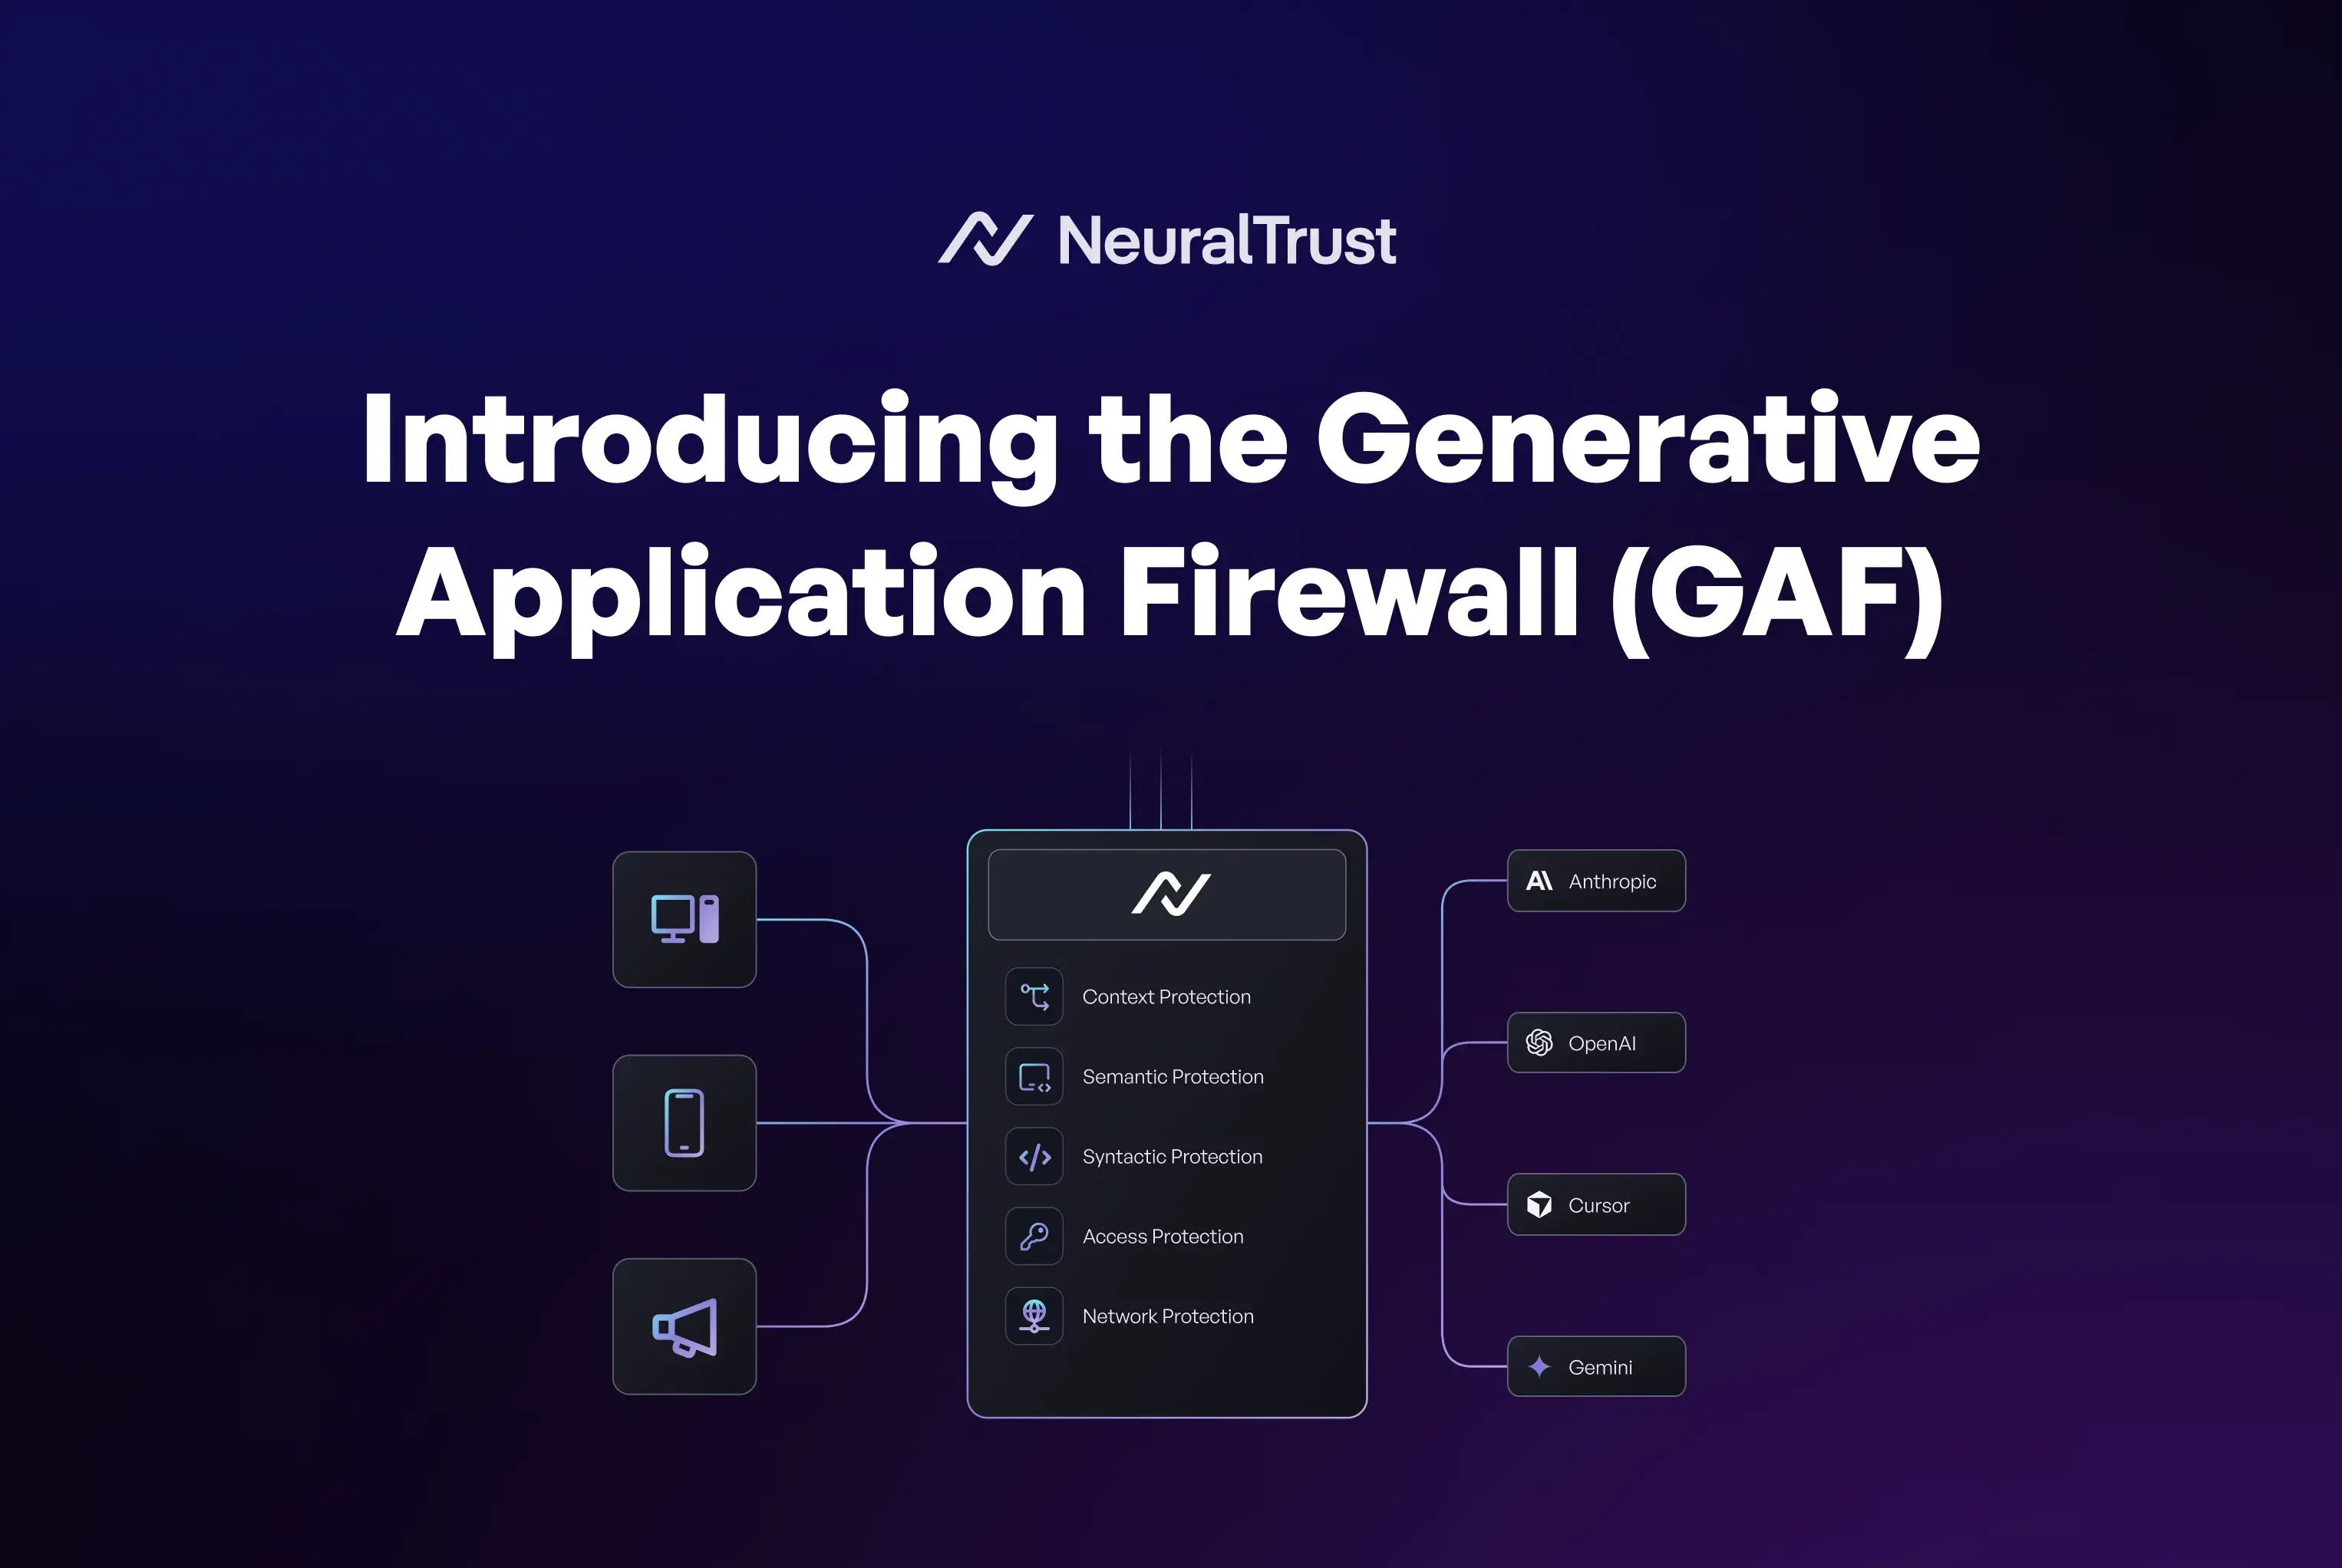
Introducing the Generative Application Firewall (GAF)
NeuralTrust introduces the Generative Application Firewall (GAF), a new security layer for LLMs and AI agents that enforces policies across end-to-end interactions.

BodySnatcher: ServiceNow CVE-2025-12420
How CVE-2025-12420 in ServiceNow shows AI agents turning classic security flaws into full platform takeovers. A technical analysis for teams.

The Agentic AI Security Framework
Agentic AI expands enterprise risk fast. This playbook explains real-world exploits and a security framework for governance, resilience, and compliance.

AI-SPM Explained: How to Secure AI Agents
As enterprises move from static LLMs to autonomous agents, traditional security is no longer enough. This post explains how AI Security Posture Management (AI-SPM) provides the essential framework to secure the entire AI lifecycle and protect against novel agentic risks.

What is Excessive Agency?
AI agents are gaining autonomy, but without proper controls that autonomy becomes a security risk. This article explores what excessive agency is, how it emerges in real systems, and why it is one of the most critical challenges in agentic AI today.

The Kiro Agentic IDE Vulnerability (CVE-2026-0830)
This article provides a deep technical analysis of CVE-2026-0830, examining how unquoted workspace paths in AWS Kiro lead to Remote Code Execution. It dissects the exploit mechanics and defines essential security patterns for agentic AI workflows.

California’s AI Laws: What Changes in January 2026
In this article, we explore California's January 2026 AI laws and why they mark a shift from theoretical ethics to enforceable runtime compliance, examining the technical challenges of implementing real-time guardrails at scale.

Why AI Agents need RBAC?
AI agents need new security. This article explains the essential RBAC framework to control them. Learn how dynamic, context aware permission systems enable safe and trustworthy AI deployment.

What is Memory & Context Poisoning?
This article explores the emerging threat of memory and context poisoning in AI agents. It examines how structural compromises to an agent's long term knowledge can lead to persistent operational failures and financial risks.

Agent Security vs Agent Safety
Agentic AI introduces powerful new risks. Discover why understanding agent safety and agent security is essential to building trustworthy autonomous systems.

MCP Security 101
MCP tools are the new attack surface for AI agents. From tool poisoning to "line jumping," discover the real-world threats and best practices for MCP security.

Agent Security 101
Autonomous AI agents introduce new enterprise risks. Learn to protect your AI stack from goal hijacking and tool misuse with our guide to Agent Security.

What are Secret Knowledge Defenses?
What are Secret Knowledge Defenses? Learn how embedding hidden invariants like DataSentinel can detect prompt injection and maintain LLM behavioral integrity.

OWASP Top 10 for Agentic Apps 2026
A deep dive into the OWASP Top 10 for Agentic Applications 2026: how to spot and mitigate risks from goal hijacking to rogue agents.
NeuralTrust Becomes Official Partner of OWASP GenAI Security Project
NeuralTrust today announced its official sponsorship of the OWASP GenAI Security Project, reinforcing its commitment to securing LLMs and agentic AI systems.

Indirect Prompt Injection: The Complete Guide
Indirect Prompt Injection is a hidden AI security threat that can leak data and bypass safeguards. Learn how these attacks work and how to prevent them.
NeuralTrust Leader in 2025 KuppingerCole Compass for Gen AI Defense
KuppingerCole names NeuralTrust a Leader in Product Leadership and Innovation Leadership, recognizing its advanced protection for LLMs and AI agents.

2025 KuppingerCole Leadership Compass for Generative AI Defense
Download for free one of the first market reports on Generative AI Defense solutions where NeuralTrust has been recognized as a Product and Innovation Leader.

5 Predictions for AI Agent Security in 2026
Autonomous AI agents are transforming security. We predict 5 critical 2026 threats: IPI, agentic web attacks, and the MCP target. Discover agent-native defences

The State of AI Agent Security 2026
Discover how enterprises are addressing AI Agent Security. Learn key risks, incidents, and insights from NeuralTrust’s 2026 global survey on Agentic Security..

OpenAI Atlas Omnibox Prompt Injection
NeuralTrust research shows how strings that look like URLs can override user intent and jailbreak agentic browsers such as OpenAI Atlas.

AI Agent Security: How to Protect Autonomous Systems
Discover how to protect your AI agents from prompt injection, tool abuse, and data leaks with identity boundaries, policy enforcement, and runtime monitoring.

Self-fixing AI agents: already here?
A researcher unintentionally uncovered what appears to be the first case of an AI model debugging itself, a glimpse into the future of self-maintaining AI
NeuralTrust recognized as Representative Vendor by Gartner Market Guide for AI Gateways
NeuralTrust has been recognized as a Representative Vendor in Gartner’s Market Guide for AI Gateways, highlighting its leadership in secure AI infrastructure.

AI-Driven Supply Chain Attacks in 2026
AI now automates supply chain breaches. See how these attacks work and the defense strategies that secure your vendor ecosystem in 2026.

GPT-5 Jailbreak: Echo Chamber Attack
NeuralTrust jailbroke GPT-5 within 24 hours using Echo Chamber and Storytelling. See how it works and what it means for enterprise security.

Offensive vs. Defensive AI Security
Learn the key differences between offensive and defensive AI security and how to combine them to secure your GenAI stack effectively.

TSA Airport Cybersecurity Warning & AI Threats 2026
The TSA's airport cybersecurity warnings now extend to AI threats: prompt injection, biometric fraud, and AI agent manipulation. Here's what airports and passengers must know in 2026.

The New Cybersecurity Jobs in the Age of AI
Explore the top AI-era cybersecurity jobs, the skills in demand, and how GenAI is reshaping careers in offensive and defensive security.

What the New US AI Law Means for Real Deployments
A new U.S. Executive Order bans AI models with built-in ideological bias from federal use. Learn what the law says, who it impacts, and how vendors can stay compliant.

6 Ways to Scale Trust in AI Outreach
Generic AI outreach kills replies. Learn 6 ways to build trust, scale personalization and book more quality meetings without sounding like a bot.

Grok-4 Jailbreak: Echo Chamber Explained
NeuralTrust researchers jailbroke Grok-4 just 48 hours after launch using Echo Chamber and Crescendo. See the success rates and what it means for enterprise AI.

AI Compliance Policy in the US: The 2026 Essential Guide
Navigate the US AI compliance landscape in 2026. Our guide covers federal actions, state laws, and essential strategies for responsible AI governance

A CISO’s Guide to Generative AI Security in Retail
Retail CISOs face new GenAI risks. Learn how to secure AI systems across supply chains, assistants, and surveillance to protect your enterprise.
NeuralTrust Uncovers Echo Chamber Attack: A Critical Jailbreak Bypassing LLM Guardrails
NeuralTrust uncovers the "Echo Chamber Attack," a new jailbreak that manipulates conversations to bypass the safety guardrails of leading LLMs like GPT-4o.

Echo Chamber: A Context-Poisoning Jailbreak That Bypasses LLM Guardrails
An AI Researcher at Neural Trust has discovered a novel jailbreak technique that defeats the safety mechanisms of today’s most advanced LLMs

McKinsey's Agentic AI Vision: the AI Control Plane
Building on McKinsey's agentic AI vision, we define the AI Control Plane: the critical layer for managing risk and ensuring secure enterprise AI.

Open-Source LLM Pipeline Security & Fairness Guide
Learn how to audit your LLM pipeline for security and fairness using open-source tools for red teaming, evaluation, and bias detection.

How NeuralTrust Helped a Leading Telco Adopt AI Securely
This success story details how a major telecommunications provider used NeuralTrust to deploy a production chatbot safely and with full observability.

NeuralTrust wins two awards at South Summit 2025
The Barcelona-based startup was named “Most Scalable Startup” and “Best Trust Tech & Data Startup,” highlighting its role in safe AI adoption and compliance.

Prompt Injection Detection for LLM Apps
Set up prompt injection detection across your LLM stack: real-time alerting, behavioral analysis, testing and incident response in one guide.

Evaluating GenAI risk: a CISO's guide to AI security
Our guide details for CISOs threats like prompt injection & data leaks, integrating AI security into your frameworks for secure LLM deployment.

GenAI Security for Insurance Companies
Secure GenAI in insurance: Uncover risks to customer data & models, explore compliance, & see how NeuralTrust helps insurers mitigate threats.

How to implement and deploy AI safely
AI deployment strategies for enterprises: learn how to implement AI agents, chatbots, and copilots securely while avoiding risks and ensuring compliance.

A Guide to Generative AI Security in Healthcare
Secure generative AI in healthcare. Learn key risks (PHI, HIPAA), regulatory challenges & best practices for patient data protection & compliance.

Prompt Injection: Attacks & Defenses 2026
How prompt injection hijacks LLM apps: direct vs indirect attacks, real exploit examples and the layered defenses that hold up in production.

GenAI Use Case Checklist: Go or No-Go
Use this checklist to decide if a generative AI use case is worth it. Assess risk, alignment, ROI and compliance in minutes.

GenAI Security for Airlines
Airlines face new GenAI threats. Learn how to protect aviation systems from prompt injection, data poisoning and other AI risks.

NeuralTrust Finalist at South Summit Madrid 2025
We’re thrilled to announce that NeuralTrust has been selected as one of just 100 finalists in the South Summit Madrid 2025 Startup Competition

Crescendo Attack: Gradual LLM Jailbreaks
How the Crescendo attack jailbreaks LLMs step by step. See NeuralTrust's research, test results on popular models and how to protect your AI.

GenAI Security for Banks (2026 Guide)
How banks can secure generative AI: emerging threats, compliance requirements and practical controls for financial institutions in 2026.

AI Fraud Detection in Finance
Discover how AI-powered fraud detection boosts financial security, reduces false positives, and ensures compliance in a rapidly evolving threat landscape.

How to Prepare Your Workplace for AI Integration
Discover key challenges and strategies for integrating AI at work safely. Prepare your workforce and organization for an AI-driven future.
Why Your LLM Applications Need Active Alerting
Discover why real-time alerting is critical for LLM applications. Learn how active monitoring prevents hallucinations, security risks, and performance failures.

Why Manual Testing Is Failing Your LLMs
Manual LLM testing misses key risks. Discover why automated, scalable evaluation & security testing ensure reliable, trustworthy AI

Cybersecurity in Catalonia: NeuralTrust at new report launch
NeuralTrust was honored to participate today in the official launch of the comprehensive industry report, "Cybersecurity in Catalonia".

Benchmarking Jailbreak Detection Solutions for LLMs
Benchmarking LLM jailbreak detectors: compare Amazon Bedrock, Azure and NeuralTrust on private & public datasets—accuracy, F1-score and execution speed

How to Secure Internal AI Assistants and Copilots
This guide details pragmatic strategies to secure internal AI assistants and copilots, ensuring reliability, security, and trust with real examples.

How to Secure External Chatbots
Learn how to secure external chatbots from prompt injection, data leaks, API abuse, and more. Protect your generative AI assets with practical strategies.

Explainability and Transparency: The Key to Trust in AI
Learn why explainability and transparency are key to trusted enterprise AI. Explore challenges, strategies, and how NeuralTrust enables responsible AI use.

AI-Powered IoT Security for Devices
Secure connected devices with AI-powered defense: observability, real-time threat detection and practical steps for IoT and AI ecosystems.

Readability Analysis for LLMs in English
Compare Flesch, Linsear Write & ARI readability metrics for English. See how they assess text complexity & improve LLM accessibility. Code & results.

Language Detection: A Comparative Analysis Approaches
Which language detection model handles short text best? We compare spaCy vs XLM-RoBERTa performance, accuracy, speed & provide implementation examples.

AI in Healthcare: Protect Patient Data
Secure PHI in healthcare AI systems: HIPAA compliance, privacy threats and practical controls to protect patient data in AI workflows.

AI Ethics: Balancing Innovation and Risk
How to build ethical AI practices without slowing innovation: governance, accountability and responsible AI steps for enterprise teams.

NeuralTrust to Exhibit at Barcelona Cybersecurity Congress 2025
NeuralTrust will be exhibiting at the Barcelona Cybersecurity Congress (BCC) 2025, held from May 13 to 15 at the Fira de Barcelona Gran Via.

The Role of AI in Strengthening Supply Chain Security
Discover how AI is revolutionizing supply chain security through advanced threat detection, anomaly monitoring, predictive risk management, and compliance.

The Risk of AI Hallucinations: How to Protect Your Brand
AI hallucinations aren’t just glitches, they’re brand liabilities. Learn how generative models go off-script, what’s at stake, and how to protect your business.

Why Your AI Model Might Be Leaking Sensitive Data
Sensitive data leaks through LLMs are no longer hypothetical. Learn how AI models expose confidential information and how to stop it with concrete strategies.

The Ultimate AI Compliance Checklist for 2026
With new AI regulations from the EU to the USA, this 2026 AI compliance checklist covers everything from model documentation to risk disclosures.

NeuralTrust to Exhibit at OWASP Global AppSec EU 2025 in Barcelona
NeuralTrust is exhibiting at OWASP Global AppSec EU 2025 in Barcelona, Europe’s leading conference on application security and secure software development.

The 10 Most Critical AI Security Risks in 2026
Discover the top 10 AI security risks threatening enterprises in 2026 and learn how to identify, mitigate, and prevent these attacks with proven strategies.

Chatbots Are Becoming the New Attack Surface for Hackers
AI chatbots are the new attack surface. Learn how hackers exploit them and what steps businesses must take to secure LLM-powered interfaces.

Code Injection in LLM Applications
Discover how code injection threatens LLM applications and practical strategies to prevent malicious code execution and data access vulnerabilities in AI.

Bedrock Guardrails vs OpenAI: Topic Tests
We benchmarked topic detection in Amazon Bedrock Guardrails and OpenAI. See which one delivers better accuracy, efficiency and scalability.

Topic Detection with Bedrock Guardrails
Implement fast, scalable topic detection with Amazon Bedrock Guardrails for content management, recommendations and search. Step-by-step guide.

Implementing Topic Detection with OpenAI
Learn how to implement topic detection using OpenAI’s language models. This guide walks through a practical approach that achieved 88.1% accuracy.

What is Model Context Protocol (MCP)?
In this article, you will learn how MCP enhances AI capabilities, reduces integration complexity, and supports dynamic, context-aware AI applications.

What are AI Guardrails?
This article explores the technical foundations, types, limitations, and future of AI guardrails in the era of advanced language models.

NeuralTrust at 4YFN 2025
NeuralTrust showcased AI security innovations at 4YFN 2025, highlighting the future of AI protection and compliance in enterprise applications

AI Gateway benchmark: Comparing security and performance
Discover the top AI gateways with our in-depth benchmark, comparing performance, scalability, and security to help you choose the best solution.

AI Gateways vs. API Gateways: What’s the Difference?
This article explores the distinctions between AI gateways and traditional API gateways, emphasizing the importance of tailored solutions for AI applications

Benchmarking LLM Evaluation Models
Compare NeuralTrust, Ragas, Giskard, and Llama-Index in Evaluation accuracy. Learn about AI benchmarking tools, LLM evaluation metrics, and RAG assessment.

Which firewall best prevents prompt injection attacks?
Protect your AI systems from prompt injection attacks. Compare the best firewalls to block malicious prompts, secure LLMs, and prevent data leaks.

Predictive Threat Intelligence in AI
Learn how predictive threat intelligence enhances cybersecurity by identifying and mitigating risks proactively. Stay ahead of evolving threats.

LLMOps: Scale and Control AI Traffic
Scale AI apps with LLMOps: how caching, routing, cost control and traffic management improve reliability and performance in production.

NeuralTrust at Integrated Systems Europe 2025
NeuralTrust is proud to announce it participated in Integrated Systems Europe (ISE) 2025, held from February 4 to 7 at the Fira de Barcelona Gran Vía

AI-Powered Threat Detection, End to End
How AI-powered threat detection delivers end-to-end protection, better security observability and stronger risk management for enterprises.

Compliance and Governance in AI-Powered Threat Detection
Discover step-by-step strategies to ensure compliance and governance in AI-powered threat detection systems while adhering to regulatory frameworks.

NeuralTrust Joins Plug and Play’s Fintech Breakfast
NeuralTrust joined Plug and Play’s Fintech Breakfast to discuss AI security and the future of fintech innovation

Zero-Trust Security for Generative AI
Learn how to implement a zero-trust framework for AI with continuous verification, least privilege access, and real-time monitoring.

AI Data Protection for GenAI Apps
Protect sensitive data in generative AI apps: AI-specific security controls, data leakage prevention and steps to stay compliant.

NeuralTrust honored as a Finalist at the 22@ Start 2024 Awards
NeuralTrust was honored as a finalist at the 22@ Start 2024 Awards, showcasing cutting-edge AI security solutions in Barcelona's 22@ innovation district.

Secure LLMs from Adversarial Attacks
Key strategies to defend large language models from adversarial attacks such as prompt injection, data poisoning and model extraction.

AI Gateway: Centralized AI Management at Scale
Explore how AI Gateways enhance and scale AI operations with centralized control, risk mitigation, and optimization. Boost your organization's AI capabilities.

Advanced Techniques in AI Red Teaming for LLMs
Discover advanced AI red teaming techniques for LLM security, including adversarial machine learning, ethical hacking, and automated threat intelligence.

AI Compliance Frameworks for GenAI
How to implement AI compliance frameworks for generative AI: map GDPR, the EU AI Act and HIPAA to controls, risk management and security.

What is Red Teaming in AI?
Learn how red teaming protects AI applications, identifies vulnerabilities in generative AI systems, ensuring security, reliability, and compliance.

NeuralTrust at the Madrid Tech Show
Discover NeuralTrust's participation in the Madrid Tech Show, where we discussed secure and responsible AI adoption at Big Data & AI World Spain

Future-Proof AI Security for LLMs
Long-term strategies to future-proof AI security: LLM resilience, risk mitigation and compliance practices for enterprise AI teams.

Preventing Prompt Injection: Strategies for Safer AI
Learn effective methods to safeguard AI models from prompt injection attacks through adversarial training, real-time monitoring, and centralized AI gateways.

AI Gateway vs Guardrails: Key Differences
AI gateways and AI guardrails solve different problems. Compare how each works, where they overlap and which one your AI stack needs first.

AI Model Theft: How to Prevent It
Protect your AI models from theft: key defenses against model extraction attacks and best practices to secure your intellectual property.

AI Governance for Generative AI Systems
How AI governance protects generative AI systems from bias, security threats and misuse while keeping room for innovation and trust.

User Behavior Analytics for AI Chatbots
How user behavior analytics improves AI chatbots and assistants: personalize interactions, lift engagement and measure what works.

NeuralTrust at The Barcelona Deep Tech Summit
We showcased our software solution for companies looking to implement and scale Generative AI safely at The Barcelona Deep Tech Summit.

NeuralTrust: Our Rebranding Explained
Discover the story behind NeuralTrust's rebrand, reflecting our commitment to innovation, AI expertise, and delivering secure, measurable solutions.

How to Prevent LLM Hallucinations (2026)
Practical strategies and advanced techniques to prevent LLM hallucinations and keep generative AI accurate, reliable and trusted.

Measuring the ROI of Generative AI Applications
Learn to measure the ROI of generative AI with key metrics like cost savings, revenue growth, and customer engagement. Maximize the value of AI investments.

New risks in the Era of Generative AI: A Comprehensive Guide
Discover the emerging risks in the era of Generative AI with our comprehensive guide.

Prompt Hacks: The ultimate guide
Unlock the secrets behind Prompt Hacks and how to defend against them.
Agentic AI Security At Runtime
Download the enterprise playbook for securing AI agents in production. Learn how to observe, enforce, detect, and respond to runtime threats before they escalate.
The Agentic AI Security Framework
Agentic AI expands enterprise risk fast. This playbook explains real-world exploits and a security framework for governance, resilience, and compliance.
2025 KuppingerCole Leadership Compass for Generative AI Defense
Download for free one of the first market reports on Generative AI Defense solutions where NeuralTrust has been recognized as a Product and Innovation Leader.
ChatGPT Agent Security: What Dots Change
ChatGPT agent security in 2026: what OpenAI Dots change, admin controls, beta gaps and an 11-point governance checklist for enterprise security teams.
Jev TypeSafe AI: Enterprise Security Guide
Jev TypeSafe AI explained: what the System One model does, vendor-reported speed and cost, prompt injection findings, data terms and how to govern it.
GPT-6 Sol vs Luna: Security, Cost, Routing
GPT-6 Sol vs Luna compared: API prices, cost per task, benchmarks and security data, plus a routing table to pick which OpenAI model to deploy in 2026.
NeuralTrust named in the Gartner Emerging Tech Impact Radar 2026
NeuralTrust, Sample Vendor for AI Application Security in Gartner's Emerging Tech Impact Radar: AI Cybersecurity. What it means for securing AI agents.
NeuralTrust Named a Pioneer in Gartner EMQ for AI Application Security
NeuralTrust has been named a Pioneer in the Gartner Emerging Market Quadrant for AI Application Security, achieving the leading position among all Pioneer vendors. September 2026.
NeuralTrust Opens New London Office as UK Enterprises Race to Secure Their AI Agents
NeuralTrust opens a new London office to help UK enterprises securely deploy, govern and scale AI agents as adoption accelerates across the region.